Federal Bureau of Investigation (FBI) agents have arrested a Canadian cybersecurity executive in Pennsylvania, marking a significant escalation in the federal government’s high-stakes investigation into the prolific hacking collective known as ShinyHunters. The arrest, which took place this past Thursday, comes on the heels of a brazen cyberattack in which the group successfully infiltrated FBI systems, exfiltrating sensitive data pertaining to thousands of bureau personnel.
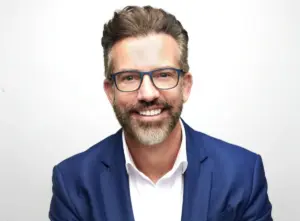
The arrest was first signaled by reports from The New York Times, which confirmed that a Canadian national had been taken into custody on suspicion of providing material assistance to the ShinyHunters operation. While official channels, including a brief statement from FBI Director Kash Patel on X (formerly Twitter), confirmed the apprehension, they stopped short of identifying the individual. However, multiple sources familiar with the federal investigation have confirmed to KrebsOnSecurity that the individual in custody is Edward Dubrovsky, a prominent figure in the Canadian cybersecurity landscape.
A Target at a Cyber Industry Conference
According to details provided by sources close to the investigation, the arrest occurred in Philadelphia while the suspect was attending the Cyber Risk Summit, an industry gathering held at the Loews Philadelphia Hotel between October 5 and October 7. The timing and location suggest that the FBI had been tracking the suspect’s movements with precision.
The suspect’s professional background is deeply rooted in the very industry he is now accused of subverting. His company specialized in the high-stakes world of ransomware negotiation—a niche field that involves acting as an intermediary between corporate victims and the criminal syndicates holding their data hostage. The summit itself, which served as the backdrop for the arrest, lists among its major sponsors several firms in the security sector, including Cypfer, a Canadian organization where Dubrovsky previously held a senior leadership role.
Public records and professional profiles paint a complex picture of the suspect. While his LinkedIn profile previously identified him as a co-founder of Cypfer, a spokesperson for the firm clarified in an update on October 10 that Dubrovsky was never a founder, but rather served as a managing director before his resignation in November 2025. Following his departure from Cypfer, Dubrovsky became associated with CyberSteward, another Canadian security firm that was also a sponsor of the Philadelphia summit. In a social media post published roughly a month prior to the conference, Dubrovsky expressed his intent to attend the summit alongside his colleagues at CyberSteward.

Legal Proceedings and Jurisdictional Shifts
Federal court records reveal that an individual identified as Edward Dobrovsky—noting a slight discrepancy in the spelling of the surname—was arrested in Pennsylvania on October 8. He faces serious charges, including conspiracy to threaten to impair the confidentiality of information with the intent to extort money, and interference with commerce by threats.
While much of the documentation surrounding the case, including the core criminal complaint, remains under seal, filings indexed by CourtListener provide a window into the gravity of the allegations. The records show a swift procedural maneuver on October 9: the case was officially transferred to the Eastern District of Texas. This is a critical development, as multiple sources have confirmed that the Eastern District of Texas has been designated as the centralized hub for the FBI’s sprawling, multi-jurisdictional investigation into the ShinyHunters group.
As of the latest reports, a 54-year-old Edward Dubrovsky is being detained at a federal facility in Philadelphia. Court records indicate that he does not currently have legal representation on record, and the court has yet to appoint a public defender to his case.
The Intersection of Expertise and Extortion
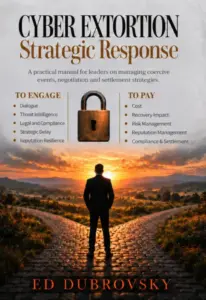
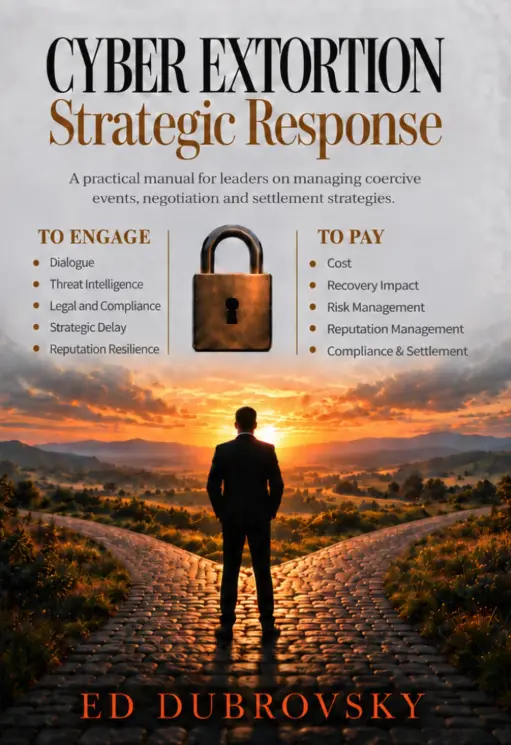
The arrest is particularly noteworthy given the suspect’s specialized knowledge of the ransomware ecosystem. Dubrovsky is the author of Cyber Extortion Strategic Response, a 252-page book that purports to guide organizations through the volatile process of recovering from ransomware attacks. The book’s promotional material highlights the fine line between communication and capitulation, noting that engagement with cybercriminals is often necessary to test claims, gather intelligence, and buy time.
"At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay," an excerpt from the book states. The irony of an expert in defensive negotiation facing charges of participating in the very activities he wrote about has not been lost on industry observers.

Contextualizing the ShinyHunters Threat
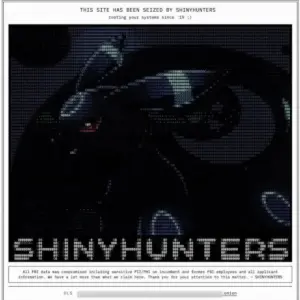
The ShinyHunters group has emerged as one of the most disruptive forces in the cybercrime landscape over the past year. Typically, the group gains access to corporate environments through sophisticated phishing campaigns and the exploitation of stolen credentials, often targeting software-as-a-service (SaaS) providers. Once inside, they siphon massive volumes of proprietary data and issue ransom demands, threatening to leak the information on the dark web if payment is not met. According to internal FBI assessments, the group has successfully extorted over $70 million from victims within this year alone.
The investigation into ShinyHunters has been a volatile, fast-moving operation. It was bolstered significantly last month when Dutch police apprehended Pepijn van der Stap, a convicted cybercriminal, in connection with the group’s activities. The FBI has since been conducting extensive forensic analysis on devices seized during that operation. Sources suggest that the arrest of Dubrovsky may not be the end of the federal sweep, as prosecutors reportedly contemplate additional charges against principals at other firms that operate within the murky waters of ransomware negotiation.
From Recruitment Portals to Aviation Data
The intensity of the FBI’s pursuit of ShinyHunters is largely a result of the group’s recent decision to target the Bureau itself. Following the arrest of Van der Stap, the hacking collective—now operating under the leadership of a member known as "Rey"—began taunting federal authorities. This group managed to compromise the FBI’s own online recruitment portal, obtaining highly sensitive details including medical and psychiatric records of applicants, as well as information regarding their specific units and specializations.
This escalation led to a focused manhunt for "Rey," who was eventually identified as a teenager named Saif Al-din Khader. Last week, news broke that Khader had been detained and was actively cooperating with investigators. Reports indicate that Khader was apprehended as the group attempted to extort a navigation and digital aviation unit formerly part of the Boeing conglomerate.
As the investigation continues, the federal government remains tight-lipped. The FBI has declined to comment on the specifics of the case against the Canadian executive, citing the ongoing nature of the proceedings. For now, the legal system must determine the extent to which the expertise of those tasked with "negotiating" with cyber-extortionists may have crossed the line into active criminal conspiracy. With the case now centralized in Texas and multiple high-profile suspects in custody, the investigation into ShinyHunters is poised to reveal even more about the inner workings of modern cyber-extortion rings.