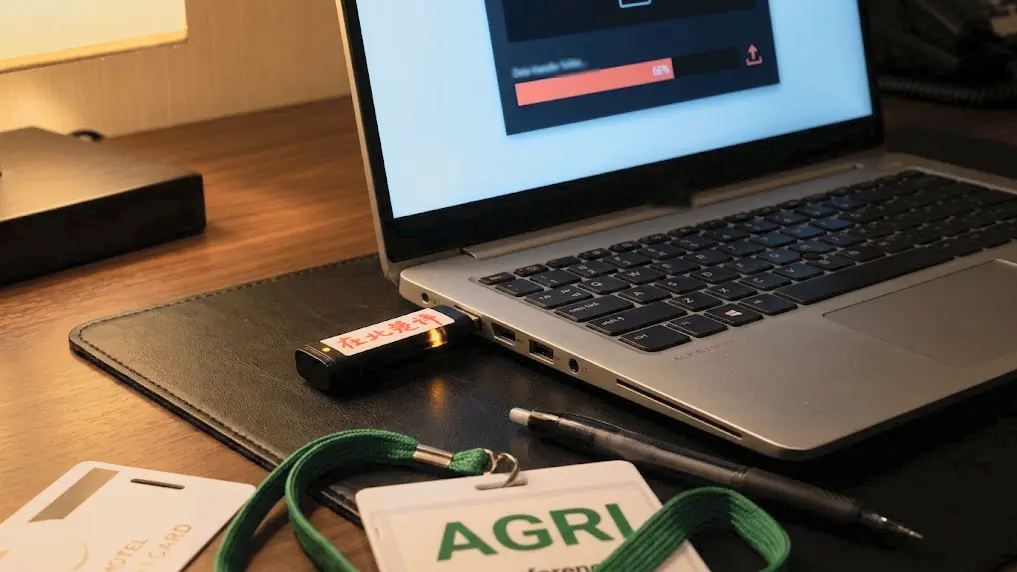
In a stark reminder that the most sophisticated cyber-espionage operations often bypass the digital perimeter entirely, a Chinese state-linked hacking group has been caught compromising executive laptops through direct physical access. The campaign, which took place this spring at an agricultural industry conference on Hainan Island, did not rely on traditional vectors like phishing emails, malicious links, or network vulnerabilities. Instead, attackers gained entry to hotel rooms while the occupants were away at dinner, utilizing bootable USB sticks to implant malware directly onto the machines.
CrowdStrike, which tracks the responsible actor as "OVERCAST PANDA," revealed the details of the operation in its 2026 Threat Hunting Report. Adam Meyers, CrowdStrike’s senior vice president of counter adversary operations, provided additional context during an interview at the company’s Fal.Con 2026 event in Las Vegas, confirming the precise nature of the intrusion. According to the firm’s timeline, the intruders accessed one room at approximately 8 p.m. local time, followed by a second room just before 10 p.m. In each instance, the operatives booted the laptops from an external drive and wrote a backdoor known as "FlowCloud" directly to the storage media before rebooting the devices and exiting the room, leaving no obvious traces of a digital break-in.
A Persistent Threat Exploiting Physical Access
The FlowCloud backdoor is not a new tool in the arsenal of state-sponsored actors. Its origins trace back several years; Proofpoint researchers documented its use as early as 2020, when it was deployed via phishing campaigns targeting the U.S. utilities sector. Furthermore, NTT Security’s Security Operations Center has been tracking USB-delivered infections involving the same malware at the overseas branches of Japanese organizations since the beginning of 2022.
However, the Hainan Island operation represents a significant evolution in tradecraft. Security researchers have long used the term "evil maid attack" to describe the compromise of unattended devices through physical tampering, a concept famously demonstrated by Joanna Rutkowska in 2009. While such attacks are theoretically well-known, they remain remarkably rare among the 290 distinct adversaries monitored by CrowdStrike. While groups like "MUSTANG PANDA" have utilized USB sticks, those campaigns typically rely on the victim themselves to plug in a drive. The OVERCAST PANDA operation is distinct because it combines state-intelligence-level hotel infiltration with a sophisticated, pre-boot malware deployment that requires no user interaction to execute.
When the unsuspecting executives returned to their rooms and powered on their machines the following morning, the trigger fired, initiating the FlowCloud installation. Once the operating system loaded, the malware began its work: capturing keystrokes, recording screen activity, harvesting credentials, and exfiltrating sensitive files. CrowdStrike’s OverWatch team successfully disrupted the intrusions and warned that the group is almost certain to continue these operations.
The Blind Spot in Modern Endpoint Security
The primary challenge posed by this method is that it effectively bypasses the modern security stack. Endpoint Detection and Response (EDR) agents, multi-factor authentication (MFA) protocols, and phishing training are all designed to address threats that occur within a running operating system or via network traffic. Because the initial compromise occurs below the level of the OS and the authentication layer, the malware is already present on the disk before the security software even begins to monitor the environment.
"We have the visibility once the machine boots up," Meyers explained. "A registry key or similar trigger starts FlowCloud sometime after the operating system loads, and that’s when the Falcon sensor picks it up." The critical security gap, therefore, lies in the hours of vulnerability between the initial USB write and the moment the user logs back in, during which the laptop sits in a compromised, yet undetected, state.
Meyers noted that the operation bears the hallmarks of China’s Ministry of State Security. He suggested that the individuals physically entering the rooms were either intelligence officers or hotel staff who had been compromised, bribed, or compelled to cooperate. The choice of an agricultural conference as a target is consistent with the intelligence collection priorities often tied to China’s broader five-year economic and strategic plans. A similar incident occurred in mid-2026, targeting a U.S.-based media professional, further suggesting that this physical tradecraft is being applied across various sectors.
New Frontiers in AI-Driven Cybersecurity
The disclosure of the Hainan campaign coincided with a major product announcement slate at Fal.Con 2026. CrowdStrike introduced a suite of AI-enhanced security tools, including "Falcon Guardian," "SafeMind," the "Agentic Identity Provider," and an "AI Gateway." Nvidia CEO Jensen Huang joined CrowdStrike CEO George Kurtz on stage to unveil SafeMind, an agentic cybersecurity system powered by Nvidia’s Nemotron open models.
The urgency of these tools is underscored by the current threat landscape. Meyers reported to the conference audience that 7,400 Common Vulnerabilities and Exposures (CVEs) were registered in June 2026 alone—a 96% increase compared to June 2025. CrowdStrike itself was responsible for identifying and submitting 2,400 of those vulnerabilities. The company’s data indicates that AI-agent-triggered security leads are growing at two and a half times the rate of human-triggered leads, while cloud-conscious eCrime activity has surged by 171%.
Yet, for all the focus on AI and cloud-native threats, these new technologies are primarily designed to defend against network-based attacks. They assume the existence of a running OS, an active user session, or a live cloud workload—the very conditions that the OVERCAST PANDA hotel operation circumvents.
Bridging the Gap with Firmware and Policy
Addressing the risk of physical compromise requires returning to foundational security principles: firmware integrity and strict hardware policy. CrowdStrike has offered firmware attack detection and BIOS settings auditing within the Falcon sensor since 2019, including integrations that surface BIOS verification telemetry. However, as Meyers pointed out, the technical capability to detect these issues is often underutilized due to the inconvenience of implementing strict hardware policies.
"It’s a solvable problem," Meyers stated. "It’s just an inconvenient solution, which means that a lot of people don’t do it."
Defensive measures include disabling external boot options within the Unified Extensible Firmware Interface (UEFI), setting robust BIOS administrator passwords, and implementing pre-boot authentication. Without these, even full-disk encryption like BitLocker can be vulnerable to physical attacks. Researchers have previously demonstrated that volume master keys can be extracted from the hardware bus using relatively inexpensive equipment if the machine is not protected by pre-boot authentication requiring a PIN or physical key.
Ultimately, the most effective defense remains a change in travel protocol. Meyers advises that employees should never travel with devices containing sensitive information if they are not prepared for those devices to be fully compromised. The use of "burner" laptops and email accounts for international travel—wiped clean upon returning—is a practice he adopted during his own career. He warned that customs and border agencies in various countries have the legal authority to seize devices and compel users to unlock them, providing intelligence services with a straightforward path to sensitive data.
While network-based, AI-powered intrusions are arguably more dangerous because they can be scaled to thousands of targets simultaneously, the physical operation remains a potent tool for high-value targets. Because hotel room intrusions do not scale easily, they are reserved for specific individuals and critical objectives. As long as organizations allow their executives to carry production-capable devices into high-risk environments without hardened firmware configurations, they remain vulnerable to the "evil maid" tactics that bypass even the most advanced AI security suites. Closing this gap is not a matter of purchasing new software, but a matter of discipline, policy, and acknowledging that when an adversary gains physical access to a device, the game has already changed.