Federal authorities have apprehended a high-ranking executive from a Canadian cybersecurity firm in connection with an expansive investigation into the notorious hacking collective known as "ShinyHunters." The arrest, which took place in Pennsylvania this past Thursday, marks a significant escalation in the government’s efforts to dismantle a group that recently embarrassed the Federal Bureau of Investigation (FBI) by successfully exfiltrating sensitive data pertaining to thousands of bureau personnel.
While the FBI has remained largely tight-lipped regarding the specifics of the operation, multiple sources familiar with the matter have confirmed the arrest to KrebsOnSecurity. The development follows a report from The New York Times, which first noted that a Canadian national had been taken into custody in Pennsylvania on suspicion of providing material assistance to the hacking group. FBI Director Kash Patel confirmed the arrest via a brief statement on X (formerly Twitter), though he declined to identify the individual or provide further details regarding the scope of the charges.
The Intersection of Industry and Intrusion
The circumstances surrounding the arrest suggest a sophisticated intersection between the legitimate cybersecurity industry and the criminal underworld. According to a source close to the investigation, the suspect was in Pennsylvania to attend the Cyber Risk Summit, an industry gathering held at the Loews Philadelphia Hotel between October 5 and October 7. The suspect’s firm reportedly specializes in the high-stakes, gray-market business of negotiating ransomware payments on behalf of organizations targeted by cybercriminals.
Public records and conference materials indicate that the event featured several prominent sponsors. Among the largest sponsors listed for the 2026 summit was Cypfer, a Canadian-based security firm. In the aftermath of the arrest, focus shifted toward Edward Dubrovsky, a prominent figure in the Canadian security sector. Dubrovsky, who has been linked to both Cypfer and another security firm, CyberSteward, had publicly stated on LinkedIn roughly one month prior to the conference that he intended to attend the Cyber Risk Summit alongside his colleagues.
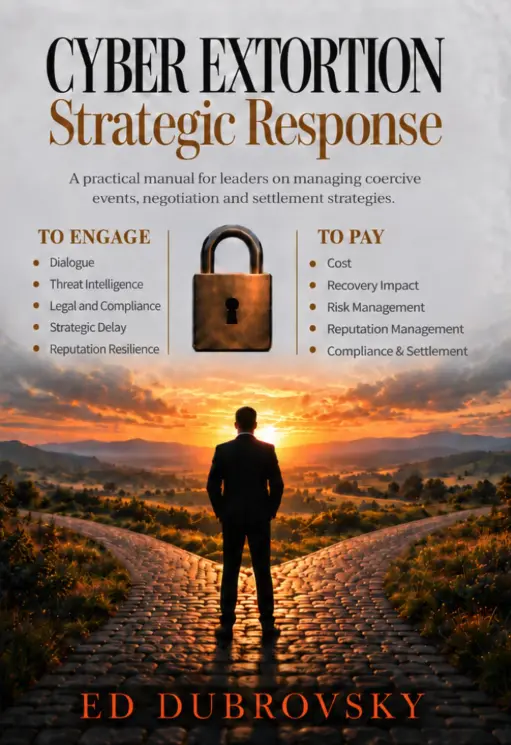
Following the initial reports, a spokesperson for Cypfer clarified that while Dubrovsky’s LinkedIn profile previously identified him as a founder or co-founder, he had actually served as a managing director before resigning from the company in November 2025. Despite this distinction, the professional footprint left by Dubrovsky highlights a career deeply embedded in the mechanics of cyber extortion. He is the author of Cyber Extortion Strategic Response, a 252-page manual that promises to guide organizations through the complex decision-making processes required when facing a ransom demand.

In promotional material for the book, Dubrovsky emphasized the nuance of his trade, writing: "At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay. Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move." It is this very "engagement" that federal prosecutors now allege crossed the line into illegal activity.
Federal Charges and Procedural Shifts
Court records show that on October 8, an individual identified as Edward Dobrovsky—noting a slight variance in the spelling of his surname—was arrested in Pennsylvania. He faces serious charges, including conspiracy to threaten to impair the confidentiality of information with the intent to extort money, and interference with commerce by threats. While many of the core documents remain under seal, summaries indexed by CourtListener provide a glimpse into the gravity of the allegations.
The U.S. Bureau of Prisons inmate locator confirmed that a 54-year-old Edward Dubrovsky is currently being held at a federal facility in Philadelphia. However, in a move that underscores the national importance of the case, a notice filed on October 9 indicated that the proceedings have been transferred to the Eastern District of Texas. Sources indicate that the FBI has centralized its investigation into the ShinyHunters collective at its Texas field office, making it the strategic hub for this multi-jurisdictional effort. As of this writing, Dubrovsky does not appear to have retained legal counsel, and the court has yet to appoint a public defender.
The Shadow of ShinyHunters
The investigation into ShinyHunters comes at a time when the group has become one of the most prolific and brazen threats in the cybercrime landscape. Operating primarily through the exploitation of stolen credentials and sophisticated phishing campaigns, the group specializes in siphoning data from corporate accounts at software-as-a-service (SaaS) providers. Once in possession of the data, they utilize it as leverage, threatening to dump sensitive information on the dark web unless a ransom is paid. According to FBI estimates, the group has successfully extorted over $70 million from victims throughout the current calendar year.
The intensity of the FBI’s pursuit is in no small part a response to the group’s direct assault on the bureau itself. Earlier this year, ShinyHunters compromised the FBI’s own online recruitment portal. The stolen data included highly sensitive personal information, such as the units and specializations of bureau personnel, as well as private medical and psychiatric records.

The investigation has been a fast-moving series of dominoes. Last month, Dutch police arrested Pepijn van der Stap, a convicted cybercriminal, in connection with the same probe. The FBI has reportedly been conducting a deep forensic analysis of devices seized during that operation, leading to expectations that further charges against executives and principals at other ransomware negotiation firms may be imminent.
Following the arrest of Van der Stap, the group’s operations were seemingly taken over by an individual operating under the handle "Rey." This successor engaged in a campaign of taunting the FBI, flaunting the agency’s own stolen data to emphasize the group’s reach. However, the group’s momentum stalled last week when Reuters reported that "Rey"—identified as a teenager named Saif Al-din Khader—had been detained and was actively cooperating with federal investigators.
The apprehension of Khader was reportedly linked to a failed extortion attempt against a navigation and digital aviation unit previously divested by Boeing in late 2025. With the investigation now shifting toward the alleged facilitators and negotiators who may have provided the infrastructure or guidance for such criminal enterprises, the case against Dubrovsky serves as a stark warning to the professional services industry. As the FBI continues to dismantle the network from both the technical and the advisory side, the reach of the ShinyHunters investigation appears poised to expand, potentially implicating a wider circle of actors who have navigated the thin line between corporate security consulting and criminal conspiracy.