In a startling discovery that highlights the pervasive nature of modern cyber risks, security researchers have identified that several devices within the White House’s dedicated internet network are inadvertently acting as residential proxy nodes. This configuration effectively allows unknown third parties to rent the White House’s IP addresses, potentially bypassing security perimeters and masking the true origin of malicious internet traffic.
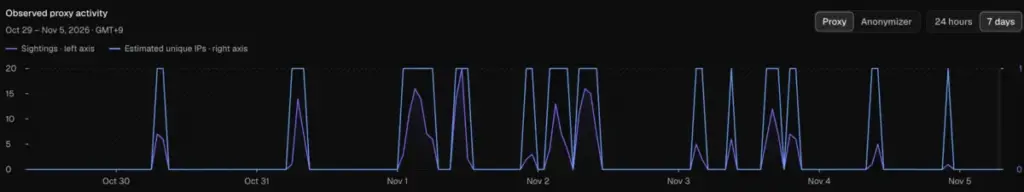
The security firm Layer3 Intel raised the alarm after detecting multiple residential proxy nodes “beaconing” from the internet address network specifically reserved for the Executive Office of the President, identified as AS2650. According to the firm, this unauthorized proxy activity was persistent throughout a month-long observation period, spanning from October 5 to November 3. During that timeframe, Layer3 Intel’s analysis revealed that these proxies exited from the White House network on at least 236 separate occasions.
The implications of this breach are compounded by the origins of the services involved. The proxy tracking firm Synthient confirmed via social media that the traffic emanating from the AS2650 network was tied to multiple Windows 11 installations running a service called Infatica. Infatica is a proxy program frequently bundled into seemingly benign or "free" mobile and desktop applications. The service is led by Vladimir Fomenko, a Russian national whose previous venture, a web hosting company known as King Servers, was infamously linked to the 2016 cyberattacks against election databases in Arizona and Illinois. During those incidents, six of the eight IP addresses utilized by Russian state security services to compromise election infrastructure were traced back to Fomenko’s hosting firm.
The Mechanism of Residential Proxy Exploitation
To understand the severity of this issue, one must understand the function of residential proxy services. These providers operate by turning consumer and corporate devices into “exit nodes.” Once a device is compromised or intentionally enrolled in such a network, its internet connection becomes a relay point for others. Customers of these proxy services pay a fee to route their web traffic through these nodes, effectively cloaking their identity. To any website or service being accessed, the traffic appears to originate from the residence or office of the device owner—in this case, the White House—rather than the actual user of the proxy service.
Layer3 Intel reported that the proxy exit nodes within the White House network were traced to six distinct internet addresses. The activity was highly consistent, occurring on 26 out of the 30 days observed. Notably, much of this traffic occurred during off-hours, specifically between 5 p.m. and midnight, suggesting that the activity may be linked to devices brought into the workplace by staffers or left running after hours.
Perhaps most concerning is that Infatica is not the only culprit. Layer3 Intel discovered that a staggering 28 separate residential proxy services were capable of routing traffic through the White House network.
“This is public access,” the team at Layer3 Intel noted in their report. “Anybody can obtain it by signing up to a public residential proxy service, paying a few dollars, and sending requests through it. We did not selectively target this network or try to make our probes exit from it. We caught this by chance, simply by requesting global rotating access through these services.”
As of the time of reporting, the White House has not provided a comment regarding these findings.
A Broader Ecosystem of Digital Risk
The presence of these proxies within such a high-security environment underscores a growing trend in the cybersecurity landscape. Residential proxy services have become a primary vector for a wide array of illicit activities, including account takeovers, advertising fraud, large-scale content scraping for artificial intelligence model training, and various forms of cybercrime.
Beyond the immediate risk of traffic anonymization, these services introduce significant structural vulnerabilities. In late 2025, researchers identified that cybercriminals were actively exploiting widespread vulnerabilities in proxy software to probe the local networks of the machines they had compromised. By gaining a foothold through the proxy service, attackers could scan the user’s local network—whether it be a home, a corporate office, or a government building—to identify and infect other vulnerable systems with malware.
The danger was further illustrated in January 2026, when Synthient founder Ben Brundage demonstrated how attackers were abusing these vulnerabilities to gain administrative control over devices inside the local networks of unsuspecting users. Following this disclosure, numerous proxy providers were forced to issue emergency patches to their networks.
“Some of these resellers sell bandwidth for as low as 60 cents a gigabyte; that means for less than a dollar, you can gain access into some of the most confidential and trusted networks,” Brundage told KrebsOnSecurity. “The reseller ecosystem further enables this, with any criminal able to buy access while skipping KYC [Know Your Customer] processes.”
The Prevalence of “Shadow” Network Access
The root cause of this exposure often lies in the software installed on employee devices. Developers of seemingly innocent applications—ranging from productivity tools to games—often embed software development kits (SDKs) provided by residential proxy networks. These SDKs monetize the software by turning the user’s device into a proxy node, providing the developer with a small financial kickback for every installation. When these devices are brought into secure environments like government offices, the proxy node becomes an unintentional bridge into the organization’s internal network.
The scale of this issue is not limited to the White House. The practice of devices acting as residential proxies has been found across nearly every sector of critical infrastructure. In a webinar conducted in January 2026, the proxy tracking service Spur identified residential proxy activity in nearly 300 government-operated networks, as well as 318 utility companies, 166 healthcare institutions, and 141 firms within the banking and finance sectors. Furthermore, the security firm Infoblox reported that approximately 65% of its customer base had been observed querying domains associated with residential proxy services, indicating that the phenomenon is both widespread and largely unchecked.
As organizations grapple with the challenges of remote work and the integration of third-party software, the case of the White House network serves as a stark reminder that even the most secure facilities can be undermined by the silent, often invisible, presence of proxy services running on everyday hardware. With the barrier to entry for such access costing less than a dollar, the security implications for sensitive government and corporate entities remain a pressing concern for network administrators and policymakers alike.