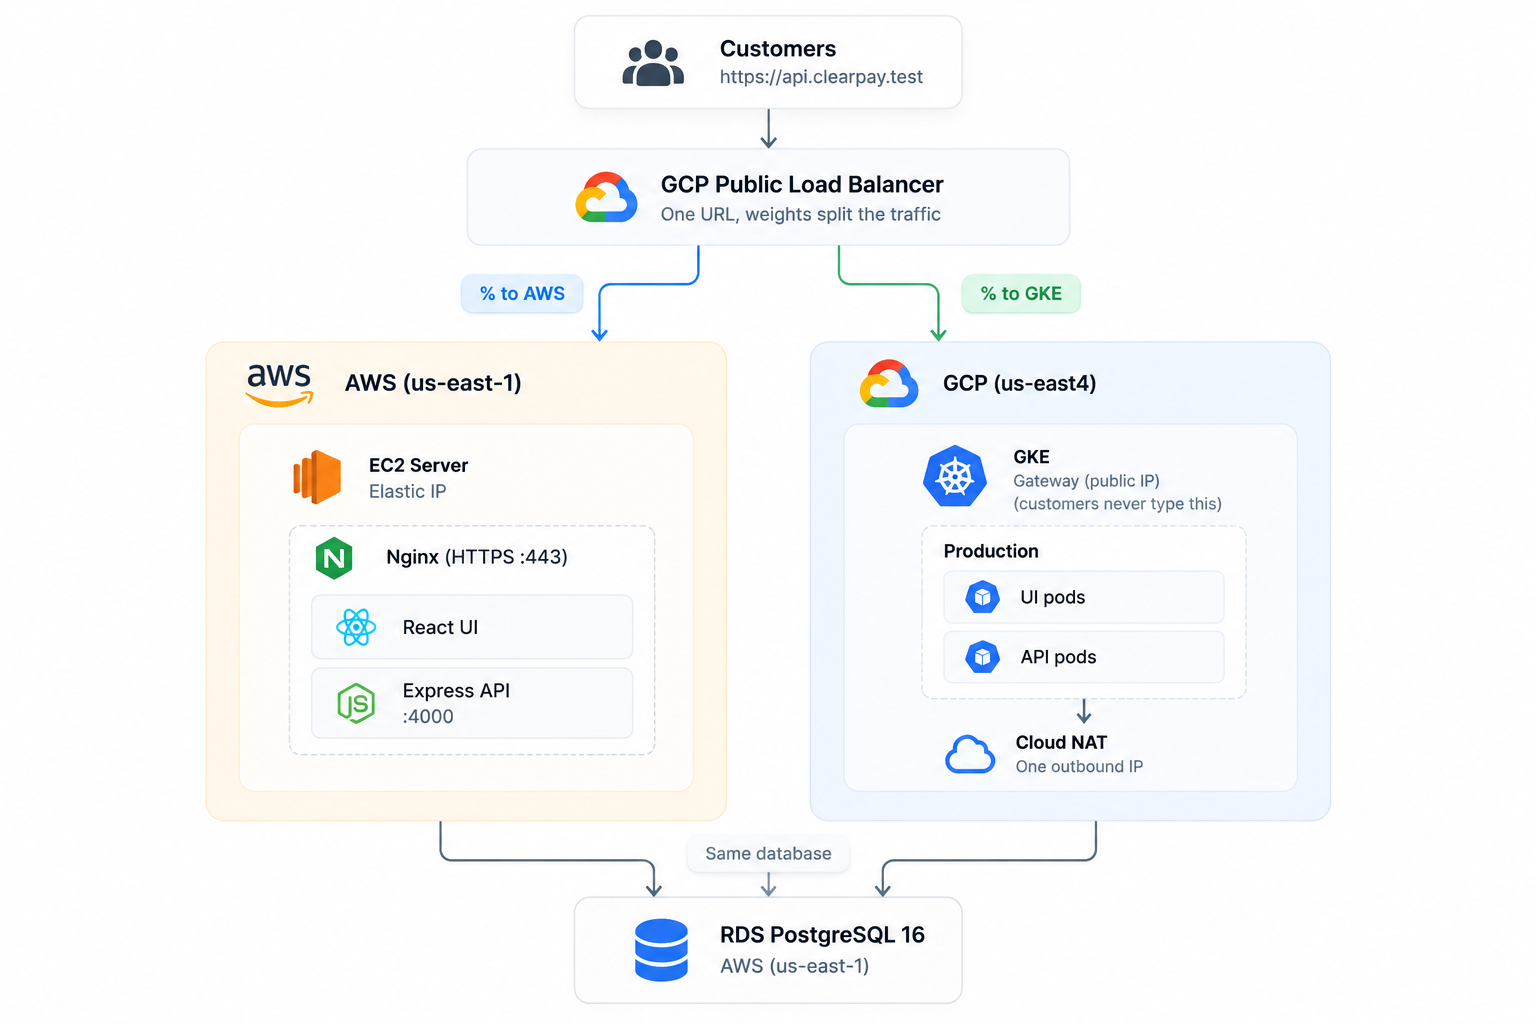
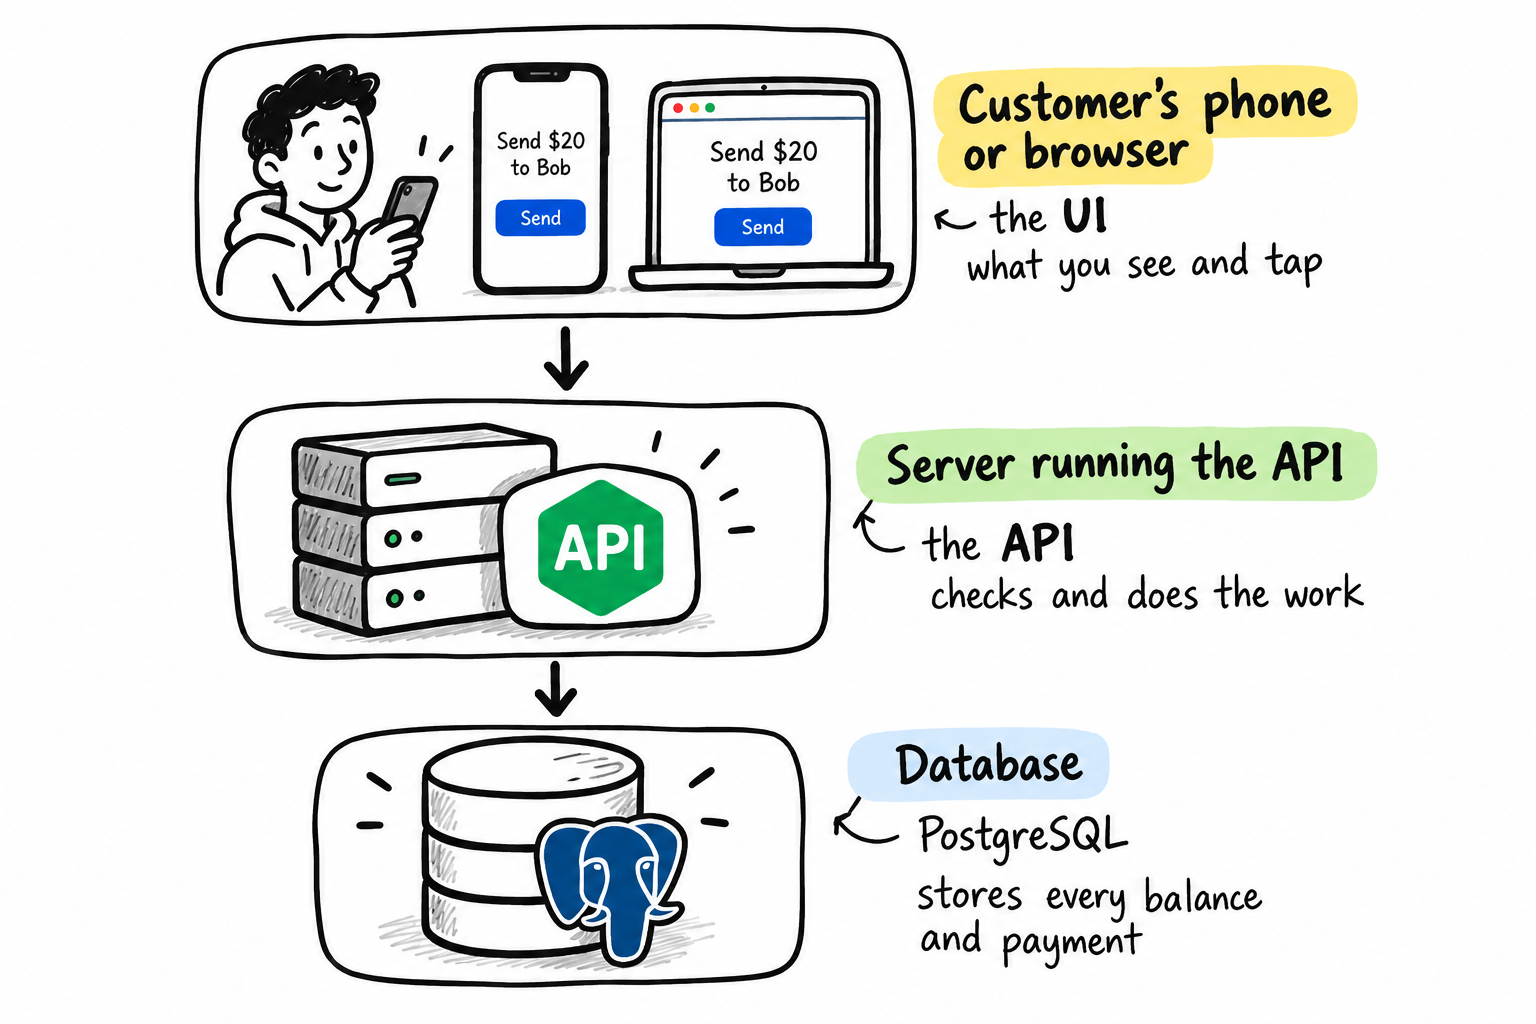
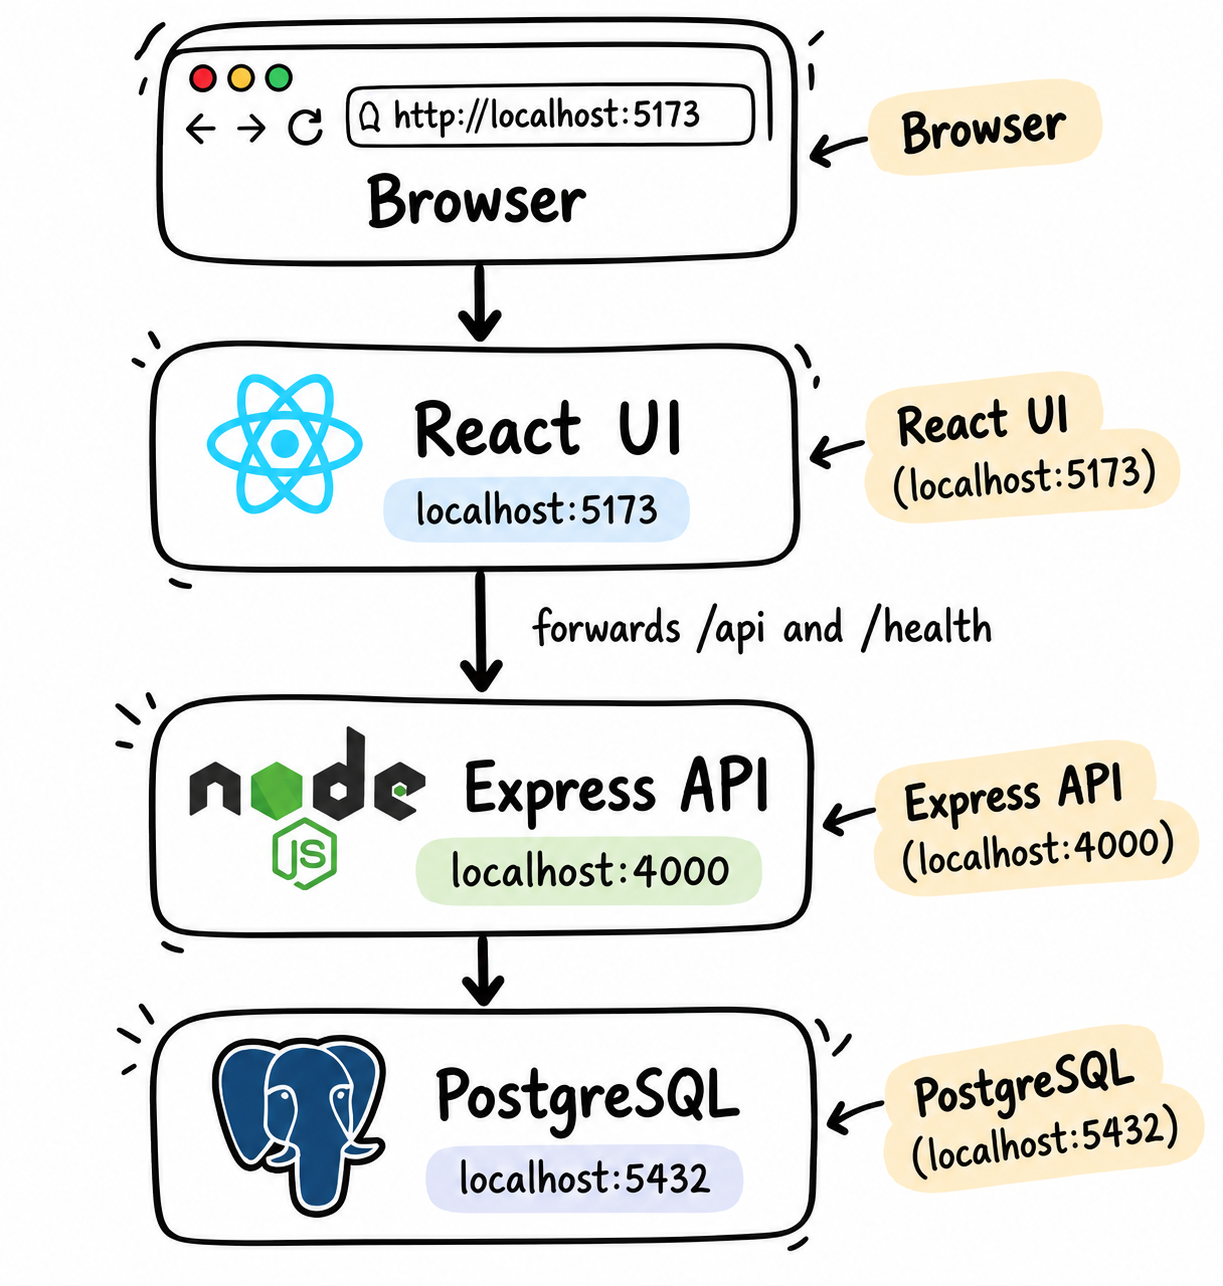
An engineering team has published a comprehensive manual detailing the complete architectural process of migrating a production-grade application from Amazon Web Services (AWS) to Google Kubernetes Engine (GKE). The comprehensive project blueprint walks engineering teams through the complex lifecycle of moving an Express API and React frontend running on an EC2 instance into a containerized Kubernetes environment, all while keeping the backend PostgreSQL database securely hosted on AWS.
The guided publication addresses a fundamental challenge faced by enterprise engineering organizations: how to modernize infrastructure without triggering user-facing downtime or undertaking the immense risk of migrating the database simultaneously. According to the architecture plan outlined in the manual, the migration relies on maintaining a dual-cloud environment where the application layer is progressively shifted using weighted traffic routing, giving teams a reliable mechanism to roll back instantly if unexpected failures occur.
Setting Up and Establishing the Baseline
The project begins by running the sample application, a payments platform named ClearPay, locally using Docker Compose to establish a trustworthy functional baseline. Engineers are instructed to verify core transactional mechanisms, such as API health checks, user authentication, and transaction workflows, before touching any cloud resources.
Following local validation, the manual details the provisioning of an AWS infrastructure using Terraform. Instead of jumping straight into complex architectures, the initial state replicates a standard enterprise setup: a single Ubuntu EC2 server managed via systemd and nginx, paired with an Amazon RDS PostgreSQL instance configured with a private endpoint. Once deployed, engineers record a comprehensive performance scorecard—including p50, p95, and p99 latency metrics, throughput, and error rates—which serves as the benchmark against which the subsequent Google Cloud environment is measured.
Designing and Provisioning the Google Cloud Environment
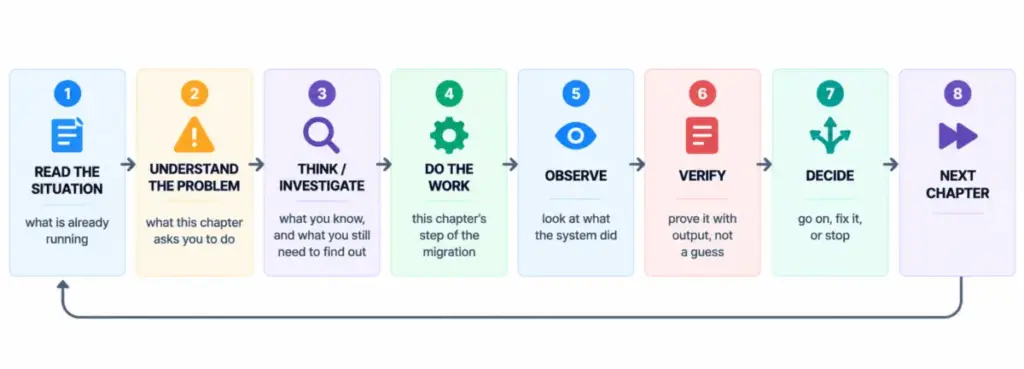
Before containerizing or deploying applications to Google Cloud, the blueprint mandates a structured eight-stage Terraform provisioning process. This systematic approach ensures that dependencies are built sequentially and verified at each layer. Stage one enables necessary Google Cloud APIs, followed by stage two, which provisions a custom Virtual Private Cloud (VPC) subnet and a Cloud NAT gateway to handle secure outbound internet access for private cluster nodes.
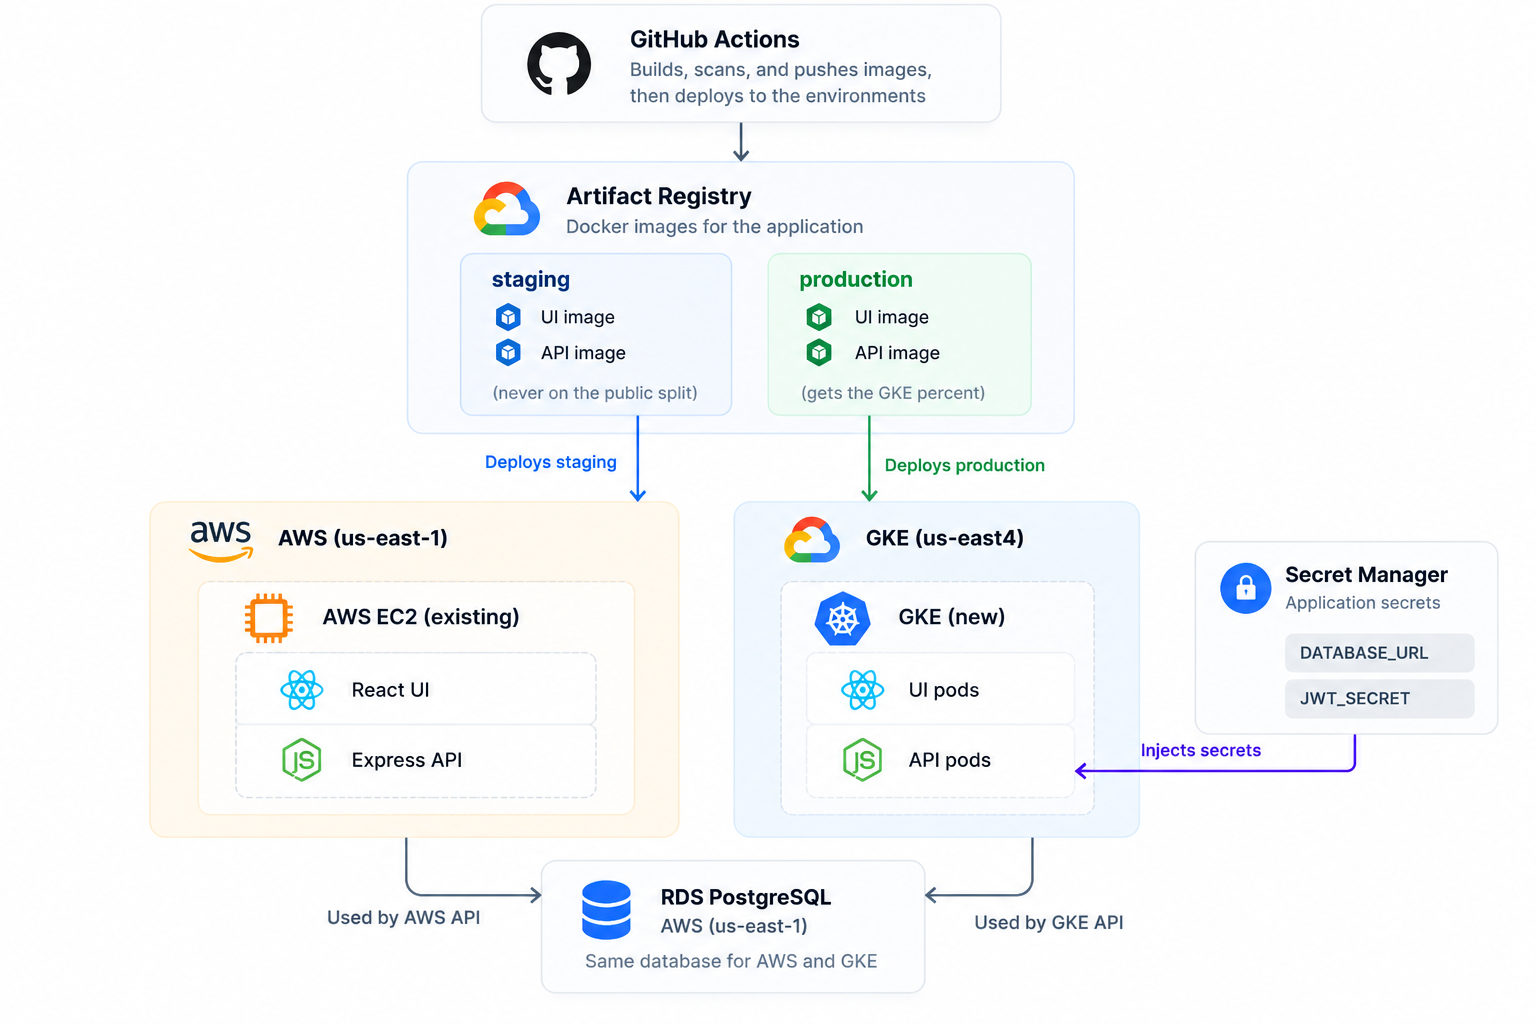
Subsequent stages build a private GKE Standard cluster, configure an Artifact Registry for container images, establish identity and access management using Workload Identity Federation without storing static service account key files, and set up Secret Manager to securely sync configuration data. Observability metrics and error-counting logs are configured in stage seven, while stage eight establishes the public global load balancer with an initial traffic split of 100 percent to AWS and 0 percent to GKE.
Deploying to Staging and Executing Production Gates
With the underlying infrastructure established, container images for the React UI and Express API are built and pushed through an automated GitHub Actions CI/CD pipeline. The pipeline incorporates automated security vulnerability scanning via Trivy and uses OIDC tokens to authenticate with Google Cloud securely, eliminating long-lived credentials.
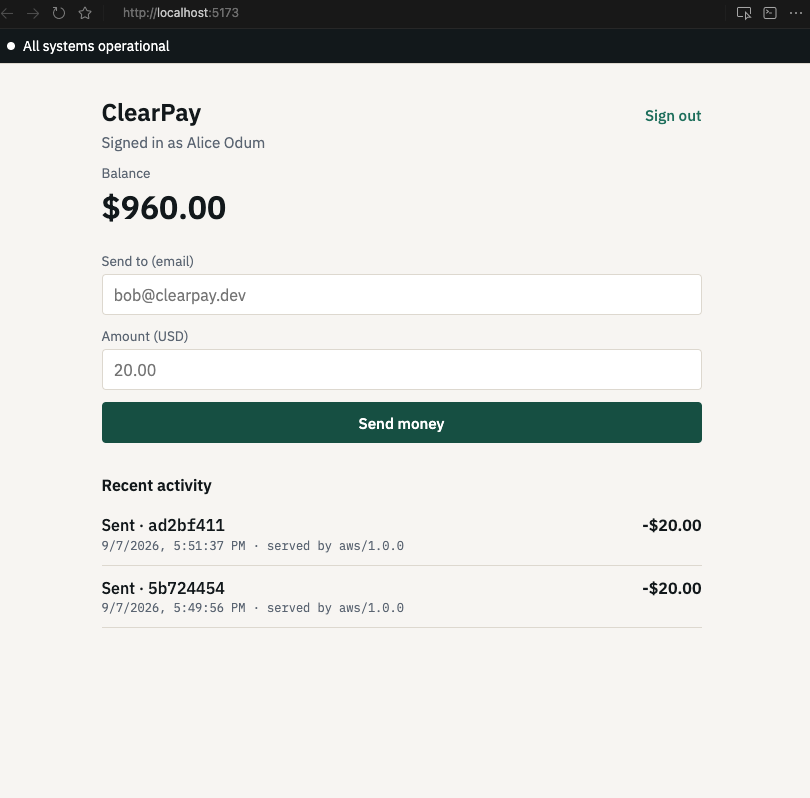
Once the application is deployed to the GKE staging namespace, verification moves beyond simple container health checks. Engineers must execute an automated promotion gate script that exercises the core business logic: testing database connectivity, verifying token-based authentication, and proving that transaction retries using idempotency keys correctly prevent duplicate financial debits. This guarantees that a payment request sent multiple times due to a dropped connection results in a single charge, even when requests are distributed across cloud providers sharing the same backend database.
Managing the Traffic Shift and Ensuring Production Readiness
Prior to routing production traffic, the documentation emphasizes rigorous security reviews and failure testing. Teams verify that database traffic is encrypted via TLS, audit logs are active, and least-privilege permissions are enforced across namespaces. Furthermore, engineers conduct load-testing evaluations against staging and deliberately terminate active application pods to measure cluster resilience and automated recovery times.
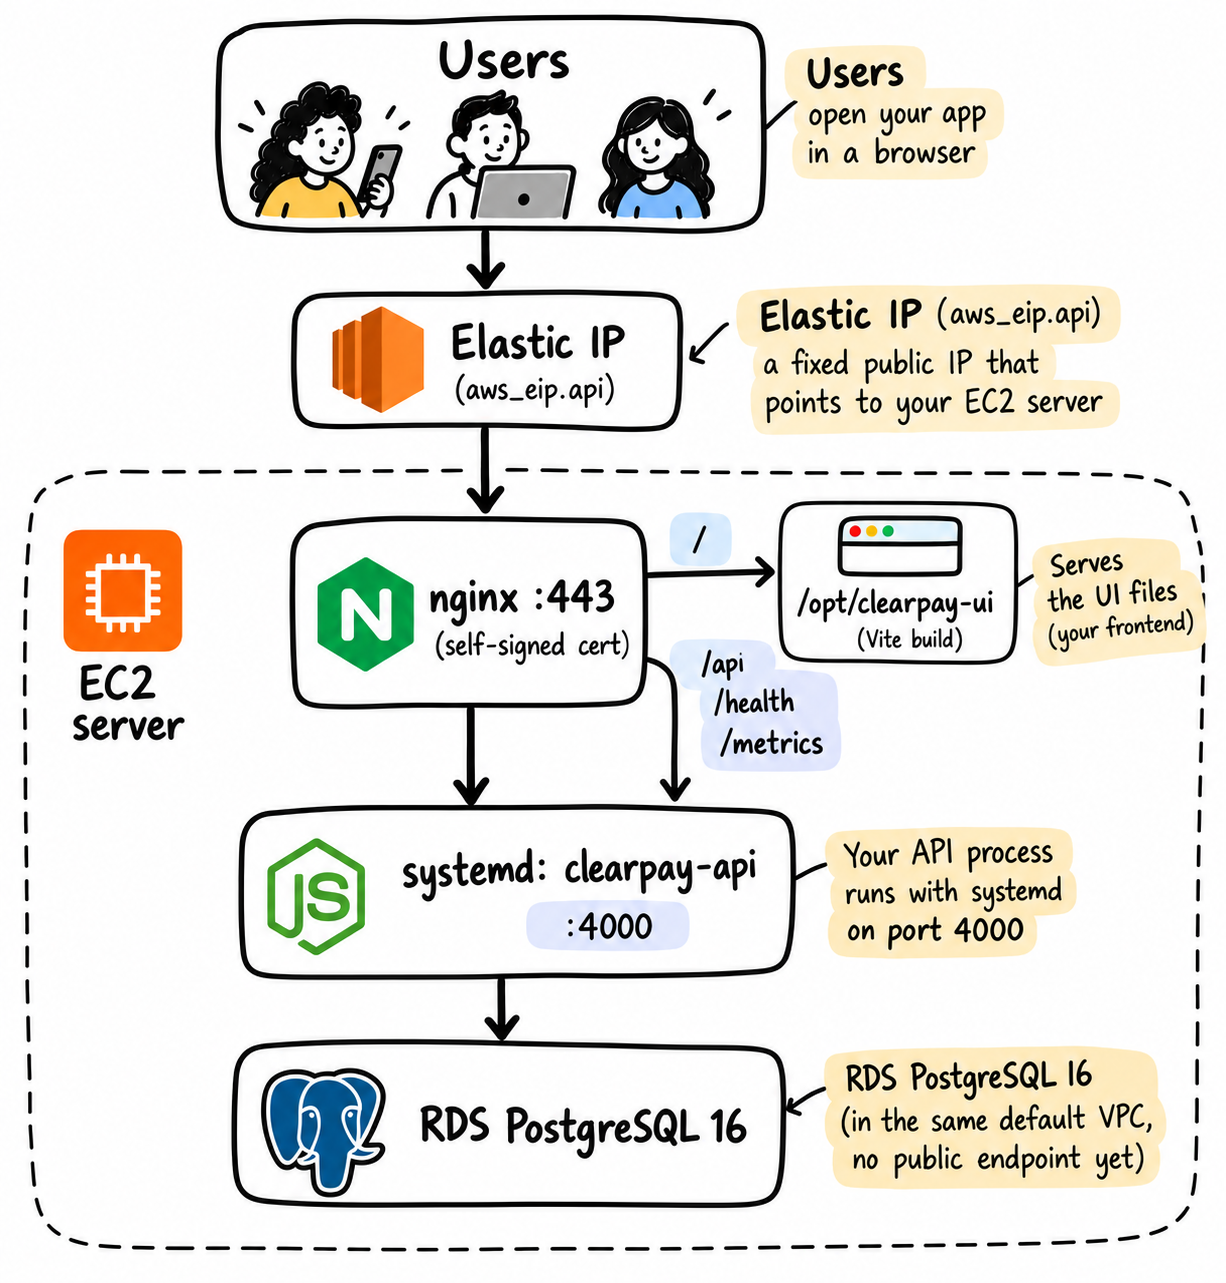
When production deployment commences on GKE using the Gateway API, traffic migration is intentionally executed through gradual increments—starting at one percent, moving to ten percent, twenty-five percent, fifty percent, and beyond. Throughout this transition, operations teams monitor error rates, latency histograms, and database connection pools. Because both AWS and GKE instances connect to the same PostgreSQL database simultaneously, careful capacity planning is required to ensure that the combined maximum connection counts from all active container replicas do not exceed the database server’s max_connections limit.
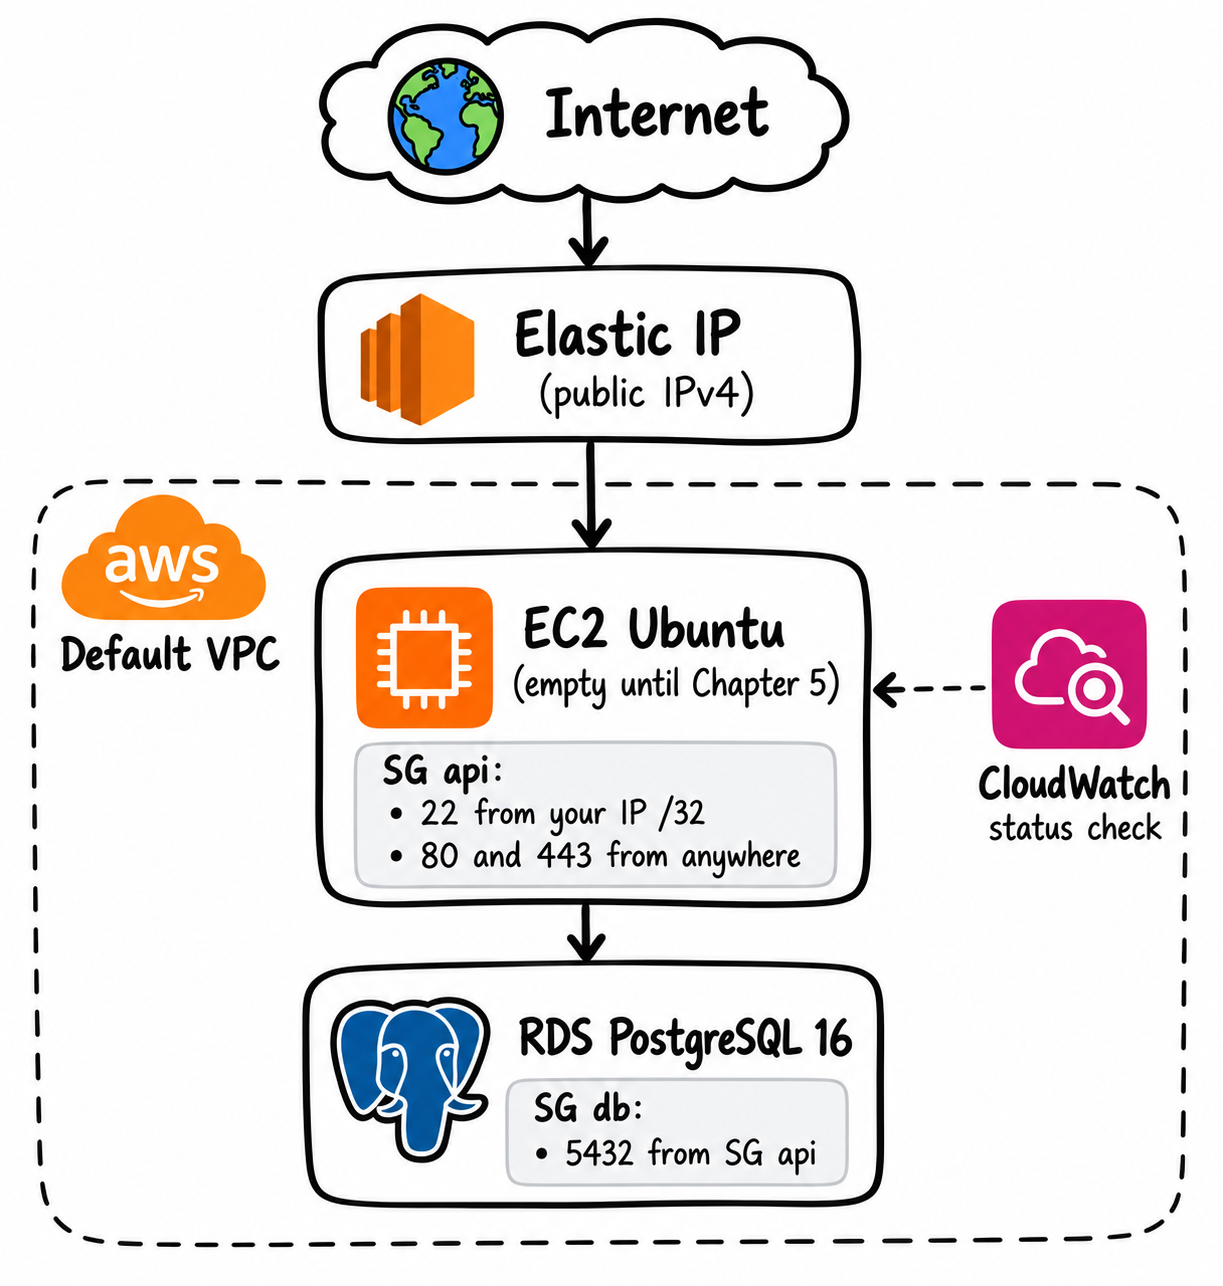
The manual outlines clear incident response protocols, emphasizing that if latency anomalies or error thresholds are breached, the team can instantly execute an automated rollback script to divert 100 percent of traffic back to the AWS infrastructure while displaying a distinct status banner to application users.
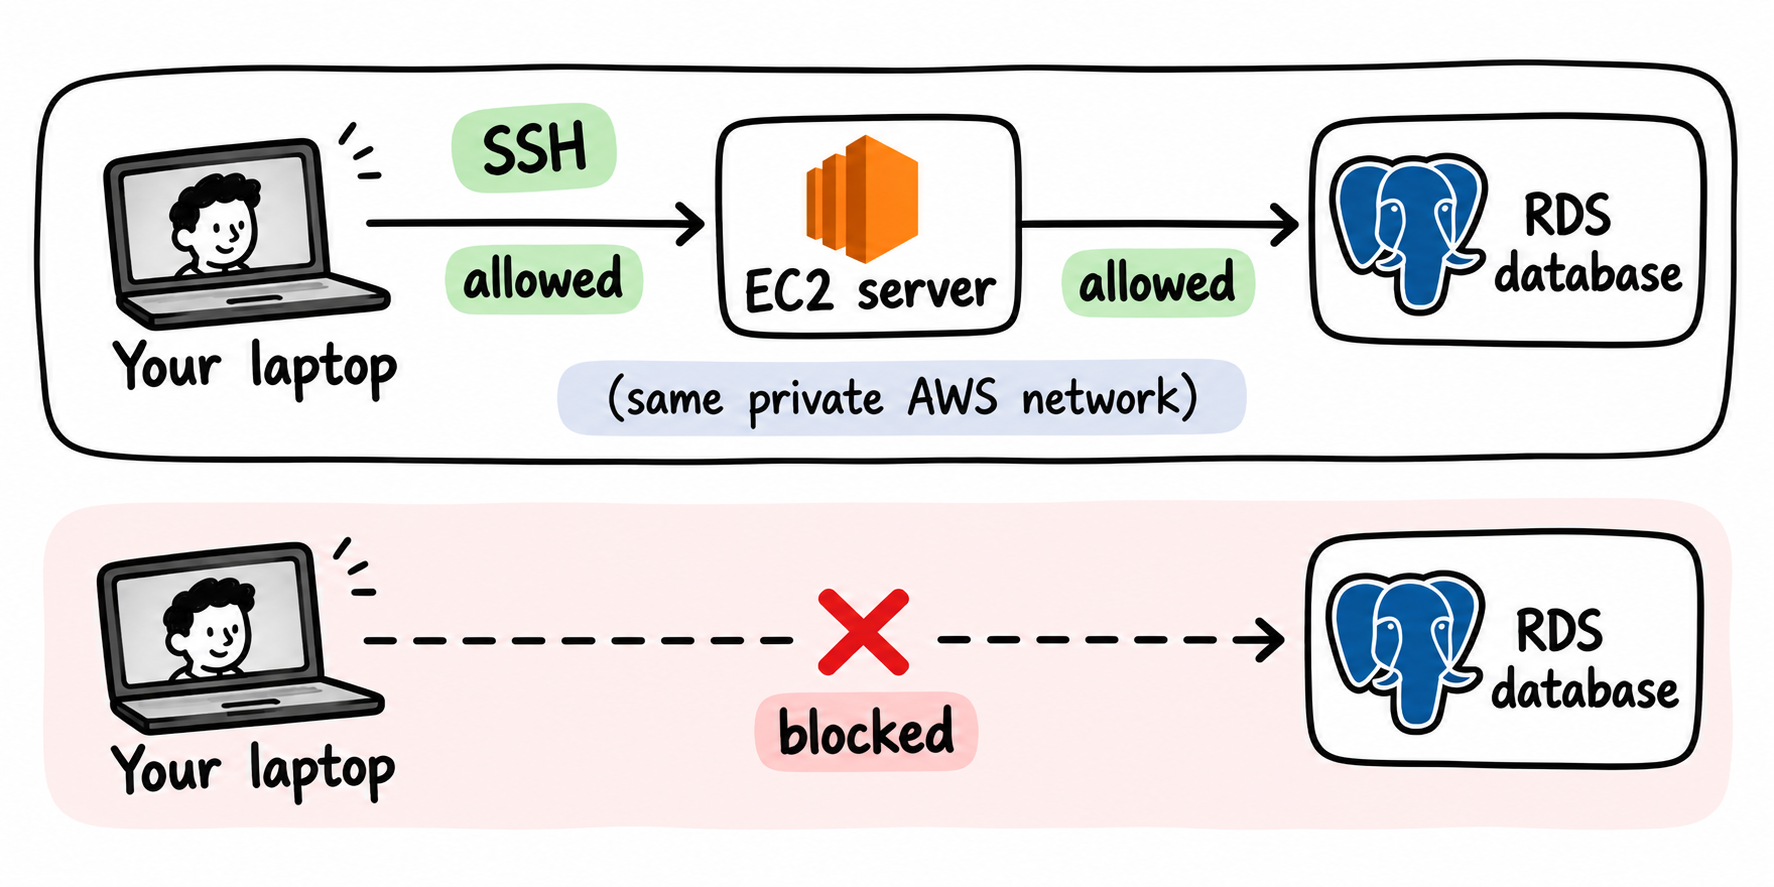
Finalizing the Cutover and Retiring Legacy Infrastructure
Once 100 percent of production traffic is stably served by GKE and comprehensive post-cutover performance metrics confirm that customer experience meets established thresholds, the final phases of the project address infrastructure cleanup. The manual details the systematic decommissioning of the legacy AWS EC2 compute instances, security groups, and elastic IP addresses using targeted Terraform destroy scripts.
Meanwhile, the PostgreSQL database remains on AWS as a deliberate architectural boundary, deferring database migration to a subsequent, dedicated project lifecycle. By isolating the application migration from the data layer, the framework demonstrates how enterprise engineering teams can successfully execute complex multi-cloud migrations while maintaining strict operational visibility, predictable rollback capabilities, and continuous service availability.