










In a significant escalation of the federal government’s crackdown on digital extortionists, agents with the Federal Bureau of Investigation (FBI) have arrested a high-profile executive at a Canadian cybersecurity firm. The arrest, which took place in Pennsylvania on Thursday, is directly connected to the ongoing investigation into the notorious hacking collective known as "ShinyHunters," a group that has recently targeted the FBI itself, allegedly compromising sensitive data belonging to thousands of federal agents.
While the FBI has remained tight-lipped regarding the specifics of the operation, the arrest was confirmed by multiple sources close to the investigation. The news was first brought to the public eye by The New York Times, which reported that a Canadian national was taken into custody in Pennsylvania on suspicion of providing material assistance to the ShinyHunters group. Although the FBI’s official channels have been cautious, FBI Director Kash Patel issued a statement on X (formerly Twitter) confirming that an arrest had been made, though he declined to name the individual or provide granular details about the charges.
The Intersection of Industry and Intrusion
Sources familiar with the case revealed that the suspect was in Pennsylvania to attend the Cyber Risk Summit, a high-level industry gathering held at the Loews Philadelphia Hotel between October 5 and October 7. The suspect, identified in federal court records as Edward Dubrovsky, reportedly held a prominent role in the cybersecurity sector, with his professional background focused heavily on ransomware negotiations.
According to conference materials, the summit featured a range of industry leaders and sponsors, with a Canadian security company known as Cypfer listed as the event’s primary sponsor. Dubrovsky, who has maintained a high profile in the cybersecurity community—including authoring a book on the strategic response to cyber extortion—was previously associated with Cypfer. However, a spokesperson for the firm clarified in an update on October 10 that Dubrovsky was not a founder or co-founder, as his LinkedIn profile had previously claimed, but had served as a managing director until his resignation in November 2025. Following his departure, Dubrovsky moved to another Canadian firm, CyberSteward, which also acted as a sponsor for the summit. In a post on LinkedIn roughly one month prior to his arrest, Dubrovsky had publicly expressed his intention to attend the Philadelphia event alongside his new team.
Legal Proceedings and Jurisdictional Shifts
Federal court records reveal that an individual named Edward Dobrovsky (a spelling variation of the suspect’s name) was arrested on October 8 on charges of cyber extortion and conspiracy. While much of the core complaint remains under seal to protect the integrity of the ongoing investigation, summaries indexed by CourtListener.com indicate that the charges include "conspiracy to threaten to impair the confidentiality of information with the intent to extort money" and "interference with commerce by threats."

As of Friday morning, the U.S. Bureau of Prisons inmate locator confirmed that a 54-year-old Edward Dubrovsky was being held at a federal facility in Philadelphia. However, the legal landscape of the case is shifting rapidly. A notice filed on October 9 indicated that the proceedings have been moved to the Eastern District of Texas. Sources suggest this move is highly significant, as the FBI has centralized its broader investigation into the ShinyHunters group at a field office in Texas, signaling that the arrest of the Canadian executive may be part of a much larger, coordinated offensive against the organization.
Expert Insight or Criminal Complicity?
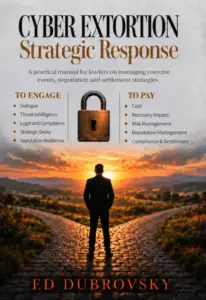
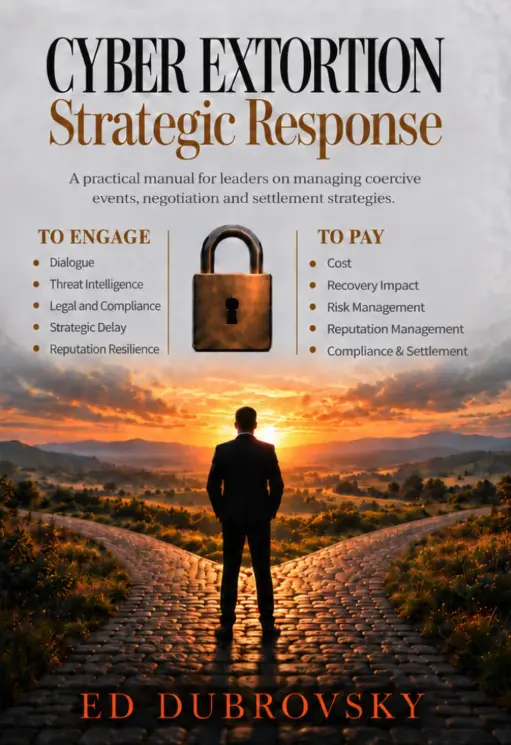
The arrest has sent shockwaves through the cybersecurity industry, particularly given Dubrovsky’s expertise in the very field he is now accused of exploiting. His LinkedIn profile highlights his role as the author of Cyber Extortion Strategic Response, a 252-page volume dedicated to navigating the complex, often dangerous world of ransomware negotiations. The book purports to guide organizations through the decision-making processes required when faced with extortion, emphasizing that companies must distinguish between communicating with criminals and actually yielding to their demands.
"At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay," an excerpt from the book’s Amazon listing reads. "Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."
Investigators are now tasked with determining where the line between legitimate advisory services and criminal assistance was crossed. As of now, Dubrovsky has not been represented by an attorney in the available court filings, and the court has yet to appoint a public defender. Attempts to reach him or his associates at CyberSteward for comment have been unsuccessful.
The Shadow of ShinyHunters
The ShinyHunters group has become a primary target for federal law enforcement due to its aggressive and highly disruptive tactics. The group typically gains initial access to corporate networks through phishing campaigns and the use of stolen credentials, often targeting software-as-a-service (SaaS) providers. Once inside, they siphon vast amounts of data and threaten to release it publicly unless a substantial ransom is paid. According to estimates provided by the FBI, the group has successfully extorted more than $70 million from various victims throughout the current calendar year.

The pressure on ShinyHunters has intensified in recent weeks. Sources indicate that the FBI has been meticulously examining devices seized during the arrest of Pepijn van der Stap, a convicted cybercriminal apprehended by Dutch police last month. The evidence gathered from those devices is reportedly providing the FBI with a roadmap of the group’s internal communications and operational structure.
The FBI’s interest in the group became personal after hackers managed to breach the agency’s own recruitment portal. The stolen data included sensitive information on thousands of individuals, such as their specific units, medical backgrounds, and psychiatric records. Following the arrest of Van der Stap, a member of the group going by the moniker "Rey" attempted to seize control of the collective, reportedly taunting the FBI regarding the stolen files.
However, the group’s momentum appears to be waning. Last week, Reuters reported that "Rey"—who authorities identified as a teenager named Saif Al-din Khader—had been detained and was actively cooperating with federal investigators. His apprehension occurred as the group attempted to extort a digital aviation unit that had been spun off from Boeing in late 2025.
As the investigation into the ShinyHunters network continues to unfold, authorities are signaling that this week’s arrest in Pennsylvania is unlikely to be the last. Sources close to the inquiry suggest that charges against principals at other companies specializing in ransomware negotiation may be forthcoming, as federal agents continue to peel back the layers of a criminal enterprise that has successfully exploited the intersection of corporate fear and digital vulnerability. The FBI continues to decline official comment as the case proceeds, but the shift in jurisdiction to Texas suggests a high-level, sustained effort to dismantle the infrastructure that has allowed ShinyHunters to operate with impunity for so long.