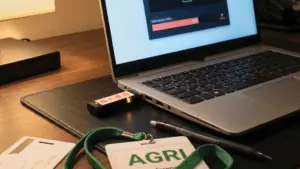
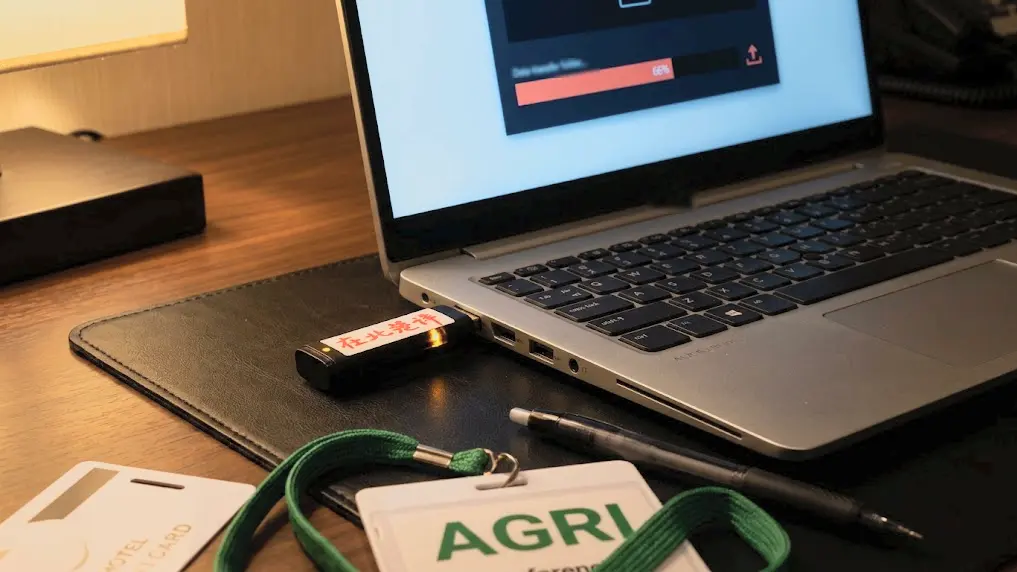
In a sophisticated display of espionage that bypassed traditional digital defenses, a Chinese state-linked hacking group successfully compromised the executive laptops of several high-profile agricultural industry leaders during a conference on Hainan Island this spring. Rather than relying on the common, noisy vectors of phishing emails or network-based exploits, the adversaries gained physical access to the hotel rooms of their targets while they were away at dinner. Once inside, the operators manually booted the executives’ laptops from a USB stick, injecting malicious code directly into the devices’ storage before leaving the rooms undisturbed.
The campaign, which has been attributed to a group CrowdStrike tracks as OVERCAST PANDA, was unveiled in the cybersecurity firm’s 2026 Threat Hunting Report. Adam Meyers, CrowdStrike’s senior vice president of counter adversary operations, detailed the precise, calculated nature of the operation during an interview at the company’s Fal.Con 2026 conference. According to the investigation, one intruder gained entry to a victim’s room at approximately 8 p.m. local time, while a second room was breached shortly before 10 p.m. The attackers utilized a known backdoor called FlowCloud, writing it directly to the machines’ storage media. By the time the executives returned to their rooms, the hardware had been compromised, yet the laptops showed no signs of external interference.
This physical-access operation represents a rare and chilling evolution in modern cyber warfare. Security researchers have long referred to this technique as an "evil maid attack"—a concept famously demonstrated by Joanna Rutkowska in 2009—but its application by state intelligence services at scale is highly unusual. While CrowdStrike tracks nearly 300 distinct adversarial groups, physical tampering remains infrequent. Other groups, such as MUSTANG PANDA, have historically relied on victims to plug in discarded USB sticks, but OVERCAST PANDA’s methodology is distinct: it combines the logistical capability of hotel-room entry with the technical precision of a pre-boot malware injection.
The payload, FlowCloud, is not new; it has been documented by security firms since 2020, when it was identified in attacks targeting U.S. utilities. Despite its age, the malware remains potent. When the targeted executives powered on their machines the following morning, the trigger fired, and FlowCloud loaded into the system. Once active, the implant initiated a suite of invasive functions, including keylogging, screen capturing, file collection, and the harvesting of stored credentials. Because the compromise occurred below the level of the operating system, it remained invisible to standard security protocols until the moment the laptop finished booting and the malicious process finally initiated.
Why Conventional Security Tools Missed the Breach
The success of the OVERCAST PANDA campaign highlights a significant blind spot in modern enterprise security architectures. Endpoint Detection and Response (EDR) platforms require an active operating system and a running agent to monitor for threats. Similarly, Multi-Factor Authentication (MFA) is only effective when a login attempt is made, and phishing training assumes the presence of a deceptive email.
By initiating the compromise at the pre-boot stage, the attackers effectively bypassed the entire authentication stack and the security agent layer. The malicious implant and its trigger were already embedded on the disk before the EDR agent had even initialized. Meyers acknowledged that while Falcon’s sensors eventually caught the FlowCloud process once the operating system loaded, the critical window of opportunity—the hours during which the laptop sat in a compromised state—was entirely unprotected.
Meyers suspects that the Ministry of State Security (MSS) is behind the OVERCAST PANDA group. The physical execution of these attacks implies access to high-level resources, suggesting that those entering the hotel rooms were likely intelligence officers or agents, or potentially hotel staff who had been bribed or coerced into facilitating the breach. The choice of an agricultural conference as the target venue aligns with China’s broader strategic objectives, as outlined in its national five-year plans. A similar operation, involving the same tradecraft, was also identified mid-year against a U.S.-based media professional.
Evolving Defenses in an Era of AI-Powered Threats
The disclosure of these attacks coincides with a major shift in CrowdStrike’s product strategy. At Fal.Con 2026, the company announced a new suite of AI-driven security tools, including Falcon Guardian and an agentic cybersecurity system called SafeMind, developed in partnership with Nvidia. These tools are designed to combat the rapidly rising tide of AI-driven cybercrime, which saw a 171% increase in cloud-conscious eCrime activity during the reporting period.
However, these innovations are primarily focused on network-based threats. As Meyers noted, the landscape of digital danger is shifting toward automated, high-speed intrusions. Groups like REVENANT SPIDER, which recently used AI to compromise 17 victims in less than an hour, represent the type of scalable, high-velocity threat that keeps security leaders awake at night. Because network-based attacks can target thousands of machines simultaneously, they remain the primary focus of enterprise security budgets.
The OVERCAST PANDA operation, by contrast, is slow, labor-intensive, and unscalable. Yet, for the executives targeted in Hainan, the lack of scale was irrelevant. They were specific, high-value targets, and the attackers utilized a method that rendered conventional software defenses entirely moot.
Closing the Gap: Firmware and Policy
Despite the technical complexity of the attack, Meyers emphasized that the solution is not necessarily a new piece of software, but rather a return to rigorous physical security and firmware management. "It’s a solvable problem," he stated. "It’s just an inconvenient solution."
The most effective defenses against such physical tampering are foundational: disabling external boot capabilities in the UEFI, setting robust BIOS administrator passwords, and implementing pre-boot authentication. Many organizations rely on standard BitLocker configurations using only a Trusted Platform Module (TPM), which researchers have repeatedly shown can be bypassed via physical probing of the motherboard. Requiring a PIN or a hardware key at startup ensures that even if an attacker gains physical access to a device, the storage remains encrypted and unreadable.
Furthermore, firms must adopt a more conservative posture regarding travel-related security. Meyers, who personally utilized "burner" laptops and email accounts during his own international travel, argues that security leaders must assume that any device taken abroad is subject to compromise. This includes potential seizure by customs officials, who may compel a user to unlock their device.
The fundamental issue remains organizational fracture. In many large enterprises, the teams responsible for firmware and BIOS configuration are separate from the teams deploying EDR agents and AI-based identity providers. When these silos are not bridged, critical gaps in security—such as leaving a USB port open for boot-up—persist, despite the presence of advanced detection tools elsewhere in the environment.
As the industry pivots toward AI and runtime security, the OVERCAST PANDA case serves as a stark reminder that digital security is only as strong as its weakest physical link. Executives and organizations must recognize that when they travel, their threat model changes entirely. Without a combination of firmware-level lockdown, strict pre-boot authentication, and the use of dedicated, wiped travel devices, those traveling for high-stakes business remain vulnerable to the oldest trick in the intelligence book: the "evil maid" waiting in the room.