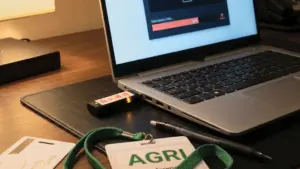
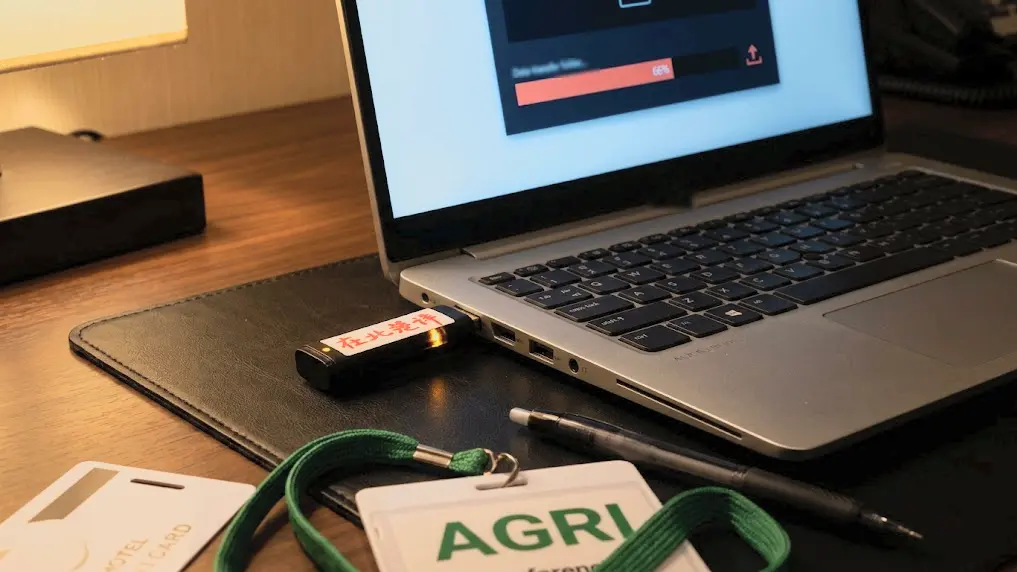
A sophisticated Chinese state-linked hacking group has demonstrated that even the most robust digital security perimeters can be rendered moot by old-fashioned physical infiltration. During an agricultural industry conference held on Hainan Island this past spring, the group—identified by cybersecurity firm CrowdStrike as OVERCAST PANDA—successfully compromised the laptops of visiting executives. Rather than relying on traditional cyberattack vectors like spear-phishing campaigns or network-based exploits, the intruders physically entered the executives’ hotel rooms while they were away at dinner. Once inside, they used bootable USB sticks to load malicious software directly onto the machines, bypassing the operating system entirely.
CrowdStrike, which has been tracking the group’s activities, disclosed the details of this campaign in its 2026 Threat Hunting Report. The operation’s timeline, which was cleared for publication by Adam Meyers, CrowdStrike’s senior vice president of counter adversary operations, provides a chilling look at the persistence of state-sponsored actors. According to the data, an intruder accessed one room at approximately 8 p.m. local time, and a second room by 9:57 p.m. In both instances, the actors installed a backdoor known as FlowCloud directly to the laptop storage before rebooting the machines and exiting the premises, leaving no immediate trace of a network intrusion or stolen credentials.
The intrusion window, which spanned from March to May 2026, highlights the group’s focus on specific, high-value targets. While CrowdStrike’s OverWatch team was able to disrupt the intrusions, the firm assesses that OVERCAST PANDA is highly likely to continue these operations. The malware itself is not new; FlowCloud has been documented by researchers for years. Proofpoint first identified it in 2020 when it was used in phishing campaigns targeting U.S. utility sectors, and NTT Security’s Security Operations Center has tracked similar USB-delivered infections at Japanese corporate branches since early 2022.
The Evolution of the "Evil Maid" Attack
Security researchers have long referred to the physical tampering of unattended devices as an "evil maid attack," a term popularized by Joanna Rutkowska in 2009. While the concept is well-known in cybersecurity circles, such operations remain relatively rare among the 290 distinct adversaries tracked by CrowdStrike. Adam Meyers notes that while other groups, such as MUSTANG PANDA, have historically relied on victims plugging in a dropped USB stick, the OVERCAST PANDA campaign represents a significant escalation in tradecraft. The novelty lies in the deliberate, coordinated entry into a hotel room by state intelligence assets, followed by the silent deployment of malware through a forced reboot.
When the executives returned and powered on their devices the following morning, the malicious trigger fired, and FlowCloud loaded into memory. Once active, the malware provided the attackers with a suite of capabilities, including keylogging, screen capture, file collection, and the harvesting of stored credentials.
The security gap created by this method is significant. As Meyers explained during an interview at the Fal.Con 2026 event, CrowdStrike’s Falcon platform has visibility once the machine boots up, but there is a dangerous "blind spot" between the moment the USB is inserted and the moment the executive next logs in. During this window, the laptop sits in a state of compromise, waiting for the user to initiate the system, at which point a registry key or similar mechanism triggers the malware, allowing the Falcon sensor to finally detect and flag the malicious process.
Why Conventional Security Tools Fall Short
The success of the OVERCAST PANDA campaign underscores the limitations of standard endpoint protection. Modern Endpoint Detection and Response (EDR) agents require the operating system to be fully loaded and the security software to be active to function. Similarly, Multi-Factor Authentication (MFA) requires a login attempt, and phishing training assumes a user will interact with a malicious email. Because the initial compromise occurred below the operating system and the authentication stack, the attackers successfully bypassed these common safeguards. By the time the Falcon sensor identified the activity, the implant and its trigger were already embedded on the device.
Meyers attributes the operation to China’s Ministry of State Security. He suggests that the individuals physically entering the rooms are likely officers of the Ministry of State Security or the Ministry of Public Security, or potentially hotel staff coerced or bribed into facilitating the intrusion. This assessment is supported by the specific nature of the targeting; focusing on an agricultural conference aligns with broader economic intelligence collection priorities linked to China’s five-year plans. A separate incident involving a U.S.-based media professional, which utilized identical tradecraft, suggests that this is a systematic approach to high-level corporate and state espionage.
Addressing the Vulnerability: Firmware and Policy
Despite the sophistication of the attack, the vulnerabilities exploited are, according to Meyers, entirely solvable. The difficulty lies in the fact that the solutions are often viewed as inconvenient. CrowdStrike has integrated firmware attack detection and BIOS settings auditing into its Falcon sensor since 2019, including telemetry from Dell SafeBIOS, yet many organizations fail to apply these controls to the devices their executives carry on international travel.
The recommended defenses against such attacks are well-established. Disabling the ability to boot from external media within the UEFI settings effectively removes the primary vector used by OVERCAST PANDA. Furthermore, setting a robust BIOS administrator password prevents unauthorized users from altering these configurations. Pre-boot authentication, which requires a PIN or key before the encrypted storage becomes readable, ensures that even if a machine is accessed, the data remains protected.
"Don’t bring anything with you that you’re not comfortable with handing over to a foreign intelligence service," Meyers advised, noting that he personally utilized temporary "burner" laptops and email accounts when traveling for his own work, wiping the devices immediately upon return. He warned that the risk extends beyond hotel rooms, as customs officials in certain jurisdictions can legally seize devices and compel users to provide credentials.
The Challenge of Scaling Security
While the OVERCAST PANDA campaign is alarming, CrowdStrike researchers emphasize that network-based threats still pose a more significant risk to the average enterprise. During the Fal.Con 2026 conference, Meyers compared the hotel room operation to cases involving REVENANT SPIDER, an eCrime group that utilized AI to compromise 17 victims in under 48 minutes using custom web shells.
"You can’t intrude on hotel rooms at scale," Meyers remarked, contrasting the labor-intensive physical nature of the OVERCAST PANDA operation with the speed and automation of modern network-based attacks. Because physical-access tradecraft cannot be automated or deployed across thousands of machines simultaneously, it remains a specialized tool for state actors targeting high-profile individuals. However, for those specific targets, the "slow" method is precisely what makes it effective.
The current landscape of cybersecurity is defined by a disconnect between the threats we anticipate and the threats we encounter. At conferences like Fal.Con, vendors often focus on runtime protection, which is vital for modern cloud and AI-driven environments, but this protection only begins once the machine is powered on. Organizational silos often exacerbate the problem; the team responsible for deploying EDR agents is rarely the same team responsible for managing BIOS settings or enforcing travel policies.
As long as executives carry production-access devices into high-risk environments, they remain vulnerable to this blend of low-tech physical access and high-tech malware deployment. The solution does not require new, expensive software, but rather a more rigorous approach to hardware hygiene and travel protocol. Until organizations mandate the hardening of firmware and the use of dedicated, non-sensitive travel devices, the window between a laptop being shut down for the night and reopened the next morning will remain a significant, exploitable gap for state-sponsored intelligence services.