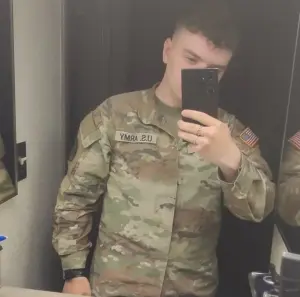
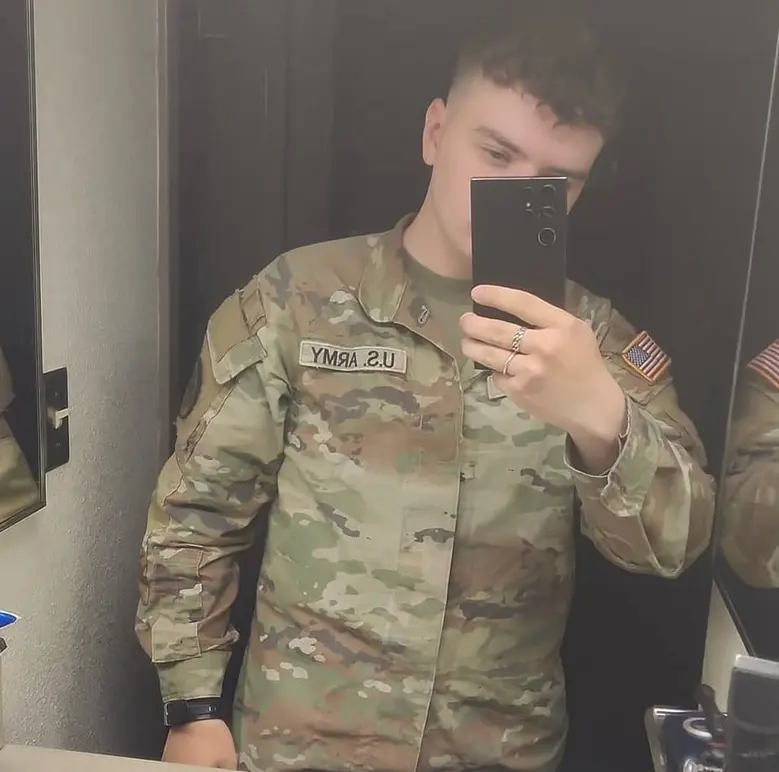
A U.S. Army soldier who leveraged his position and technical skills to orchestrate a high-stakes cybercriminal operation has been sentenced to 70 months in federal prison. Cameron John Wagenius, 22, was handed the sentence today in a Seattle federal courtroom after pleading guilty to charges stemming from his role in hacking into several major telecommunications companies. Beyond his prison term, he has been ordered to pay nearly $300,000 in restitution to the victims of his digital campaigns, which compromised the personal call and text metadata of more than 100 million AT&T customers.
Wagenius, who operated under the handle “Kiberphant0m,” was stationed at a U.S. Army base in South Korea during the height of his criminal activities. His operation was not a solitary effort; he acted as a central figure in a network of co-conspirators who exploited gaps in cloud security to access sensitive corporate data. By targeting customers of the cloud data storage service Snowflake who had failed to enforce multi-factor authentication (MFA) on their accounts, Wagenius and his associates were able to exfiltrate vast troves of information. Snowflake has since mandated MFA across all customer accounts in response to the widespread vulnerability.
The scale of the breach was unprecedented. In October 2024, the persona Kiberphant0m began bragging on various dark-web forums about his acquisition of call and text metadata—including timestamps, durations, and source-destination numbers—for tens of millions of AT&T subscribers. His reach extended far beyond a single carrier; Wagenius claimed to have compromised over a dozen telecommunications firms worldwide, including Verizon’s specialized Push-to-Talk business. His modus operandi involved public extortion, where he would threaten to release stolen data unless the victim companies met his financial demands.
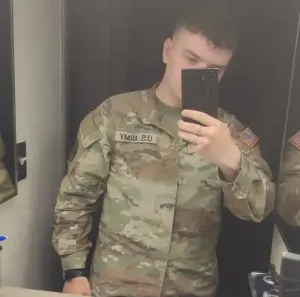
The investigation into Wagenius gained significant momentum in November 2025, when reporting by KrebsOnSecurity identified that the individual behind the Kiberphant0m handle was likely an active-duty U.S. soldier based in South Korea. The identification triggered a swift multi-agency response. Less than a month after the report, federal authorities arrested Wagenius, charging him in two separate indictments. He ultimately pleaded guilty to all counts, leading to today’s sentencing.
The complexity of the investigation was underscored by the high-level coordination between federal agencies. Paul Russell, a resident agent in charge at the Defense Criminal Investigative Service (DCIS)—the criminal investigative arm of the Department of Defense Office of Inspector General—noted the rarity and severity of the case.
“We don’t often get leads where there’s an active duty soldier with a secret clearance who’s creating hacking tools and trafficking in data,” Russell stated. “That doesn’t happen every day, and so when that hits, it really spins all of our partner organizations up. It was very serious from jump street, just because it was unique, it was an insider threat, and we weren’t sure what we were dealing with.” The DCIS worked in tandem with the FBI, the Army Criminal Investigative Division (CID), and the U.S. Secret Service to dismantle the operation.
Wagenius did not act alone, and his sentencing brings into focus the broader network of cybercriminals involved in these thefts. Prosecutors identified Kenneth Schuchman, a 28-year-old from Vancouver, Washington, as a primary accomplice. Schuchman is no stranger to federal authorities; he previously pleaded guilty in 2019 to operating the Satori botnet, a massive infrastructure of compromised Internet-of-Things (IoT) devices that powered wide-scale distributed denial-of-service (DDoS) attacks.
Other co-conspirators linked to the Snowflake data thefts are also facing the consequences of their actions. Conor Riley Moucka, an Ontario resident known online as “Judische,” was arrested in 2024 and entered a guilty plea in August 2026. Meanwhile, John Erin Binns, an American citizen currently residing in Turkey, remains a significant figure in the investigation. Binns is also a person of interest in a separate, massive 2021 data breach at T-Mobile that exposed the personal records of at least 76 million customers.
The audacity of the Kiberphant0m persona reached a dangerous threshold when, following the arrest of Moucka, the group attempted to "re-extort" victims. Despite AT&T having already paid a $370,000 Bitcoin ransom, the group continued to threaten the public release of sensitive information. In a move that escalated the case from a corporate data theft to a potential national security concern, Kiberphant0m posted what he claimed were call logs belonging to then-President-elect Donald Trump and then-Vice President Kamala Harris. He also claimed to possess stolen schematics from the U.S. National Security Agency (NSA).
The legal proceedings have been complicated by the defendant’s behavior while in custody. According to a sentencing memorandum filed on September 19 by federal prosecutors in Seattle, Wagenius—despite his cooperation with authorities—continued to exhibit a dangerous interest in cyber vulnerabilities while awaiting his fate. Prison records indicate that between September 2025 and his sentencing, Wagenius repeatedly violated Bureau of Prisons (BOP) computer use policies.
In a series of calculated attempts to probe the security of his own incarceration environment, Wagenius reportedly used other inmates’ email accounts to solicit information from commercial AI tools. In one instance, he asked an AI for specific Common Vulnerabilities and Exposures (CVEs) related to Windows 10 Enterprise privilege escalation, requesting "real-world working scripts" without omitted code. In another, he requested a step-by-step guide and exploit code for CVE-2023-45208, a command injection vulnerability affecting D-Link networking devices.
Perhaps most alarmingly, prosecutors noted that Wagenius also sought instructions on how to construct an antenna using commissary items to extend radio reception within the prison, and even researched methods for escaping the facility. The sentencing memo highlights that Wagenius attempted to mask these queries as research for a book he was writing—a technique known as "prompt injection," used to bypass safety guardrails installed in AI models to prevent the generation of malicious content.
The government noted that there is currently no evidence that Wagenius successfully deployed these vulnerabilities or established a functional escape plan. When confronted by investigators about the queries, Wagenius claimed he was merely researching potential weaknesses to report them to the BOP.
Despite the immense scale of the data he controlled and the high-profile nature of his targets, the financial outcome of the scheme was remarkably disproportionate. The sentencing memo reveals that, for all the havoc caused, Wagenius managed to net only about $1,500 from his criminal efforts.
The court emphasized that while his personal financial gain was negligible, the collateral damage was immense. The government’s sentencing memorandum concluded that although Wagenius was not a particularly successful cybercriminal in terms of profit, he acted with clear intent to cause significant, lasting harm to individual citizens, major U.S. corporations, and the United States government itself. With his sentencing now finalized, Wagenius faces the reality of nearly six years in federal prison, marking the end of a case that exposed both the vulnerabilities of global cloud infrastructure and the unpredictable nature of the insider threat.