







In a significant blow to the global cybercrime ecosystem, authorities in Australia have successfully apprehended two men linked to "TeamPCP," a prolific and destructive data extortion group responsible for one of the most sustained software supply chain attack campaigns in history. The Australian Federal Police (AFP) confirmed today that two Western Australian residents, aged 21 and 23, were taken into custody following an intensive joint operation involving the FBI and local law enforcement. The arrests mark the culmination of a months-long investigation into a sophisticated syndicate that allegedly weaponized open-source software to infiltrate thousands of businesses worldwide.
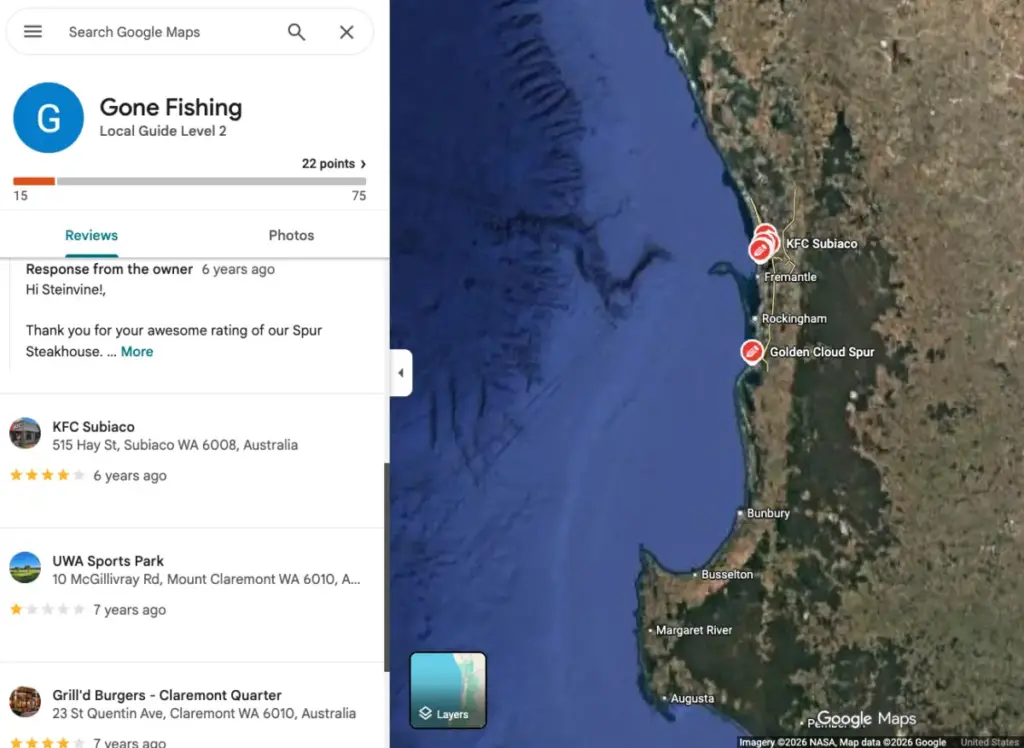
While the AFP has withheld the identities of the defendants, investigative reporting by KrebsOnSecurity—which had been in communication with the group’s self-described spokesperson since June—has identified the primary figures behind the operation. The downfall of the group appears to have been hastened by a combination of high-level law enforcement collaboration and a series of "operational security" (OpSec) failures that left a digital trail connecting the hackers’ online personas to their real-world identities in the coastal suburb of Cottesloe, near Perth.

The Rise of the Shai-Hulud Worm
TeamPCP first emerged on the cybercrime landscape in late 2025, distinguishing itself through a relentless focus on the software supply chain. Rather than targeting individual endpoints directly, the group specialized in embedding malicious code into widely used open-source software tools. Their signature weapon was "Shai-Hulud," a self-propagating worm designed to harvest credentials and inject backdoors into legitimate development environments.
The group’s methodology, as detailed by Wired journalist Andy Greenberg earlier this year, relied on a cyclical, parasitic approach. By compromising the networks of developers who maintain popular open-source libraries, TeamPCP was able to distribute malicious updates to the thousands of downstream users who relied on that software. Once a machine was infected, the malware would steal authentication credentials, allowing the hackers to compromise further repositories. This "recursive" model allowed the syndicate to exponentially expand its reach, turning the trust-based model of open-source development against the global technology infrastructure.

Beyond mere infiltration, TeamPCP aggressively incentivized this activity. In May, they published the source code for the third iteration of Shai-Hulud and launched a hacking competition. They offered a bounty of $1,000 in Monero to any participant who could achieve the highest number of downloads for compromised software packages. As security firm Dataminr noted, the contest functioned less as a game and more as a recruitment tool to identify talented malicious actors and acquire access to high-value networks at scale. The group reportedly dismissed the $1,000 prize as a mere "participation trophy," signaling that they were prepared to pay far more for "meaningful access" harvested by their recruits.
The group’s reach was staggering. In March, they compromised the code for LiteLLM, an open-source AI gateway used to connect applications to over 100 large language models. A subsequent analysis by CloudSEK revealed that the breach resulted in the theft of cloud service keys and sensitive secrets from more than 2,500 organizations, including some of the world’s most prominent technology firms. By May, the group claimed credit for breaching at least 3,800 repositories on GitHub after a developer inadvertently installed a compromised extension.

Meet the "Cybercats"
Security researchers characterize TeamPCP not as a rigid hierarchy, but as a fluid "amalgamation" of various threat actors who frequently collaborate. According to Austin Larsen, a principal threat analyst at the Google Threat Intelligence Group, the group functions as a "peer community of individually-skilled actors" held together by a central figure known as "Kernelstub."
Kernelstub, who operated a Twitter/X profile under the same name, facilitated the group’s communication via a Matrix chat server dubbed "Cybercats." This server became the nerve center for several cybercrime entities, where members used their hacker handles to discuss targets, taunt victims, and coordinate ransom demands. Among the key administrators on the server were individuals known as "Boxturtle," linked to data breaches at major automotive manufacturers including BMW, Audi, and Toyota, and "SeesawSec," the alias behind Fulcrumsec, an extortion group that has targeted high-profile entities like Novo Nordisk and LexisNexis.

The investigation into the group’s leadership eventually centered on two individuals: the 23-year-old Michael Gaebler and 21-year-old Ruben Thomson. Digital forensics and online activity logs revealed that the account "@pcpcasper," a vocal member of an Australian neo-Nazi political organization who frequently posted images of his pet cat, was linked to the group’s activities. Sources confirmed that this individual was one of the two men arrested. The other, Ruben Thomson, operated under the handle "T" or "@pcpcats," serving as the group’s public spokesperson.
The Unraveling of an Operator
The downfall of the group’s leadership can be traced back to a series of critical lapses in operational security. Ruben Thomson, who utilized various monikers such as "EllisD25," "BulkDMT," and "Express" on dark-web forums, often shared personal details that allowed researchers to piece together his life in Perth.

Intelligence firms, including Intel 471 and SpyCloud, tracked the group’s activities across multiple email addresses and IP ranges. Evidence showed that Thomson used his own family’s home internet connection to host private file servers and register accounts on cybercrime forums. Further investigation revealed that Thomson had incorporated several businesses in Australia, including one ironically named "OPSEC Express," effectively linking his legal identity to the criminal aliases he used to sell stolen data and exploits.
Perhaps the most damning evidence came from Thomson’s own professional and social media footprint. He maintained an Upwork profile that detailed his skills in PHP development and Linux, and his HackerOne bug bounty account—used for legitimate research—was registered under the name "Deadcatx3," a handle widely flagged by security firms as a primary alias for the TeamPCP leader.

In an interview with KrebsOnSecurity conducted via Signal in July, the individual known as "Ellis" was remarkably candid about his involvement. He claimed to have drifted into cybercrime after struggling with homelessness and addiction, describing the "blackhat" lifestyle as a way to find community and purpose. He admitted to earning roughly $20,000 through his illicit activities, though he maintained that the money was not his primary motivator. He expressed a resignation regarding his eventual arrest, noting that he struggled with substance abuse and felt that prison would likely fail to provide the rehabilitation he needed.
A Legacy of Security Reform
Despite the damage caused by TeamPCP, the security community has pointed to one unexpected outcome: the group forced a necessary reckoning within the technology industry. Charlie Eriksen, a security researcher at Aikido Security, described TeamPCP as a new breed of threat actor—one that does not fit the traditional mold of state-sponsored intelligence or purely profit-driven organized crime.

"They are not a state actor, not quite organized cybercrime, and not purely ideological," Eriksen noted. "Their motivations seem to mix money, disruption, attention, and ideology."
Eriksen argued that the ease with which TeamPCP leveraged artificial intelligence and large language models to bridge the gap between theoretical research and operational attacks represents a dangerous shift in the threat landscape. However, the group’s brazen attacks on GitHub ultimately compelled Microsoft to implement more robust safeguards. In late July, GitHub introduced a three-day "cooldown" mechanism for its Dependabot service, a measure specifically designed to prevent the rapid propagation of compromised software packages.

By exposing the vulnerabilities in the software supply chain, TeamPCP achieved in months what the cybersecurity industry had struggled to implement for years. Microsoft and other major coding platforms were forced to prioritize supply chain security, effectively closing the doors that TeamPCP had spent the better part of a year kicking open.
As the legal process begins, the two men remain in custody in Western Australia. Following a court appearance in Perth, they were denied bail and are expected to remain in detention until their next scheduled appearance on September 18. While the arrest of Thomson and Gaebler effectively disarms TeamPCP, the case serves as a stark reminder of the evolving nature of cyber threats and the critical importance of maintaining secure, vigilant software development practices in an era where the barriers to entry for sophisticated cybercrime continue to lower.