In a significant development that underscores the growing intersection between the legitimate cybersecurity industry and the dark underbelly of cybercrime, federal agents have arrested a Canadian executive on charges related to the notorious hacking collective known as ShinyHunters. The arrest, which took place in Pennsylvania this past Thursday, marks a pivotal moment in the FBI’s ongoing efforts to dismantle a group that recently managed to breach federal systems and access sensitive, personal data belonging to thousands of FBI personnel.
While the FBI has remained tight-lipped regarding the specifics of the case, multiple sources familiar with the investigation have confirmed the arrest to KrebsOnSecurity. The New York Times was among the first to report that a Canadian national had been taken into custody in Pennsylvania on suspicion of providing material assistance to the ShinyHunters group. Despite the gravity of the allegations, neither the federal authorities nor FBI Director Kash Patel, who acknowledged the arrest in a brief statement on social media platform X, have officially disclosed the identity of the detainee.
The Intersection of Professional Security and Criminal Allegations
The suspect, identified through court records as Edward Dubrovsky, was apprehended while in Philadelphia to attend the Cyber Risk Summit, a high-profile industry gathering held at the Loews Philadelphia Hotel from October 5 to October 7. According to sources close to the investigation, Dubrovsky’s professional background—specifically his work in the niche sector of ransomware negotiation—has become a central focus for federal investigators.
For years, companies specializing in ransomware negotiations have positioned themselves as the bridge between desperate organizations and ruthless cybercriminals. Their stated goal is to provide a "compliant" and strategic path forward for companies hit by extortion, often serving as intermediaries to minimize financial damage and data leakage. However, the arrest of a veteran of this industry raises troubling questions about where the line is drawn between professional advisory services and active participation in the extortion economy.
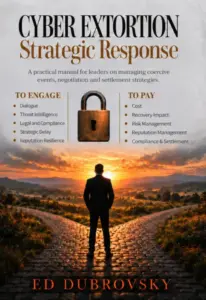
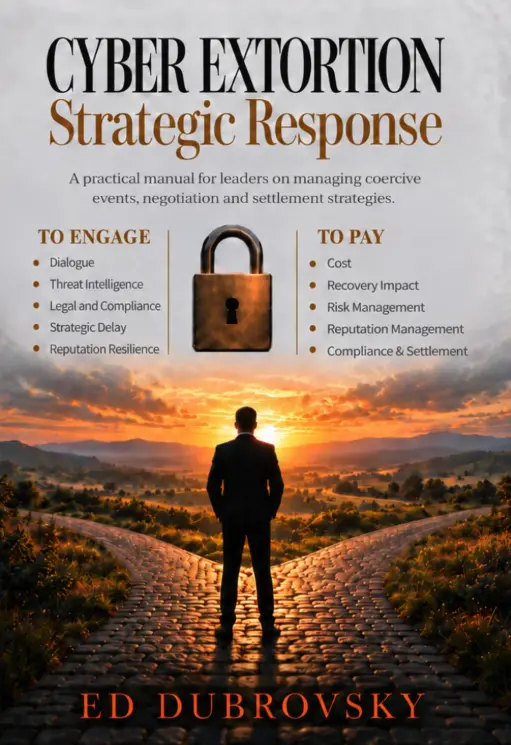
Publicly available records indicate that Dubrovsky has been a prominent voice in this field. He is the author of Cyber Extortion Strategic Response, a 252-page professional manual that purports to guide organizations through the complex, high-stakes decisions required after a ransomware attack. In his book, Dubrovsky emphasizes a nuanced approach to dealing with hackers, arguing that "communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay." He posits that such engagement can serve legitimate objectives, such as testing the validity of an attacker’s claims or buying time to preserve an organization’s options.

Following the news of his arrest, questions regarding his professional history emerged. While his LinkedIn profile previously identified him as an "ex-founder" of the Canadian security firm Cypfer—a top sponsor of the Cyber Risk Summit—a spokesperson for the company moved quickly to clarify his tenure. The spokesperson stated that Dubrovsky was never a founder or co-founder, but rather served as a managing director until his resignation in December 2025. At the time of his arrest, Dubrovsky was associated with another Canadian firm, CyberSteward, which was also a sponsor of the Philadelphia conference.
A Shifting Legal Battleground
Federal court records reveal that an individual named Edward Dobrovsky (with a slight variation in the spelling of the surname) was formally charged on October 8 with conspiracy to threaten to impair the confidentiality of information with the intent to extort money, as well as interference with commerce by threats. Although many of the documents surrounding the case remain sealed, the available filings paint a picture of a sophisticated federal probe.
Perhaps most tellingly, the case was transferred on October 9 to the Eastern District of Texas. Sources indicate that this move is part of a broader strategy to centralize the sprawling ShinyHunters investigation within a single FBI field office, which has now become the primary nerve center for the case. As of the latest updates, the U.S. Bureau of Prisons inmate locator confirms that a 54-year-old Edward Dubrovsky is being held at a federal facility in Philadelphia, pending further judicial proceedings. To date, no attorney has been noted in the public record for the defendant, and the court has yet to appoint a public defender.
The Shadow of ShinyHunters
The investigation into the ShinyHunters group has intensified following a series of brazen attacks that have embarrassed federal law enforcement. The group, known for utilizing sophisticated phishing campaigns and the exploitation of stolen credentials, primarily targets software-as-a-service (SaaS) providers. Once inside, they siphon vast quantities of corporate data and threaten to leak it publicly unless exorbitant ransom demands are met. According to FBI estimates, the group has successfully extorted more than $70 million from victims throughout the 2026 calendar year.
The stakes of this investigation were raised significantly when ShinyHunters managed to penetrate an FBI online recruitment portal. The breach resulted in the exposure of sensitive data, including the units and specializations of agency personnel, as well as highly private medical and psychiatric records. The theft was followed by a series of taunts directed at the FBI, suggesting that the hackers were emboldened by the success of their incursion.

This latest arrest is part of a cascading series of law enforcement actions aimed at the group’s leadership and support network. Last month, Dutch police apprehended Pepijn van der Stap, a convicted cybercriminal, in a move that provided the FBI with a wealth of digital evidence. Sources indicate that investigators have been painstakingly analyzing devices seized from Van der Stap, leading to the belief that additional charges against other figures within the ransomware negotiation industry may be imminent.
The group’s internal dynamics have also been subject to rapid change. Following Van der Stap’s arrest, a figure operating under the handle "Rey" stepped into a leadership role, continuing the group’s campaign of extortion and public taunting. However, the lifespan of this new leadership appears to have been short-lived. Last week, Reuters reported that "Rey"—identified as a teenager named Saif Al-din Khader—was detained and is currently cooperating with federal investigators. Khader’s apprehension was reportedly tied to the attempted extortion of a navigation and digital aviation unit, an entity that had been divested by Boeing in late 2025.
As the investigation continues, the focus on the "negotiators" suggests that the FBI is looking beyond the hackers themselves to the entire ecosystem that facilitates these crimes. By targeting those who act as middlemen, federal authorities may be attempting to sever the financial lifelines that allow groups like ShinyHunters to thrive. For now, the legal proceedings against Dubrovsky represent a critical test of how the justice system will address those who operate in the murky gray area of cyber-extortion, and whether their professional expertise will be viewed as a service or a criminal enterprise.
The case remains fluid, with federal authorities declining to comment on the record beyond the initial confirmations of the arrest. As the epicenter of the investigation shifts to Texas, observers expect further developments in what has become one of the most high-profile and consequential cyber-crime investigations of the decade.