In a significant escalation of the federal investigation into the notorious cybercrime syndicate known as "ShinyHunters," FBI agents have arrested a prominent Canadian cybersecurity executive. The arrest, which occurred on Thursday, marks a pivotal moment in the government’s ongoing efforts to dismantle a group that recently managed to breach sensitive FBI databases, exfiltrating personal data belonging to thousands of federal agents.
The arrest was first confirmed by multiple sources close to the investigation, which has been intensifying in the wake of the group’s brazen attacks on government infrastructure. While the FBI has maintained a tight lid on specific identifiers, reports from The New York Times corroborated the apprehension of a Canadian national in Pennsylvania. FBI Director Kash Patel acknowledged the arrest in a brief statement on X (formerly Twitter), though he provided no specific details regarding the identity of the suspect or the exact charges filed.
A High-Stakes Arrest at a Cyber Risk Summit
Sources familiar with the investigation revealed that the suspect was in Pennsylvania to attend the Cyber Risk Summit, a professional gathering held between October 5 and October 7 at the Loews Philadelphia Hotel. The suspect’s presence at such an event is particularly notable, as his firm reportedly specialized in the sensitive and often controversial field of ransomware negotiations—acting as a liaison between organizations under duress and the cybercriminal groups holding their data hostage.
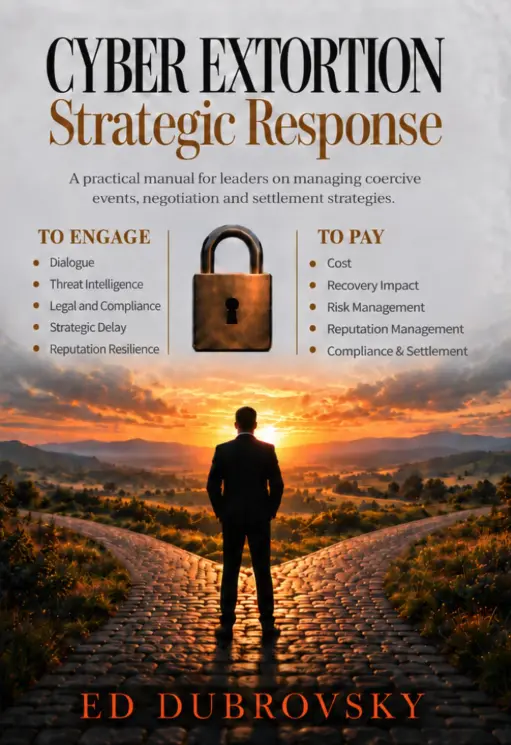
According to conference materials, the summit featured a range of industry leaders, but one name stood out among the sponsors: the Canadian security firm Cypfer. Further investigation into the backgrounds of key figures associated with the event led to Edward Dubrovsky. Dubrovsky, a well-known figure in the cybersecurity space and the author of the book Cyber Extortion Strategic Response, had publicly announced his intention to attend the summit as part of the team from CyberSteward, another Canadian firm and event sponsor.
While initial reports linked the arrest to the executive’s professional activities, a spokesperson for Cypfer later clarified that Dubrovsky was not a founder of their organization, as some professional profiles had suggested. Instead, the firm stated that he served as a managing director before resigning his position in November 2025. This clarification highlights the complex and often murky nature of the ransomware negotiation industry, where high-profile experts frequently move between firms and consultancies.

Charges and Judicial Movement
Federal court records indicate that an individual named Edward Dobrovsky—a slight variation in the spelling of the name—was taken into custody in Pennsylvania on October 8. The charges filed against him include "conspiracy to threaten to impair the confidentiality of information with the intent to extort money" and "interference with commerce by threats." While several of the core documents related to the complaint remain under seal, the existing docket entries at CourtListener.com provide a stark outline of the allegations.
As of the latest reports, the 54-year-old is being held at a federal facility in Philadelphia. However, in a move that suggests the federal government is consolidating its legal strategy, a notice was filed on October 9 to transfer the case to the Eastern District of Texas. Sources indicate that this specific district has become the operational epicenter for the FBI’s broader investigation into the ShinyHunters collective. As of the time of this report, the FBI has declined to comment on the specifics of the transfer or the ongoing proceedings.
For his part, Dubrovsky has not been reached for comment, and current records show that he has yet to be assigned a public defender or retain private counsel. His professional reputation, largely built on his expertise in handling the very threats he is now accused of facilitating, is currently the subject of intense scrutiny within the cybersecurity community. His book, Cyber Extortion Strategic Response, emphasizes the nuances of dealing with criminals, noting that "communicating with a criminal is not the same as negotiating a payment." The irony of his situation has not been lost on industry observers, who are now grappling with the implications of an expert in extortion defense being accused of participating in the same illicit ecosystem.
The Rise and Fall of ShinyHunters
The ShinyHunters group has long been a thorn in the side of global corporations and, more recently, federal agencies. The group typically operates by leveraging phishing campaigns and stolen credentials to siphon massive datasets from software-as-a-service (SaaS) providers. Once the data is secured, they issue ransom demands, threatening to leak the information on the dark web if payment is not received. According to FBI estimates, the group has successfully extorted more than $70 million from victims within the current calendar year alone.
The investigation into the group has been a multi-national effort, gaining significant momentum last month when Dutch authorities arrested the convicted cybercriminal Pepijn van der Stap. Following that arrest, investigators have been meticulously combing through seized digital devices to map the network’s internal structure. Sources indicate that this data trove has provided the FBI with a roadmap of the group’s operations, leading to the belief that further charges against individuals at other ransomware negotiation firms may be forthcoming.

A Public Taunting of Federal Authorities
Following the arrest of Van der Stap, the group’s leadership underwent a rapid transition. A member operating under the handle "Rey" assumed control of the collective and quickly adopted an aggressive posture toward law enforcement. Rey went so far as to taunt the FBI over the successful infiltration of their own internal recruitment portal. That specific breach was particularly damaging, as it resulted in the exposure of sensitive internal documents, including the units and specializations of FBI personnel, as well as private medical and psychiatric records.
However, the group’s hubris proved to be its undoing. Last week, Reuters reported that "Rey"—who was identified as a teenager named Saif Al-din Khader—had been apprehended and was actively cooperating with federal investigators. The arrest of Khader followed a botched extortion attempt against a navigation and digital aviation unit that had been divested by Boeing in late 2025. The FBI’s ability to track and apprehend the group’s leadership in such rapid succession suggests a highly coordinated effort to dismantle the organization from the inside out.
As the case against the Canadian executive proceeds, the cybersecurity industry remains in a state of flux. The intersection of legitimate security consulting and the illicit world of cyber extortion has long been a gray area, but the recent federal actions signal a firm shift in policy. With the investigation now centralized in Texas and multiple key figures in custody, the legal and operational landscape for ransomware negotiators is likely to undergo significant changes. The FBI’s silence on the specifics of the case underscores the sensitivity of the evidence being processed, and as the situation develops, further indictments are expected to ripple through the sector. For now, the focus remains on the courtroom in the Eastern District of Texas, where the government will attempt to prove that the line between legitimate negotiation and criminal conspiracy was not just blurred, but systematically crossed.