In a significant escalation of the federal government’s campaign against the prolific hacking collective known as ShinyHunters, agents with the Federal Bureau of Investigation (FBI) arrested a Canadian cybersecurity executive in Pennsylvania this past Thursday. The suspect, taken into custody amidst an industry conference, is alleged to have provided assistance to the group, which has gained international notoriety for its high-stakes extortion schemes, including the recent theft of sensitive personnel data belonging to thousands of FBI agents.
The arrest was first noted by The New York Times, which reported that a Canadian national had been detained in Pennsylvania on suspicion of facilitating the operations of the hacking group. While the FBI has remained tight-lipped regarding specific identities, a public statement issued by FBI Director Kash Patel via social media confirmed the agency’s active pursuit of those involved in the recent breaches. Sources close to the investigation have confirmed to KrebsOnSecurity that the arrest occurred while the individual was attending the Cyber Risk Summit, a high-profile industry event held at the Loews Philadelphia Hotel between October 5 and October 7.
The individual taken into custody has been identified as Edward Dubrovsky, a veteran in the cybersecurity space and a former figure within the Canadian security firm Cypfer. According to records and conference materials, Dubrovsky was present at the summit, which counts several prominent security firms among its sponsors. While a spokesperson for Cypfer later clarified that Dubrovsky was not a founder or co-founder—as his LinkedIn profile had previously claimed—but rather a managing director who resigned in November 2025, his presence at the summit alongside other industry professionals marked a dramatic intersection between the world of cybersecurity defense and the criminal elements it seeks to combat.
The Intersection of Negotiation and Extortion
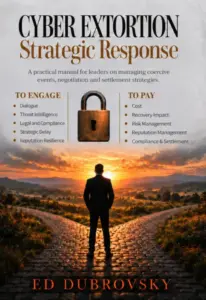
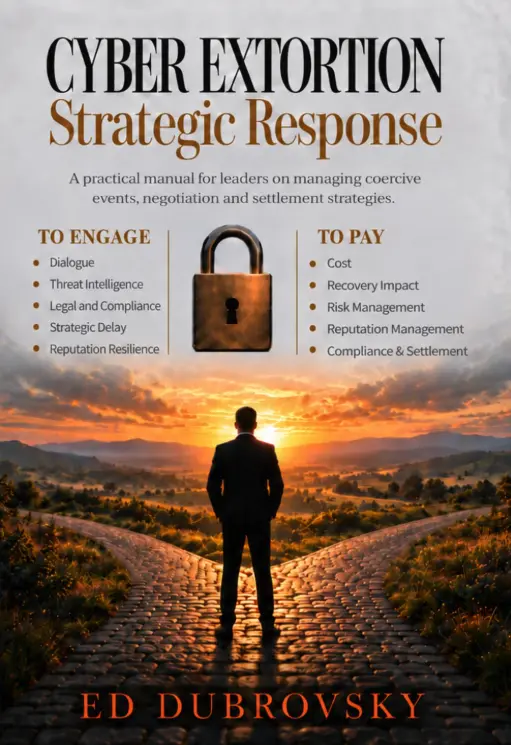
The investigation appears to center on the complex, often opaque world of ransomware negotiation. Dubrovsky, who is the author of Cyber Extortion Strategic Response, a 252-page professional guide on handling digital ransom demands, has built a career advising organizations on how to manage the fallout of cyber-attacks. His book emphasizes the delicate nuances of crisis management, arguing that "communicating with a criminal is not the same as negotiating a payment."

In his professional writing, Dubrovsky posits that organizations can use engagement as a strategic tool to gather intelligence, verify the authenticity of stolen data, and buy time for recovery efforts. However, federal investigators appear to be testing the boundary between legitimate professional negotiation and illegal conspiracy. Federal court records indicate that an "Edward Dobrovsky"—with a slight spelling variation—was arrested on charges of "conspiracy to threaten to impair the confidentiality of information with the intent to extort money" and "interference with commerce by threats."
These charges strike at the heart of the "business model" utilized by groups like ShinyHunters. The collective typically targets software-as-a-service (SaaS) companies, leveraging phishing attacks and stolen credentials to gain unauthorized access to internal corporate databases. Once they have successfully siphoned sensitive information, the group demands exorbitant ransoms, threatening to publish the data on public forums if their financial requirements are not met. By the FBI’s own estimates, ShinyHunters has successfully extorted over $70 million from victims in the current calendar year alone.
A Shifting Legal Landscape
The case against the suspect has already begun to move through the federal judicial system. While the inmate locator at the U.S. Bureau of Prisons confirmed that a 54-year-old Edward Dubrovsky was held in a Philadelphia federal facility, court dockets indexed by CourtListener reveal a critical procedural development: on October 9, the case was transferred to the Eastern District of Texas. Sources familiar with the internal operations of the FBI suggest that the Texas field office has been designated as the centralized command center for the entire ShinyHunters investigation, reflecting the high priority the agency has placed on dismantling the group’s infrastructure.
The legal proceedings remain in their early stages. As of the most recent filings, court records show that the defendant has not yet secured private legal counsel and has not been appointed a public defender. The core of the complaint remains under seal, leaving the public and industry observers to infer the extent of the evidence against him from the broader, ongoing investigation into the group’s recent activities.

The Hunt for ShinyHunters
The arrest of Dubrovsky is the latest in a rapid succession of law enforcement actions aimed at the leadership and support networks of ShinyHunters. The FBI has been aggressively reviewing data seized from devices recovered last month during the arrest of Pepijn van der Stap, a convicted cybercriminal apprehended by Dutch police. Investigators believe that the information contained on these devices is providing a roadmap to the group’s hierarchy, and they have signaled that additional charges against other individuals associated with companies specializing in ransomware negotiation may be on the horizon.
The stakes for the FBI became personal recently when ShinyHunters managed to breach the agency’s own recruitment portal. The stolen data included highly sensitive information, such as the unit specializations, medical histories, and psychiatric records of thousands of agents. Following the arrest of Van der Stap, the group’s leadership was assumed by an individual using the handle "Rey," who began a campaign of public taunts directed at the FBI.
"Rey" was subsequently identified by authorities as a teenager named Saif Al-din Khader. Reports from last week indicate that Khader has been detained and is currently cooperating with federal investigators. The investigation into Khader’s activities revealed that the group was in the midst of a brazen extortion attempt against a navigation and digital aviation unit formerly part of the Boeing corporation.
As the FBI continues to pore over the digital trail left by the group, the arrest of a prominent industry voice like Dubrovsky serves as a stark reminder of the thin, shifting line between those who negotiate with cyber-extortionists and those who may be accused of facilitating them. For the cybersecurity community, the case is a developing flashpoint that raises fundamental questions about the protocols, ethics, and legal risks involved in responding to the modern epidemic of digital extortion. With the case now centralized in Texas and the investigation into the broader network continuing, further developments are expected in what has become one of the most significant federal probes into cyber-extortion in recent memory.