A Florida-based technology firm that marketed itself as a high-end savior for victims of digital extortion has been revealed as a sophisticated fraudulent operation. The co-founder and chief technology officer of "RansomwareHelp," a business that operated for six years under the guise of providing advanced cryptographic restoration services, has been charged with wire fraud. Federal investigators allege the company did not use any proprietary technology to unlock data; instead, it simply paid ransomware attackers for decryption keys and charged desperate victims a massive, hidden markup for work that was never performed.
The indictment, returned this week in a Rhode Island federal court, names 52-year-old Juan Ricardo Palacio Escobar, a resident of Miami and Medellin, Colombia, as the architect of the scheme. According to court documents, while the company’s marketing materials promised a 99 percent success rate and insisted on a firm policy against negotiating with cybercriminals, the reality was a deceptive cycle of secret payments and exorbitant overcharging.
The Illusion of Expertise
RansomwareHelp’s website was a masterclass in professional deception. Targeting organizations in the midst of a crisis, the site urged victims to "Do not pay the ransom!" and promised that its "cryptography experts" utilized proprietary tools and algorithms to restore data, servers, and systems to their original state.
The company’s marketing copy was designed to instill confidence in non-technical business owners, boasting of "over 28 years of experience" and a team of 80 experts specializing in cybersecurity, forensic analysis, and reverse engineering. The site’s messaging was emphatic, explicitly stating, "We never promote, intermediate or pay ransom to threat actors on behalf of our clients."
However, investigators paint a starkly different picture. The indictment alleges that Palacio routinely engaged with ransomware groups to secure decryption keys for his clients’ encrypted files. Once the key was obtained, he would invoice the victim for significantly more than the cost of the ransom, framing the charges as fees for "advanced diagnostic assessments" and "proprietary decryption algorithms."

The FBI Sting Operation
The unraveling of the RansomwareHelp operation was the result of a coordinated FBI sting. Federal agents established a two-pronged operation: they posed as both a legitimate company suffering from a ransomware attack and as a fictitious group of cyber-extortionists.
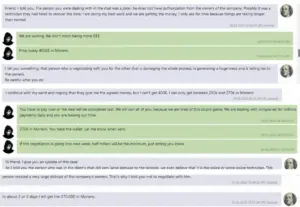
When the undercover agents, acting as the "victim" firm, reached out to RansomwareHelp, the company followed its established script, reassuring the "victims" that they would never negotiate with criminals. Shortly after this exchange, however, Palacio contacted the FBI’s fake ransomware group, posing as an intermediary. He requested the lowest possible price for a decryption key.
The FBI investigators, playing the role of the threat actors, quoted a price of 0.2 bitcoin, which equated to approximately $13,000 at the time. Less than 48 hours later, Palacio returned to the "victim" firm, claiming that his diagnostic assessment had been a success. He quoted the victim a price of $13,260, pocketing the difference.
The deception continued the following day. Palacio contacted the FBI’s fake ransomware group again, this time negotiating the price of the decryption tool down to $4,000. Ultimately, the price was settled at roughly $6,000 in bitcoin. Palacio, however, maintained his original demand to the victim, charging a total of $16,010—a figure that included a $2,750 "diagnostic fee" on top of the $13,260 cost he had previously quoted for the decryption.
Behind the Curtain: Victim Experiences
The indictment against Palacio echoes reports from independent security professionals who have long suspected the legitimacy of such "remediation" firms. Paul Ihme, co-founder of the security firm Soteria, recalled a 2024 case involving a small accounting firm that had sought help from RansomwareHelp following a Lockbit ransomware infection.

The firm had been locked out of all its internal and client data. RansomwareHelp provided a proposal for recovery totaling $438,880. The document was filled with technical jargon meant to justify the exorbitant cost, claiming the work included the "professional configuration of forensic servers," "expert engineering hours," and multiple "processing cycles" for decryption.
The proposal even went so far as to claim that the company would use "510 preconfigured forensic servers" of "maximum quantitative capacity" located across the globe to reverse-engineer the encryption. Furthermore, the company promised that its programmers would "inject randomly the encryption codes" using "brute force processes."
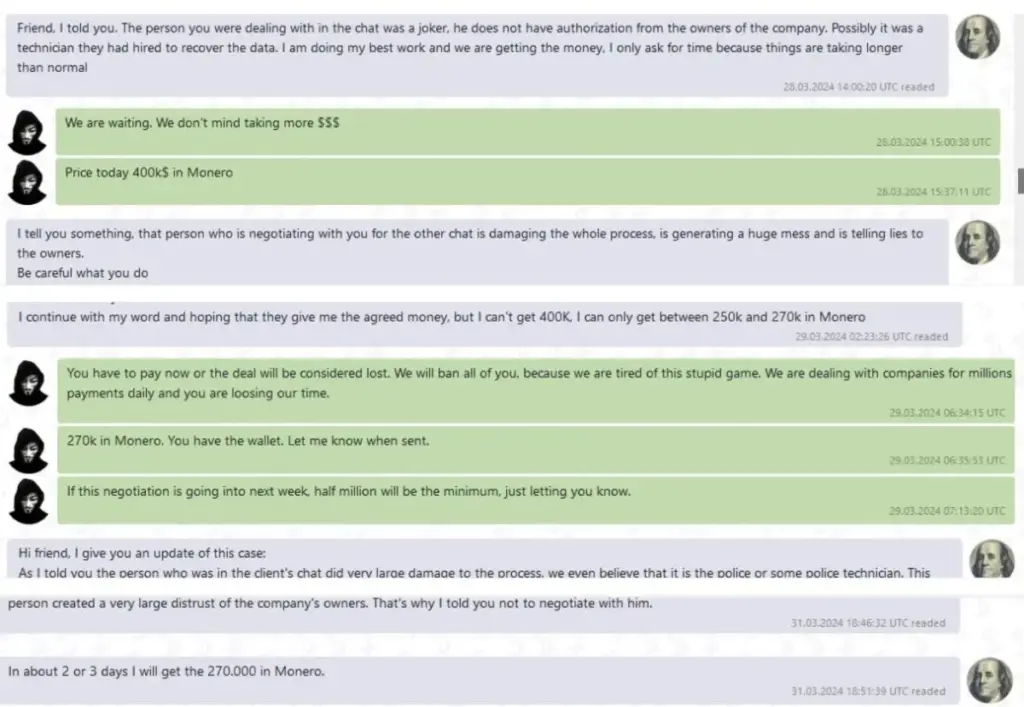
Beyond the absurd technical claims, Ihme noted that RansomwareHelp insisted on unrestricted remote access to the victim’s network, using software like Anydesk. Ihme believes this access served a dual purpose: it allowed the firm to delete any ransomware notes left behind by the actual attackers.
"A legitimate firm would say, ‘Hey, send us a copy of the ransom note,’" Ihme explained. "What they were doing is using that access to delete ransomware notes off the systems. The only reason they would do that is to prevent the victim from jumping into that chat itself."
By controlling the communication channel, RansomwareHelp ensured the victim could not negotiate directly with the hackers, thereby protecting their own middleman fee. In the case of the accounting firm, the strategy backfired. The victims discovered that someone was already negotiating with the Lockbit group, and the hackers, annoyed by the multiple parties involved, began increasing the ransom demand by $100,000 per day. The accounting firm eventually fired RansomwareHelp and hired a legitimate security firm, which helped them recover their data for half of what Palacio had intended to charge.

A Growing Trend of Fraud in Cybersecurity
The prosecution of Palacio is part of a broader crackdown by the U.S. Department of Justice on companies that claim to provide cybersecurity remediation while allegedly conspiring with or deceiving their clients.
In early October, the government charged 54-year-old Edward Dubrovsky, an executive at the Canadian firm Cybersteward, with cyber extortion and conspiracy. Shortly thereafter, Zohar Pinhasi, the 50-year-old CEO of MonsterCloud, was charged with wire fraud. Prosecutors allege Pinhasi paid $8 million to ransomware groups while charging his clients $19 million for "remediation" services that never involved the proprietary decryption tools he claimed to possess.
These cases highlight a disturbing trend where firms exploit the panic and technical ignorance of small to medium-sized businesses. As experts like Ihme have pointed out, the technical claims made by these fraudulent companies are often patently farcical—referencing irrelevant password hashing algorithms or impossible decryption scenarios that, if true, would make the perpetrators the most successful cryptographers in human history.
In July, the legal pressure on such actors was further cemented when Angelo Martino, a 41-year-old ransomware negotiator from Florida, was sentenced to 70 months in prison. Martino had been caught conspiring with the Blackcat/ALPHV group, providing the hackers with confidential information about his clients’ financial positions to help the criminals maximize their extortion demands.
As the Department of Justice continues to pursue these cases, the message to the industry remains clear: businesses seeking help in the aftermath of a ransomware attack must exercise extreme caution. The case of RansomwareHelp serves as a sobering reminder that in the high-stakes world of digital extortion, the "help" being offered may be just as dangerous as the threat it claims to resolve.