In a significant escalation of the federal government’s ongoing battle against high-profile cybercrime syndicates, FBI agents arrested a prominent Canadian cybersecurity executive in Pennsylvania this past Thursday. The individual, identified through court records as Edward Dubrovsky, is facing serious federal charges in connection with the notorious hacking collective known as "ShinyHunters." This group has recently been the focus of an intense investigation after orchestrating a brazen breach that compromised sensitive personal and professional data belonging to thousands of FBI personnel.
The arrest, which was confirmed by multiple sources familiar with the matter, highlights the converging worlds of legitimate cybersecurity consulting and the murky, often dangerous, territory of ransomware negotiation. While the FBI has remained tight-lipped regarding the specific details of the ongoing investigation, the arrest marks a pivotal moment in the government’s pursuit of a group that has successfully extorted more than $70 million from victims throughout 2026 alone.
A High-Stakes Conference and a Swift Arrest
According to sources close to the investigation, the arrest took place while the suspect was attending the Cyber Risk Summit, a professional gathering held at the Loews Philadelphia Hotel between October 5 and October 7. The suspect, whose company specializes in advising organizations through the harrowing process of ransomware negotiations and cyber extortion incidents, was reportedly in the city to participate in the summit.
Public records and event documentation indicate that the summit’s largest sponsor was the Canadian security firm Cypfer. LinkedIn records link the arrested individual, Edward Dubrovsky, to the founding of Cypfer, as well as his current association with another firm, CyberSteward. In a social media post published roughly one month prior to the conference, Dubrovsky expressed his intent to attend the summit alongside his colleagues from CyberSteward to engage in discussions regarding the nuances of "compliant-driven coercive advisory" and global settlement services.
Federal court documents, indexed via CourtListener, show that an individual named Edward Dobrovsky—a spelling variation of the suspect’s name—was taken into custody on October 8. The charges listed in the court filings are severe, including "conspiracy to threaten to impair the confidentiality of information with the intent to extort money" and "interference with commerce by threats." While the core complaint remains under seal, the summary of the charges paints a picture of an individual alleged to have crossed the line from professional negotiator to an active participant in criminal extortion schemes.
Escalation in the Eastern District of Texas
The legal proceedings have already begun to shift. Although an inmate locator at the U.S. Bureau of Prisons initially placed the 54-year-old Dubrovsky at a federal facility in Philadelphia, a notice filed on October 9 indicated that the case has been moved to the Eastern District of Texas. This transfer is particularly noteworthy, as sources suggest the FBI has centralized the entirety of its complex ShinyHunters investigation within the Texas field office, signaling that the authorities view this case as a matter of significant national security priority.

The FBI declined to provide an official comment on the arrest, citing the sensitivity of the ongoing investigation. As of the latest filings, court records indicate that Dubrovsky does not currently have legal representation on file, and the court has yet to appoint a public defender to the case.
The Business of Extortion
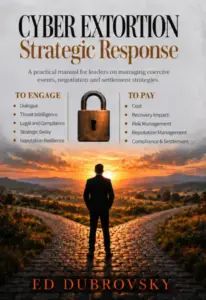
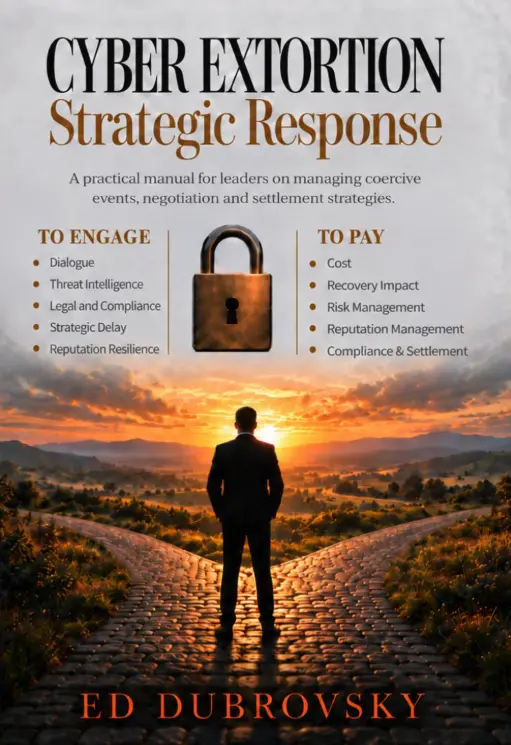
The arrest of a professional who literally wrote the book on the subject adds a layer of irony to an already complex criminal case. Dubrovsky is the author of Cyber Extortion Strategic Response, a 252-page work that purports to guide organizations through the decision-making processes required to recover from ransomware attacks. The book, as described in its promotional materials, promises to take readers "beyond the ransom note."
Perhaps most intriguing in light of his current legal troubles is a passage from the book featured on Amazon: "At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay. Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."
Investigators are now tasked with determining whether the suspect’s "engagement" with these criminal entities remained within the bounds of professional advisory or if those interactions crossed into the realm of facilitating the very crimes he claimed to help companies avoid.
A Pattern of Pursuit Against ShinyHunters
The ShinyHunters group has carved out a reputation for using aggressive tactics, primarily relying on phishing campaigns and the exploitation of stolen credentials to siphon massive amounts of data from software-as-a-service (SaaS) companies. Their modus operandi typically involves the theft of sensitive corporate data, followed by threats to leak that information publicly unless a ransom demand is met.
The arrest of Dubrovsky follows a string of recent law enforcement successes against the group. Last month, Dutch police arrested Pepijn van der Stap, a convicted cybercriminal whose seized devices have reportedly provided the FBI with a wealth of intelligence. Sources suggest that the FBI is currently poring over the data contained within those devices, and that further charges against other principals at companies specializing in ransomware negotiation could be on the horizon.

The stakes for the FBI were raised significantly when ShinyHunters managed to breach the agency’s own recruitment portal. The stolen data included highly sensitive information, such as unit designations, professional specializations, and even medical and psychiatric records of thousands of agents. Following the arrest of Van der Stap, a new leader known as "Rey" took control of the group, using the stolen FBI data to taunt the agency publicly.
However, the reign of "Rey" was short-lived. Last week, Reuters reported that the individual behind the handle—a teenager identified as Saif Al-din Khader—had been detained and was actively cooperating with federal investigators. Khader’s apprehension was reportedly tied to the group’s attempt to extort a navigation and digital aviation unit that had been divested by Boeing in 2025.
Moving Forward
As the federal case against Dubrovsky progresses in the Eastern District of Texas, the cybersecurity community is left to reckon with the implications of the arrest. The line between being a facilitator of legal settlements and a co-conspirator in extortion is one that the Department of Justice is increasingly willing to police.
For now, the case remains in its early stages. The FBI’s silence on the matter, combined with the rapid movement of the case to Texas, suggests that this is merely one chapter in a much larger investigation. With multiple suspects now in custody and a vast amount of digital evidence being processed, the saga of the ShinyHunters and those who allegedly enabled their activities is far from over. As more details emerge, the legal community and cybersecurity firms alike will be watching to see how the government distinguishes between the essential work of crisis negotiation and the criminal enterprise of extortion.