Security researchers have issued a stark warning regarding a significant cybersecurity vulnerability affecting the Executive Office of the President: multiple computers and mobile devices connected to the White House network appear to be functioning as nodes for residential proxy services. These services, which allow third parties to rent out a user’s internet connection to mask their own traffic, have effectively turned high-security government endpoints into exit points for anonymous internet activity, potentially exposing sensitive infrastructure to external exploitation.
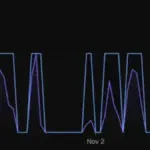
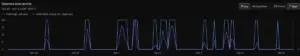
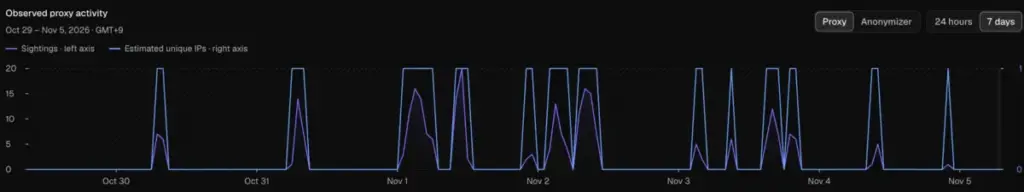
The breach was first identified by Layer3 Intel, a security firm that monitors network traffic anomalies. According to the firm’s findings, multiple residential proxy nodes were detected beaconing out from the specific internet address network reserved for the Executive Office of the President, identified as AS2650. The data suggests that this activity was not an isolated incident but a persistent phenomenon. Layer3 Intel reported that between October 5 and November 3, it observed proxy traffic exiting the White House network on 236 separate occasions.
The implications of this discovery are compounded by the nature of the proxy services involved. Among the services identified is Infatica, a proxy provider founded by Vladimir Fomenko. Fomenko, a Russian national, was previously linked to a hosting firm called King Servers, which gained notoriety in 2016 for providing the infrastructure used by Russian state security services to execute cyberattacks against election databases in Arizona and Illinois.
The presence of Infatica on the White House network was corroborated by the proxy-tracking firm Synthient, which noted on social media platform X that the traffic originating from AS2650 was consistent with Windows 11 installations of the Infatica software. Infatica is frequently bundled into "free" desktop and mobile applications, often embedded within software development kits (SDKs) that allow developers to monetize their applications by selling access to the user’s bandwidth. When a user installs such an application, they may inadvertently grant the service permission to route traffic through their device, effectively turning their hardware into a proxy server for whoever purchases access from the provider.
The mechanics of these residential proxy networks are simple but dangerous. By design, they enable customers to rent the residential IP addresses of unsuspecting users to anonymize their online behavior or spoof their geographic location. From the perspective of any website visited by the proxy user, the traffic appears to originate from the device—and, in this case, the network—of the person renting the bandwidth. If that device is located within the White House, the traffic carries the perceived legitimacy and authorization of the Executive Office’s network.
Layer3 Intel’s analysis revealed that the unauthorized traffic was not limited to a single provider. In an alarming discovery, the firm found that as many as 28 separate residential proxy services were capable of routing traffic through the White House’s network. This indicates a widespread issue of employee-owned or managed devices connecting to the government network while simultaneously hosting software that turns those devices into public proxy gateways.
"This is public access," the Layer3 Intel team stated in a report detailing the findings. "Anybody can obtain it by signing up to a public residential proxy service, paying a few dollars and sending requests through it. We did not selectively target this network or try to make our probes exit from it. We caught this by chance, simply by requesting global rotating access through these services."
The activity, which occurred on 26 of the 30 days analyzed, showed a distinct pattern: most of the proxy traffic was recorded in the evening hours, specifically between 5:00 p.m. and midnight, suggesting that the devices may be personal computers or mobile devices brought into the workplace by staffers. The White House has not yet provided a formal response to requests for comment regarding these security findings.
The broader risks associated with residential proxies are significant and well-documented. These services are frequently employed by cybercriminals to facilitate account takeovers, advertising fraud, and large-scale data scraping operations, often for the training of artificial intelligence models. However, the risk extends beyond simple traffic obfuscation. Security researchers have repeatedly warned that these networks serve as a conduit for malicious actors to probe internal, private networks.
In late 2025, security analysts uncovered a massive campaign where cybercriminals exploited vulnerabilities in these proxy services to perform reconnaissance on the local networks of the devices acting as proxies. By gaining control over the proxy endpoint, attackers could pivot into the local network, searching for unpatched systems or vulnerable infrastructure to infect with malware.
This threat was highlighted further in January 2026, when Synthient founder Ben Brundage demonstrated how attackers were abusing these vulnerabilities to gain administrative control over devices residing on the same local networks as the proxy-enabled machines. "Some of these resellers sell bandwidth for as low as 60 cents a Gigabyte, that means for less than a dollar you can gain access into some of the most confidential and trusted networks," Brundage told KrebsOnSecurity. He added that the lack of rigorous "Know Your Customer" (KYC) processes within the reseller ecosystem allows virtually anyone—including state-sponsored actors or sophisticated cybercriminal syndicates—to purchase access to these high-value networks for a negligible cost.
The incident at the White House is emblematic of a much larger, systemic problem in both government and corporate environments. While residential proxy services are often marketed as tools for marketing research or web development, they frequently operate in a grey area of legality and security. The integration of these services into common consumer applications means that even sophisticated organizations struggle to prevent them from entering their perimeters via employee devices.
Data from the proxy tracking firm Spur suggests that the problem is pervasive. In a webinar conducted earlier this year, Spur researchers identified residential proxies in nearly 300 government-operated networks, alongside hundreds of utility companies, healthcare providers, and financial institutions. Similarly, the security firm Infoblox reported that a staggering 65% of its customer base had been observed querying domains associated with residential proxy services, underscoring the ubiquity of these networks in the modern digital landscape.
The situation underscores a growing challenge for IT and security administrators: the difficulty of maintaining a secure perimeter when employees introduce unauthorized software into sensitive environments. For organizations as critical as the White House, the presence of these proxies represents not just a minor security oversight, but a potential vector for espionage and systemic compromise, as the very nature of these networks makes it nearly impossible to distinguish between a legitimate, authorized connection and one being leveraged by a malicious third party.