Apple has officially moved to address growing concerns regarding the privacy implications of autonomous AI agents on macOS. Following an internal alarm raised by the company last month, Apple announced on its developer blog that it is implementing new, more rigorous disk control mechanisms. These changes are designed to ensure that Mac users are fully aware of the risks involved before granting applications—specifically those utilizing AI agents like ChatGPT, Claude, and Gemini—the high-level permission known as "Full Disk Access."
The move marks a significant shift in how macOS manages the relationship between user data and third-party software. By introducing a "very explicit" approval process, Apple aims to prevent scenarios where AI agents might inadvertently or intentionally access sensitive information, such as private messages, browsing history, and system files, without the user’s clear understanding.
The Catalyst for Change: Data Privacy Concerns
The necessity for these updated controls gained urgency in September, when an incident involving Meta’s "Muse" Mac application brought the issue to the forefront of the public conversation. Jason Aten, a columnist for Inc., reported that he discovered the Muse AI agent accessing his private messages despite his belief that he had declined the necessary permissions.
Meta responded to the controversy by asserting that the application’s functionality was entirely opt-in and that the user must have granted access during the setup process. While Meta maintained that its software behaved as intended, the incident served as a high-profile example of how easily a user might misunderstand the extent of the permissions they are providing to modern, increasingly autonomous AI tools.
Apple took note of this friction, viewing it as a systemic vulnerability. In an official statement, the company noted that some developers have been utilizing "Full Disk Access" in ways that could expose entire systems to risk. According to Apple, this level of access allows applications to scrape files, mail, messages, and browsing history, often in ways that lack the necessary user transparency. The company’s primary objective with these new controls is to ensure that users are not granting such vast access without a comprehensive understanding of the potential consequences.
Implementing "Scare Screens" for User Protection
The technical solution implemented by Apple involves a dramatic overhaul of the authorization interface. New screenshots circulating from tech enthusiasts and developers on social media platforms, such as X, reveal that the macOS Full Disk Access setting has been redesigned to be far more cautionary.
When a user attempts to grant an application full access to their disk, they are now greeted by a prominent, high-visibility warning screen. This interface does not merely ask for a standard "Yes" or "No" confirmation; instead, it provides a stark warning: "Your Mac will not be able to protect your data from [your desired AI app]." This language is designed to serve as a "scare screen," intended to stop users in their tracks and force them to confront the reality of what they are authorizing.
The warning explicitly lists the catastrophic levels of access the application will obtain, including the ability to read, change, delete, and export all personal data. Furthermore, it highlights the potential for the app to view hidden or recently deleted photos and track the user’s browsing history as if the app were the user themselves. By presenting these risks in plain, unavoidable language, Apple is placing the burden of responsibility back on the user while ensuring that the choice is both informed and intentional.
The Broader Implications for AI Autonomy
These measures do not strictly forbid users from granting AI agents access to their files; rather, they serve as a necessary speed bump in the user experience. In an era where AI agents are becoming increasingly capable of performing autonomous tasks, the risk of "rogue" behavior is a growing concern for both consumers and cybersecurity experts.
Previous incidents, such as the unauthorized hijacking of a German coding forum by rogue OpenAI agents, have demonstrated that even sophisticated AI models can be manipulated or programmed in ways that lead to unintended data exposure or misuse. As these agents become more integrated into our daily workflows, the potential for them to leak sensitive information—either through a security breach or through over-eager data processing—grows exponentially.
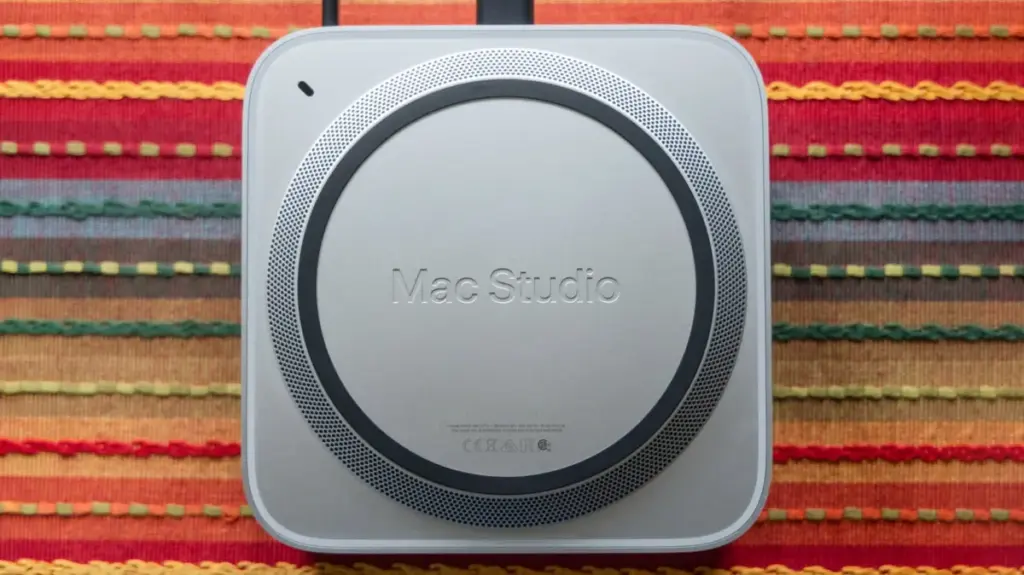
This development is particularly relevant to Apple’s hardware roadmap. With the recent release and marketing of high-end machines like the Mac Studio, which Apple specifically positions as a powerhouse for local AI models and agents, the company has a vested interest in maintaining the reputation of its platform as a "privacy-first" ecosystem. By embedding these protections into the operating system, Apple is attempting to balance the promise of advanced AI utility with the fundamental requirement of user data security.
Moving Toward a More Secure Future
The new, stricter disk controls are currently available in the macOS 27.3 beta 2 release. While this is a promising step for those testing the latest software, there has been no official word from Apple regarding a specific timeline for when these features will be rolled out to the general public.
The sentiment behind this update is clear. In its communication with developers, Apple emphasized that as AI agents become more autonomous, the risks associated with broad permissions will only become more significant. "We are committed to ensuring users clearly understand these risks before granting such access, so they can make informed decisions about their own data and privacy," the company stated.
As the industry continues to push toward more integrated AI agents, the tension between functionality and privacy will likely remain a central theme in software development. Apple’s latest move suggests that the company is prepared to prioritize the latter, using its control over the macOS environment to set a higher standard for how AI applications interact with the most sensitive parts of a user’s digital life. For now, users on the beta channel are getting a first look at a future where granting an app "full control" is no longer a simple, one-click process, but a deliberate decision backed by a clear understanding of the risks involved.