In a significant escalation of the federal government’s campaign against one of the most prolific cybercrime syndicates in operation today, FBI agents have arrested a high-profile executive from a Canadian cybersecurity firm. The arrest, which took place in Pennsylvania this past Thursday, is directly linked to an ongoing, high-stakes investigation into the hacking group known as "ShinyHunters"—an organization that recently succeeded in compromising the FBI itself, exfiltrating sensitive data pertaining to thousands of bureau agents.
The arrest was first signaled by reports from The New York Times, which confirmed that a Canadian national had been taken into custody in Pennsylvania on suspicion of providing material assistance to the ShinyHunters collective. While official channels have remained tight-lipped regarding the identity of the suspect—including a brief statement on X (formerly Twitter) from FBI Director Kash Patel that confirmed an arrest but omitted specific details—multiple sources familiar with the matter have confirmed to KrebsOnSecurity that the individual in question is Edward Dubrovsky.
A Professional Caught in the Crosshairs
According to sources close to the investigation, the arrest occurred under circumstances that highlight the blurred lines between legitimate cybersecurity defense and the criminal underworld. The suspect was in Philadelphia to attend the annual Cyber Risk Summit, a high-level industry event held at the Loews Philadelphia Hotel between October 5 and October 7. The individual’s professional background is deeply rooted in the very sector currently under the microscope: the specialized niche of ransomware negotiation and digital extortion advisory.
The suspect’s company, which had a prominent presence at the conference as a major sponsor, focuses on managing the delicate, high-pressure negotiations that occur when organizations are held hostage by cybercriminal syndicates. Federal court records, despite some initial confusion regarding the spelling of the suspect’s surname, reveal that an individual identified as Edward Dobrovsky was arrested on October 8 on charges of cyber extortion and conspiracy. While the core complaint remains under seal, publicly accessible documents indexed by Courtlistener indicate that the defendant faces charges including "conspiracy to threaten to impair the confidentiality of information with the intent to extort money" and "interference with commerce by threats."
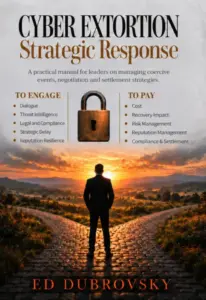
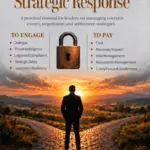
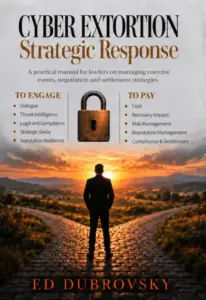
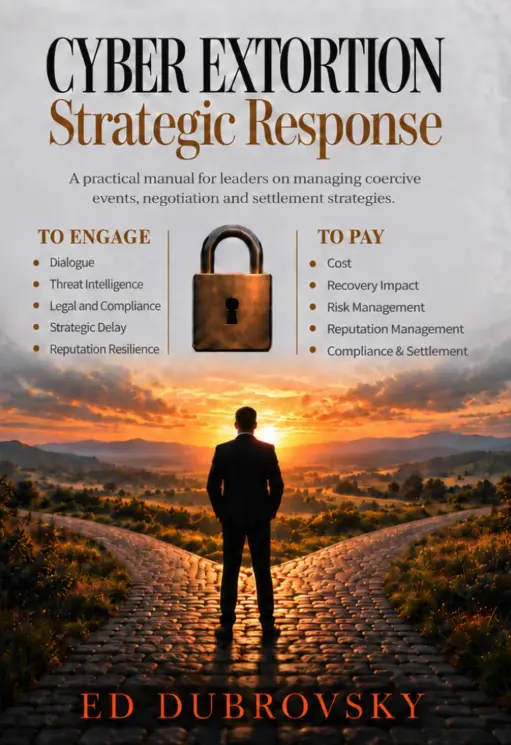
The suspect’s career has been characterized by a public commitment to the ethics of incident response. Notably, Dubrovsky is the author of Cyber Extortion Strategic Response, a 252-page professional guide intended to assist organizations in navigating the aftermath of a ransomware attack. In the book’s promotional materials, Dubrovsky emphasizes the importance of distinguishing between communication and compliance. "At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay," the book’s Amazon listing reads. "Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."

The irony of an author of a manual on extortion response now facing charges related to that very subject has sent shockwaves through the cybersecurity industry. Following the news of the arrest, a spokesperson for Cypfer—the Canadian firm where the suspect previously served as a managing director until December 2025—clarified that while the suspect had claimed to be a founder on his professional profile, he had never held that title.
Centralizing the Hunt for ShinyHunters
The logistical handling of the case provides further insight into the FBI’s current strategic priorities. Sources have indicated that the federal investigation into ShinyHunters has been significantly centralized, with control now consolidated at an FBI field office in Texas. This movement was reflected in the court dockets; although the suspect was initially detained in Philadelphia and processed by the U.S. Bureau of Prisons, a notice filed on October 9 indicated that the case had been formally transferred to the Eastern District of Texas.
This centralization suggests a broader, more aggressive push by the Department of Justice to dismantle the leadership and infrastructure of the ShinyHunters group. The group, which has gained notoriety for its sophisticated use of phishing and stolen credentials to infiltrate software-as-a-service (SaaS) providers, has been remarkably successful in its illicit operations. According to recent FBI estimates, the group has successfully extorted more than $70 million from victims within this year alone.
The investigation appears to be reaching a fever pitch. Federal agents have reportedly been conducting a meticulous forensic analysis of devices seized last month during the arrest of Pepijn van der Stap, a convicted cybercriminal apprehended by Dutch authorities. The success of that international operation provided a wealth of data that has likely informed the current wave of arrests. Sources have hinted that the charges against the Canadian executive may be merely the beginning, with additional legal actions against principals at other ransomware negotiation firms potentially forthcoming as investigators continue to map the connections between legitimate security professionals and the criminal groups they are hired to engage.
The Rise and Fall of "Rey"
The ShinyHunters group has demonstrated a remarkable, if volatile, resilience, even in the face of mounting pressure. Following the arrest of Van der Stap, a new, younger figurehead known as "Rey" assumed control of the group. Under Rey’s leadership, the group shifted from mere corporate extortion to a more provocative stance, openly taunting the FBI.

The hackers successfully breached the FBI’s own online recruitment portal, a move that exposed highly sensitive data, including the unit and specialization of agents, as well as private medical and psychiatric records. This breach marked a new, dangerous chapter in the bureau’s battle with the group.
However, the group’s momentum was short-lived. Last week, news broke via Reuters that "Rey" had been identified as a teenager named Saif Al-din Khader. Khader has since been detained and is reportedly cooperating with federal investigators. The apprehension of Khader followed a botched extortion attempt directed at a navigation and digital aviation unit, an entity that had been divested by Boeing in late 2025.
As the case against Edward Dubrovsky proceeds in the Eastern District of Texas, the cybersecurity community remains in a state of high alert. The lack of legal representation for the defendant in the initial court filings, coupled with the sensitivity of the evidence and the high-profile nature of the victim—the FBI itself—suggests that this will be a complex and fast-moving legal battle. For now, the defendant remains in federal custody, and the industry is left to grapple with the implications of an investigation that has moved from the outskirts of the cybercrime world into the boardrooms of the firms tasked with fighting it. As federal prosecutors continue to piece together the architecture of the ShinyHunters’ network, the case stands as a stark reminder of the thin line between those who negotiate with criminals and those who collaborate with them.