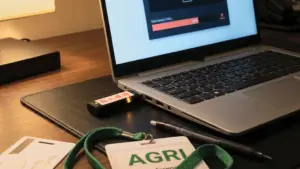
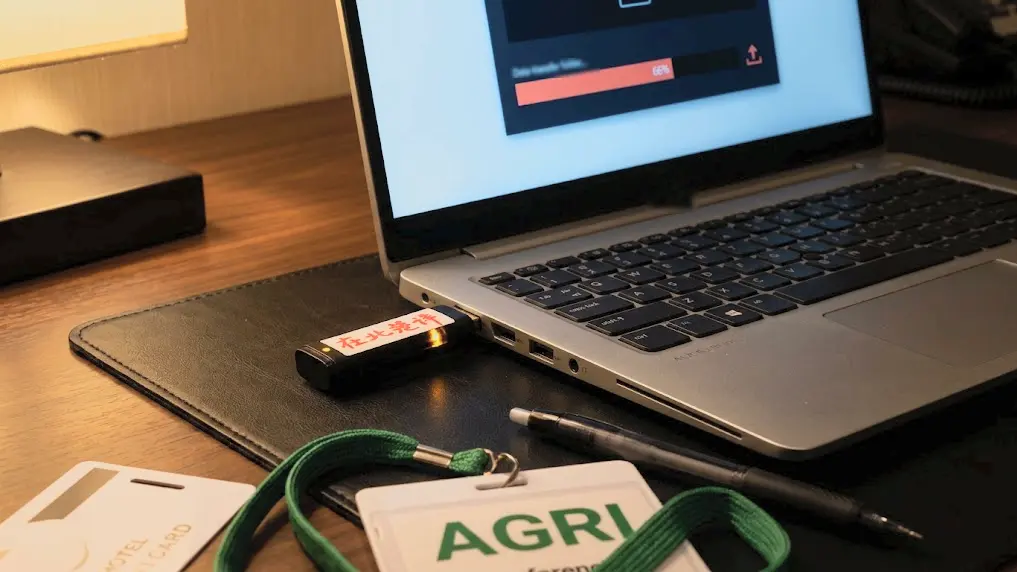
In a chilling display of physical-world espionage, a state-linked Chinese hacking group known as OVERCAST PANDA has successfully compromised the laptops of high-ranking agricultural industry executives by physically infiltrating their hotel rooms. The operation, which occurred this spring during an industry conference on Hainan Island, bypassed modern cybersecurity staples like multi-factor authentication, network firewalls, and phishing filters by opting for a low-tech, high-impact approach: gaining entry to private rooms while the victims were at dinner to boot their devices from a malicious USB stick.
CrowdStrike, the cybersecurity firm that monitors OVERCAST PANDA, detailed this sophisticated campaign in its 2026 Threat Hunting Report. According to Adam Meyers, CrowdStrike’s senior vice president of counter adversary operations, the operation represented a rare and deliberate departure from standard remote intrusion tactics. During the Hainan conference, investigators tracked an intruder entering one executive’s room at approximately 8 p.m. local time, with a second room breached by 9:57 p.m. In both instances, the attackers gained direct access to the hardware, writing a persistent backdoor known as FlowCloud directly to the laptop storage before rebooting the machines and exiting.
Because the intrusion occurred entirely at the hardware level, there was no digital footprint left on the corporate network during the initial compromise. No phishing email was sent, no credentials were stolen via a malicious portal, and no network traffic was intercepted. The compromise was effectively completed while the operating system was dormant.
The Evolution of the "Evil Maid" Attack
The methodology employed by the group is a modern iteration of the "evil maid" attack, a concept popularized in 2009 by security researcher Joanna Rutkowska. The term refers to any scenario where an attacker with physical access to an unattended device compromises it by booting from external media. While such attacks have long been a theoretical concern for high-value targets, they remain relatively rare among the 290 distinct adversary groups tracked by CrowdStrike.
While other groups, such as the China-based MUSTANG PANDA, have utilized USB-based attacks, their methods typically rely on the victim being tricked into plugging in a malicious device themselves. What makes the Hainan incident uniquely concerning is the combination of state-backed physical intelligence operations—likely involving the Ministry of State Security or associated proxies—with advanced malware deployment that requires no user interaction.
The malware, FlowCloud, is not new, but its application in this context is highly refined. First documented by Proofpoint in 2020 during campaigns targeting U.S. utilities, and later observed by NTT Security’s SOC in attacks against Japanese organizations, FlowCloud is a robust tool designed for deep espionage. When the executives returned to their rooms and powered on their laptops the following morning, the hidden trigger fired, loading the backdoor. Once the operating system initialized, the malware began its work: keylogging, screen capturing, systematic file collection, and harvesting stored credentials.
According to Meyers, the security firm’s Falcon platform was able to detect the threat, but only after the OS had finished loading and the security agent initialized. "We have the visibility once the machine boots up," Meyers explained. The critical vulnerability, however, remained the "blind spot" between the moment the USB stick was inserted in the hotel room and the moment the user logged back in the next day.
The Persistent Threat to Corporate Security
This disclosure arrives at a pivotal moment for CrowdStrike, which used its annual Fal.Con 2026 conference in Las Vegas to unveil a new suite of AI-driven security tools, including Falcon Guardian and the SafeMind agentic system. However, the OVERCAST PANDA incident serves as a stark reminder that even as the industry pivots toward AI and cloud-native defense, the "old-fashioned" threat of physical compromise remains a potent weapon for intelligence services.
The targeting of an agricultural conference is not arbitrary. Meyers noted that the collection priorities identified in the campaign align closely with China’s stated five-year economic and strategic plans. By accessing the devices of key industry decision-makers, the state-sponsored actors were able to circumvent the very digital perimeters that corporations spend billions of dollars to reinforce.
The report also highlighted that this was not an isolated event. A separate intrusion in mid-2026 targeted a U.S.-based media professional using identical tradecraft. These incidents underscore a sobering reality: when a nation-state intelligence service decides to compromise a specific target, they are not limited by the reach of the internet. They can leverage local hotel staff, bribe or coerce individuals with access to room keys, or simply use professional break-in expertise to overcome the security controls that executives rely on every day.
Why Modern Defense Architectures Fail to Prevent Physical Tampering
The fundamental issue, as Meyers points out, is that the current generation of Endpoint Detection and Response (EDR) and AI security tools assumes the existence of a running, secure operating system. EDR requires the OS to be loaded and the security agent to be active. MFA is only as effective as the login screen it protects. When an attacker gains physical control of the hardware, they are operating "below" the layer where these digital defenses exist.
The OVERCAST PANDA campaign bypassed every modern security layer because it functioned in the pre-boot environment. By the time Falcon caught the malicious process, the implant and its corresponding triggers were already embedded in the system’s storage.
Meyers emphasized that while hotel room entry is a widely understood risk by corporate physical security departments, the sophistication of combining that access with professional-grade malware deployment is a significant escalation. He believes the perpetrators are likely officers or agents of the Chinese Ministry of State Security, or individuals acting under their direct influence, such as compromised hotel staff.
The Path Toward Hardware-Level Resilience
For many enterprises, the solution to this threat is as much about policy as it is about technology. CrowdStrike has been providing firmware attack detection and BIOS settings auditing via its Falcon sensor for years, yet many organizations fail to fully implement these features for traveling executives.
"It’s a solvable problem," Meyers stated. "It’s just an inconvenient solution."
To prevent similar compromises, security experts recommend a return to rigorous hardware hygiene. Disabling the ability to boot from external media at the UEFI level, protected by a strong BIOS administrator password, is a fundamental defense against USB-based incursions. Furthermore, the use of pre-boot authentication—which requires a user to enter a PIN or provide a hardware key before the encrypted volume can even be read by the operating system—can render a stolen or tampered laptop useless to an attacker.
Yet, despite these available controls, the organizational divide between IT, physical security, and executive travel policy often leads to a dangerous lack of oversight. Often, the team managing cloud-based AI security is completely disconnected from the team responsible for configuring the BIOS settings on a CEO’s travel laptop.
Meyers’ advice for those traveling internationally remains blunt: "Don’t bring anything with you that you’re not comfortable with handing over to a foreign intelligence service." He suggests the use of "burner" laptops and temporary email accounts for overseas travel—devices that contain no production credentials and are wiped clean upon return.
While the industry continues to prioritize the rapid, scalable threats posed by AI-driven eCrime and network-based exploits—which CrowdStrike notes are increasing at a concerning rate—the Hainan incident serves as a crucial reminder that the most persistent threats are often the ones that refuse to scale. A physical incursion into a hotel room cannot be automated like a phishing campaign, but for a nation-state actor, the time and resource investment are a small price to pay for the high-value intelligence that can be extracted from a compromised executive’s machine. As the cybersecurity landscape evolves, the gap between the physical device and the digital cloud remains the most vulnerable point of entry for the world’s most dangerous adversaries.