In a significant blow to the digital asset industry, the cryptocurrency exchange Bitget has confirmed a major security breach that resulted in the exposure of approximately $351.6 million in funds. The incident, which unfolded late Thursday, was officially acknowledged by Bitget CEO Gracy Chen shortly after independent blockchain security researchers and analysts identified a series of highly irregular movements across the exchange’s wallet infrastructure.
The breach has sent shockwaves through the crypto market, serving as a stark reminder of the persistent vulnerabilities inherent in digital asset custody. As the industry grapples with the scale of the loss, the focus has shifted to the exchange’s immediate response, the safety of user deposits, and the broader implications for security protocols in the centralized exchange sector.
A Rapid Response to Unauthorized Transfers
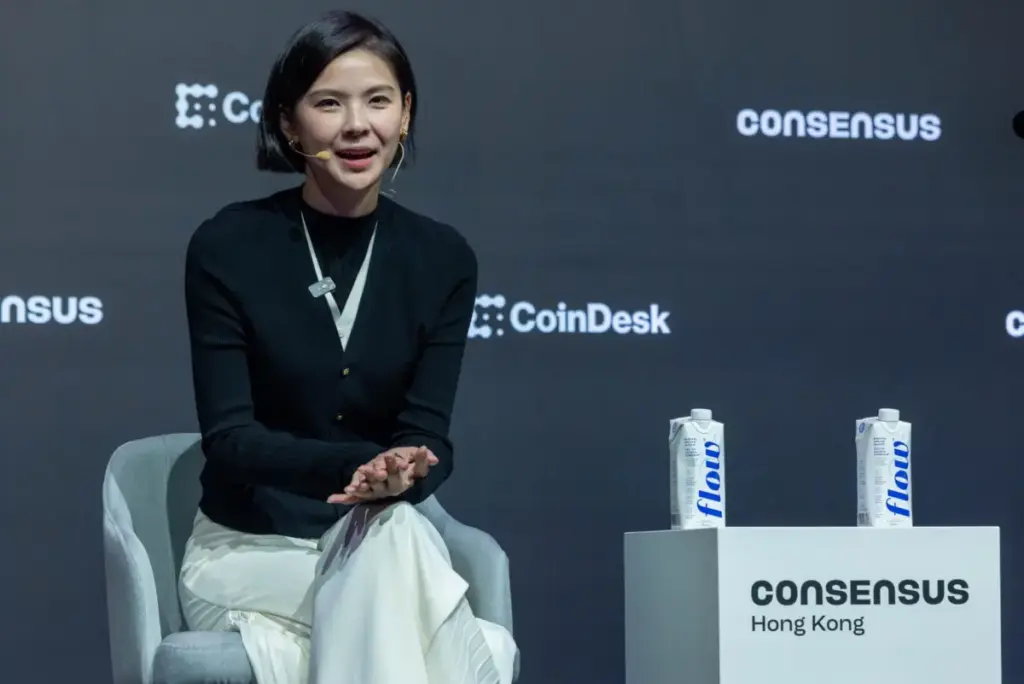
The crisis began to emerge when blockchain monitoring tools detected anomalous activity involving large-scale asset transfers. Shortly thereafter, CEO Gracy Chen took to social media to address the growing speculation, confirming that the exchange had indeed fallen victim to a sophisticated exploit.
According to Chen’s statement on X, the unauthorized activity was confined to a portion of the exchange’s hot and warm wallet layers. Crucially, she emphasized that the company’s cold storage systems—which hold the vast majority of user funds in an offline, air-gapped environment—remained fully secure and uncompromised. This distinction is vital for the exchange’s operational continuity, as it suggests that while the breach was substantial, the fundamental integrity of the platform’s long-term reserves has not been breached.
To mitigate further risk, Bitget has initiated an emergency response protocol, which includes a temporary suspension of withdrawals. The exchange maintains that this measure is a necessary precaution while its security teams conduct an exhaustive audit of their systems. Deposits and trading functions, however, have remained operational, allowing users to continue interacting with the platform while the firm works to isolate the source of the vulnerability.
Insights from On-Chain Analytics
The scale of the incident was first brought to light by the independent research community. Analysts, including Emmett Gallic of Arkham Intelligence, were among the first to trace the suspicious movements on-chain. Gallic’s preliminary findings indicated that the attackers systematically drained funds from at least three Bitget hot wallets and one cold wallet across several distinct blockchains.
The assets siphoned in the attack included a diverse array of major cryptocurrencies, such as Ethereum (ETH), BNB, and Avalanche (AVAX), along with significant holdings of the stablecoin USDT. The attackers appeared to be employing a consolidation strategy, moving the stolen assets into a single destination address, a common tactic used to obscure the trail before attempting to launder funds through decentralized finance (DeFi) protocols or mixing services.
Initial estimates from researchers varied slightly as the situation evolved, with early reports suggesting a loss of roughly $183 million. However, as the scope of the unauthorized transfers became clearer, the figure climbed to the $351.6 million total reported by the company. The speed at which these assets were moved underscores the automated nature of modern crypto heists, where attackers leverage scripts to drain liquidity before human security operators can intervene.
Security Architecture and the "User Protection Fund"
In an attempt to reassure its global user base, Bitget highlighted its multi-tiered security architecture. The exchange utilizes a three-tier system comprising hot, warm, and cold wallets. Hot wallets, which are essential for processing daily transactions and withdrawals, are necessarily connected to the internet, making them the primary target for attackers. Cold wallets, by contrast, are designed to remain disconnected from any internet-facing infrastructure, ensuring that signing credentials remain isolated from potential hackers.
Beyond its technical architecture, Bitget pointed to its "User Protection Fund" as a critical safety net. The fund, which held over $464 million at the time of the announcement, is specifically designed to provide liquidity and compensation in the event of security failures or catastrophic market events. By highlighting the existence of this fund, the exchange is signaling its intent to cover the losses resulting from the breach, though the specifics of how and when affected users might be compensated remain to be seen.
CEO Gracy Chen has promised that a full, transparent incident report will be published within 24 hours. This report is expected to provide a detailed technical breakdown of the exploit, the measures taken to remediate the vulnerability, and a roadmap for resuming normal withdrawal operations. For many observers, the speed and transparency of this report will be a litmus test for the exchange’s future credibility.
A Turbulent Month for Crypto Security
The Bitget breach arrives during what has been a particularly challenging month for the digital asset ecosystem. Earlier in September, the Liquid Network suffered a massive $320 million exploit, an event that drew significant attention due to the hackers’ peculiar claim that they were "white hat" actors acting in the interest of the network. While the circumstances of the Bitget breach appear far more conventional and malicious in nature, the proximity of these two events—totaling over $670 million in losses in less than three weeks—has prompted renewed calls for more rigorous security auditing and the adoption of more advanced custody solutions.
The frequency of these large-scale hacks in 2026 suggests that while the industry has matured in terms of product offerings and regulatory compliance, technical security remains the "Achilles’ heel" of centralized exchanges. The reliance on hot wallets to facilitate high-frequency trading inherently creates a target that, if breached, can lead to losses of this magnitude.
Market Reaction and Financial Impact
The news of the hack had an immediate, albeit somewhat muted, impact on the broader crypto market. Bitget’s native token, BGB, experienced a sharp decline as news of the breach circulated, reflecting investor anxiety regarding the platform’s stability. However, the token showed signs of stabilization shortly after the initial shock, reflecting a degree of confidence that the exchange would be able to weather the storm given its existing protection funds and the security of its cold storage.
Other major assets, including Bitcoin and Ether, saw only marginal volatility, with prices dipping slightly over the 24-hour trading period. This lack of broad contagion suggests that while the Bitget incident is a major event for the exchange itself, the wider market remains relatively resilient. Investors appear to be separating the specific operational failure of one exchange from the overall health of the underlying asset classes.
As the industry waits for the promised incident report, the focus remains on the logistical challenge of recovering stolen assets and the potential for regulatory scrutiny that often follows such large-scale losses. For now, the crypto community is watching closely to see how Bitget manages the fallout of what may well be the largest and most consequential hack of the year. The platform’s ability to successfully navigate this crisis will likely determine its standing in an increasingly competitive and security-conscious market.