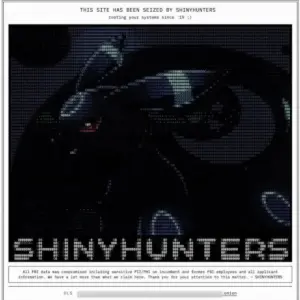
In a significant escalation of the federal crackdown on international cyber extortion syndicates, agents with the Federal Bureau of Investigation (FBI) have arrested a prominent executive from a Canadian cybersecurity firm. The arrest, which took place this past Thursday in Pennsylvania, marks a pivotal turn in the ongoing investigation into the infamous “ShinyHunters” hacking group—a collective that has recently gained notoriety for successfully breaching FBI systems and exfiltrating sensitive data regarding thousands of federal agents.
While the FBI has remained tight-lipped regarding the specific identity of the individual, multiple sources close to the investigation have confirmed to KrebsOnSecurity that the suspect was apprehended while attending the Cyber Risk Summit, an industry conference held at the Loews Philadelphia Hotel between October 5 and October 7. The suspect, identified in federal court records as Edward Dubrovsky, was taken into custody on suspicion of providing assistance to the ShinyHunters group, an organization currently under the intense scrutiny of federal authorities.
The arrest was first signaled by reports from The New York Times and a brief confirmation issued by FBI Director Kash Patel via social media. Despite the high-profile nature of the case, the specific charges and the nature of the suspect’s alleged involvement remain partially shielded by the judicial system, as several court documents have been placed under seal. However, public records indicate that Dubrovsky faces serious counts of conspiracy to threaten to impair the confidentiality of information with the intent to extort money, as well as charges of interference with commerce by threats.
A Conflict of Interest in the Ransomware Ecosystem
The intersection of the suspect’s professional background and the criminal charges he now faces has sent shockwaves through the cybersecurity industry. According to investigators and industry sources, the suspect’s firm specialized in high-stakes ransomware negotiations—a delicate field that sits at the blurred edge between legitimate risk mitigation and the complex dynamics of criminal extortion.
Conference materials from the Cyber Risk Summit reveal that the event’s primary sponsor was the Canadian security firm Cypfer. While online discourse initially linked the arrested executive to a founding role at Cypfer, a company spokesperson later issued a clarification, stating that the individual had served as a managing director before resigning in November 2025. Following his departure from Cypfer, the subject became associated with another firm, CyberSteward, which was also a sponsor of the Philadelphia summit.
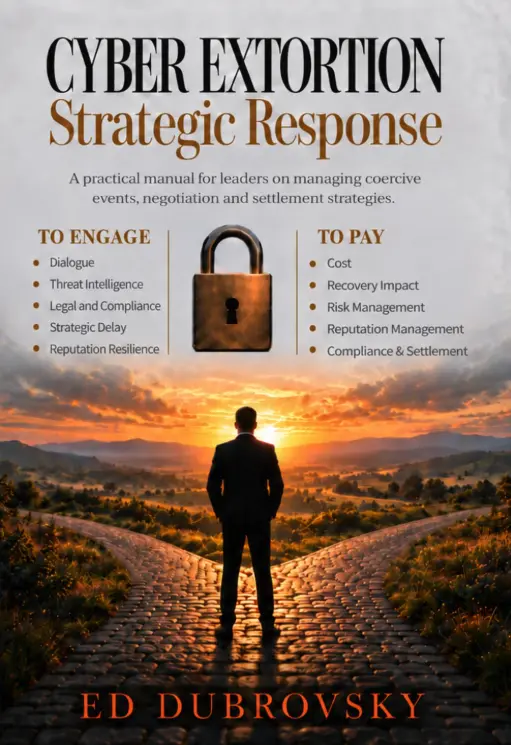
The suspect’s public profile suggests a deep, theoretical, and practical immersion in the world of cyber extortion. He is the author of Cyber Extortion Strategic Response, a 252-page professional volume that promises to guide organizations through the harrowing process of dealing with ransom demands. In the book, he argues for a nuanced approach to communication with threat actors, famously noting that "communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay." He further posits that engagement can serve tactical objectives, such as gathering intelligence, verifying the validity of stolen data, and stalling for time.

This professional philosophy—once marketed as a sophisticated tool for corporate survival—is now under the microscope of federal prosecutors, who are investigating whether the lines between "negotiation" and "facilitation" were crossed.
The Epicenter of the ShinyHunters Probe
The investigation into the ShinyHunters group has grown increasingly complex, with control of the operation now centralized at an FBI field office in Texas. Court records filed on October 9 indicate that the case against the Canadian executive has been moved to the Eastern District of Texas, confirming reports that the region has become the primary hub for the bureau’s efforts to dismantle the group.
The ShinyHunters collective has proven to be a particularly elusive and aggressive adversary. By utilizing sophisticated phishing campaigns and stolen credentials to siphon data from software-as-a-service (SaaS) providers, the group has successfully extorted more than $70 million from victims throughout the current calendar year. Their tactics often involve threatening to release sensitive data on the public web unless their exorbitant ransom demands are met.
The recent series of arrests suggests that the FBI is gaining ground by aggressively following the digital and human trails left behind by the hackers. Sources tell KrebsOnSecurity that investigators have been meticulously poring over devices seized last month during the arrest of Pepijn van der Stap, a convicted cybercriminal apprehended by Dutch police. The intelligence gleaned from these devices is reportedly providing the FBI with a roadmap of the group’s internal hierarchy and external facilitators.
The Evolution of the ShinyHunters Threat
The resilience of the ShinyHunters group has been tested by these recent law enforcement actions. Following the arrest of Van der Stap, a member of the group operating under the pseudonym “Rey” assumed leadership. Rey quickly became a thorn in the side of the FBI, taunting the agency by leaking data stolen from the bureau’s own online recruitment portal. This breach was particularly damaging, as it contained sensitive details regarding the units and specializations of federal agents, as well as personal medical and psychiatric records.
However, the group’s momentum appears to be faltering. Last week, Reuters reported that the individual known as Rey—identified as a teenager named Saif Al-din Khader—had been detained and was actively cooperating with FBI investigators. The apprehension of Khader was reportedly tied to the group’s attempts to extort a navigation and digital aviation unit previously divested by Boeing in late 2025.

The capture of Khader and the subsequent arrest of the Canadian executive in Philadelphia suggest a broader strategy by the FBI: to systematically remove both the technical operators and the alleged professional facilitators who help the group extract value from their criminal enterprises.
As of the latest updates, Edward Dubrovsky remains in federal custody at a facility in Philadelphia, pending his transfer to the Eastern District of Texas. Court records indicate that he does not currently have legal representation and has yet to be assigned a public defender. The silence from the FBI regarding the specifics of the evidence against him highlights the sensitivity of the ongoing investigation.
For the cybersecurity community, the case serves as a stark reminder of the risks inherent in the ransomware negotiation industry. As federal authorities continue to map the networks supporting groups like ShinyHunters, industry experts anticipate that additional charges against other principals at security firms specializing in ransom settlements may be forthcoming.
With the investigation moving rapidly and new details emerging from the courts, the case of the arrested Canadian executive remains the focal point of a larger, high-stakes battle between federal law enforcement and the sophisticated criminal syndicates that hold corporate and government entities hostage. For now, the legal proceedings against the accused, and the ongoing forensic analysis of the seized devices, promise to provide a much clearer picture of how the ShinyHunters operated—and exactly who was helping them along the way.