In a significant development in the high-stakes battle against international cybercrime, federal agents have apprehended a prominent executive from a Canadian cybersecurity firm. The arrest, which took place this past Thursday in Pennsylvania, is directly tied to an expansive investigation into the notorious hacking collective known as "ShinyHunters." This group has recently made headlines for allegedly compromising the Federal Bureau of Investigation, siphoning sensitive data belonging to thousands of agency personnel.
Multiple sources familiar with the matter confirmed the arrest to KrebsOnSecurity. The operation, which follows a series of tactical strikes against the group, underscores the FBI’s determination to dismantle a criminal enterprise that has wreaked havoc on corporate and government entities alike. While official sources have been tight-lipped regarding the specific identity of the detainee, The New York Times reported that the FBI successfully took a Canadian national into custody on suspicion of providing material assistance to the ShinyHunters operation.
FBI Director Kash Patel acknowledged the arrest via a brief statement on X (formerly Twitter), though he stopped short of identifying the individual by name. The timing and location of the arrest appear to be linked to a professional gathering; sources close to the investigation indicated that the suspect was in Pennsylvania to attend the Cyber Risk Summit, an industry event held between October 5 and October 7 at the Loews Philadelphia Hotel.
The individual arrested has been identified in court records as Edward Dobrovsky. While the filings contain a minor orthographic discrepancy in the surname, the details align with the professional background of Edward Dubrovsky, an industry figure well-known for his expertise in ransomware negotiations. According to public records and summit materials, the conference boasted several high-profile sponsors, with the Canadian security firm Cypfer listed as the primary backer.
The professional trajectory of the suspect has come under intense scrutiny in the wake of the arrest. LinkedIn records previously identified Dubrovsky as a founder or co-founder of Cypfer. However, in an effort to clarify his standing, a spokesperson for Cypfer issued an update on October 10, stating that Dubrovsky was never a founder of the firm, but rather served as a managing director before his resignation in November 2025. Currently, Dubrovsky is associated with another Canadian security entity and summit sponsor, CyberSteward. In a LinkedIn post published roughly one month prior to his arrest, Dubrovsky had publicly expressed his intent to attend the Philadelphia summit alongside his colleagues from CyberSteward.

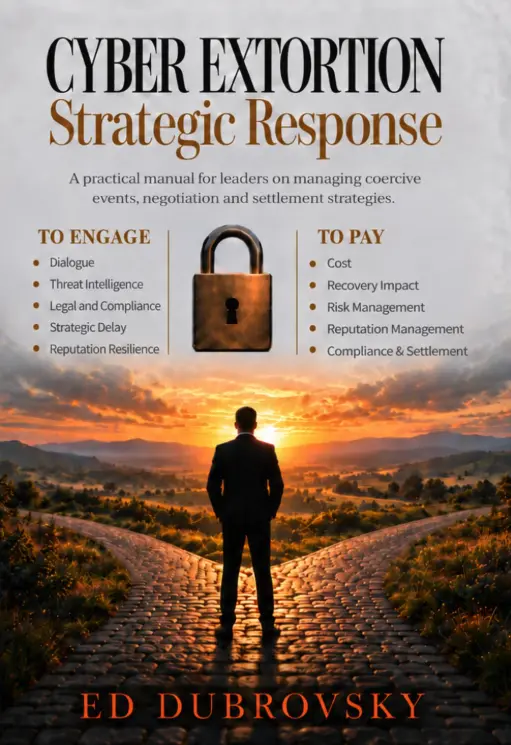
His professional focus has centered heavily on the gray area of cyber-extortion. In his LinkedIn bio, he stated: "Looking forward to continuing conversations around strategy & compliant driven coercive (ransomware, extortion) advisory, negotiations and settlement services that are global and truly agnostic." He is also the author of a 252-page book titled Cyber Extortion Strategic Response, which purports to guide organizations through the complex, often harrowing process of responding to ransom demands.
The book’s promotional material offers a window into the philosophy of the author: "At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay. Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."
Federal court records filed on October 8 confirm that an individual by the name of Edward Dobrovsky was arrested in Pennsylvania on charges of cyber extortion and conspiracy. Although a significant portion of the core complaint remains under seal, documents indexed by CourtListener indicate that the defendant faces charges of "conspiracy to threaten to impair the confidentiality of information with the intent to extort money," and "interference with commerce by threats."
As of the latest reports, the U.S. Bureau of Prisons inmate locator places a 54-year-old Edward Dubrovsky at a federal facility in Philadelphia. However, the legal proceedings appear to be shifting toward Texas. A notice filed on October 9 indicates that the case has been moved to the Eastern District of Texas. Sources familiar with the FBI’s broader strategy suggest that the Texas field office has become the centralized hub for the entire ShinyHunters investigation. The FBI has declined to provide further comment on the specific charges or the transfer of the case. Currently, court records show that the defendant has not yet secured legal counsel, and no public defender has been appointed.
The ShinyHunters group has maintained a persistent and aggressive profile in the cyber-threat landscape. Their typical methodology involves the exploitation of phishing campaigns and the acquisition of stolen credentials to breach corporate accounts, particularly those associated with software-as-a-service (SaaS) providers. Once inside, the group exfiltrates massive volumes of data, leveraging the threat of public disclosure to extort victims. According to FBI estimates, the collective has successfully extorted more than $70 million from various organizations within the current calendar year alone.

The investigation into the group has been gaining momentum since last month, when Dutch law enforcement apprehended Pepijn van der Stap, a previously convicted cybercriminal suspected of playing a key role in the ShinyHunters operation. Sources indicate that the FBI has been meticulously examining electronic devices seized during that arrest, a move that is expected to yield further leads. There is widespread speculation that additional charges may soon be leveled against principals at other firms that specialize in the niche, high-stakes business of ransomware negotiation.
The pressure on the ShinyHunters collective intensified after the arrest of Van der Stap. In a display of brazen defiance, another member of the group, operating under the alias "Rey," assumed a leadership role and began taunting the FBI. The group escalated their attacks, specifically targeting the FBI’s own recruitment portal. The stolen data reportedly included sensitive details regarding the units and specializations of agency personnel, alongside private medical and psychiatric records.
Last week, international reporting from Reuters revealed that the individual behind the "Rey" alias—identified as a teenager named Saif Al-din Khader—had been detained and was cooperating with federal authorities. Investigations revealed that Khader was apprehended as the group was in the midst of an extortion attempt against a navigation and digital aviation unit, which had been divested from Boeing late in 2025.
The arrest of a cybersecurity executive, particularly one who specialized in the very tactics used by the hackers he is now accused of assisting, marks a disturbing intersection between the legitimate security industry and the criminal underground. As federal authorities continue to peel back the layers of the ShinyHunters network, the case remains a fast-moving and critical priority for the Department of Justice and the FBI, with further developments expected as investigators process the seized evidence and continue their interrogation of those in custody.