In a significant victory for cybersecurity and consumer protection, Google announced today that it has successfully coordinated with industry partners to dismantle a sprawling botnet consisting of more than 1.3 million compromised Android TV set-top boxes. These devices, which ship with malicious software pre-installed, have been secretly harvesting the internet bandwidth of unsuspecting users to facilitate advertising fraud and power residential proxy services for anonymous traffic resale.
Experts involved in the takedown operation warn that the scope of the threat extends far beyond the primary 1.3 million TV boxes. The action is expected to sever the botnet’s reach into an estimated 10 million additional compromised systems, including a wide variety of Internet of Things (IoT) products such as Android-based healthcare devices, digital signage systems, and karaoke machines, all of which were susceptible to the same underlying malware infrastructure.
The Role of Videostrong Technology Co.
The disruption effort was spearheaded by the Google Threat Intelligence Group (GTIG), which released a comprehensive report detailing the firm’s decision to sever all ties with Videostrong Technology Co., a China-based manufacturer of TV streaming hardware. According to GTIG, investigators concluded that Videostrong was responsible for embedding the malicious code—dubbed “XCPE” after a core component of the malware—directly into the firmware of their devices.
The XCPE botnet functioned by loading the infected device with software that effectively turned the user’s home internet connection into a node for commercial residential proxy services. These services allow external customers to rent IP addresses to anonymize their web traffic or spoof their geographical location. While these tools have legitimate uses, they are frequently exploited by malicious actors to carry out account takeovers, large-scale advertising fraud, and the mass scraping of data for artificial intelligence training projects.
In its official report, GTIG did not mince words regarding the severity of the breach. “Videostrong monetized the backdoor by selling access to criminal affiliates and loading those affiliates’ malware modules onto infected devices,” the group stated. Google confirmed that it took decisive legal action to seize the domains and servers that Videostrong used to maintain command-and-control over the botnet and to push additional malicious payloads onto devices.
“A device manufacturer intentionally infecting their users with malware is an unacceptable breach of trust and represents a serious risk to those users,” Google noted in its announcement. “Without users’ knowledge or consent, infected devices were offered as a distribution mechanism for a wide array of criminal actors.”
The Ecosystem of Malicious Proxies
The GTIG investigation highlighted a troubling ecosystem where residential proxy providers relied on software development kits (SDKs) that were routinely bundled into the XCPE malware. Among the companies named in the report are several well-known players in the proxy industry.

One such firm is AppSalt, also known as Honeygain, which was developed by the Vilnius-based company Oxylabs. In October 2026, Oxylabs and Honeygain were reorganized under a new umbrella entity called Source, which recently secured $130 million in funding from the private equity firm Warburg Pincus, reaching a valuation of $3.6 billion.
Another provider identified in the report is NetNut, a residential proxy company operated by the publicly traded Israeli firm Alarum Technologies. This is not the first time NetNut has faced scrutiny; in July 2026, the FBI and its partners seized hundreds of domains associated with the company, alleging that it operated a separate botnet known as “Popa” that similarly enslaved Android TV boxes to serve as residential proxies. The GTIG report also implicated several other proxy providers, including EarnFM, Traffmonetizer, Jaguar, LINKFOG, BMW/IPWeb, and GaGaNode, as part of the broader infrastructure that capitalized on the compromised devices.
Industry Collaboration and the "Badbox" Phenomenon
The successful takedown was the result of a concerted effort by several industry players, including the startup Synthient, which specializes in tracking proxy networks. Earlier this year, Synthient gained prominence for its research into the “Kimwolf” botnet, which had been terrorizing networks globally with massive Distributed Denial of Service (DDoS) attacks. Synthient’s research revealed how Kimwolf was able to compromise millions of set-top boxes almost overnight by exploiting vulnerabilities in residential proxy SDKs, allowing the malware to spread laterally to other IoT devices on the same local network.
This research triggered a chain reaction: many proxy providers were forced to patch their networks, which fragmented the Kimwolf botnet and made it easier for internet service providers to mitigate the disruption. The issue also captured the attention of the Motion Picture Association (MPA), which collaborated with Synthient to physically dismantle and analyze various Android TV boxes.
In a report released today, Synthient highlighted that the malware found in Videostrong devices was not an isolated incident. The researchers examined the “MECOOL” brand of streaming boxes, manufactured by the Chinese company Skyworth Technology, and found that they also bundled the XCPE malware and proxy components, including those from Honeygain.
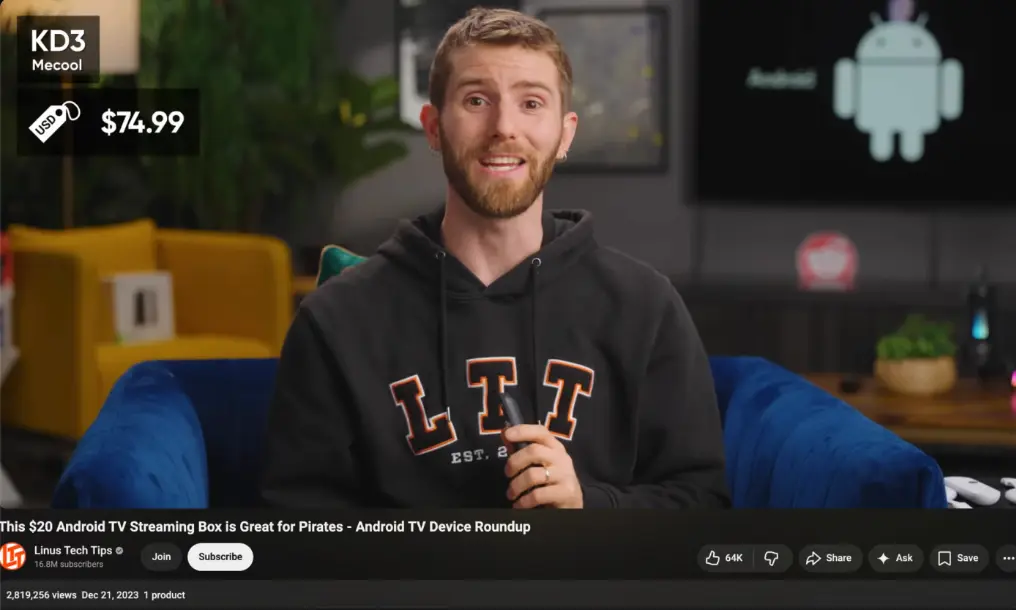
The growth of these botnets has been fueled by the popularity of "pirate" streaming boxes, which are frequently marketed by influencers on platforms like TikTok and YouTube. These devices promise access to hundreds of premium, copyrighted streaming services for a single one-time fee. The MECOOL devices, for instance, saw a massive surge in sales following a 2023 endorsement from the popular YouTube channel Linus Tech Tips. Following the revelations, the channel updated its video to label the product a scam and removed all associated affiliate links.
The Scale of the Threat
While Google has addressed the specific vulnerability that allowed Videostrong to install malware during the initial device boot-up, the sheer scale of the infection remains a major concern for the tech industry. Ben Brundage, the founder of Synthient, characterized the estimate of 1.3 million devices as “highly conservative,” noting that the proxy and ad-fraud affiliates involved have likely utilized multiple distribution channels beyond just the XCPE malware.

“The scale of affected devices is likely way higher,” Brundage said. “This is probably the largest operation against backdoored TV boxes that we’ve seen.”
In response to the report, Oxylabs issued a statement following publication, clarifying that their systems are intended to function only with user consent. The company claimed that the developer behind the infected apps had effectively faked the consent signals.
“We have been conducting regular audits of the applications provided by our partners,” the company said. “However, following this incident, we will improve the application and application’s build fingerprinting logic to better detect cases where the SDK is running on an unapproved build of an originally authorized application.”
Oxylabs further stated that it had no record of a relationship with Videostrong Technology Co. but identified a domain mentioned in the GTIG report as an external malware loader. “As soon as we saw that, we suspended the relationship and sent them a formal legal inquiry,” the statement read. “This supplier accounts for less than 1% of our IP address pool. We had a signed contract with them, they assured our QA team that users had given consent, and we saw the consent flow ourselves.”
As the investigation continues, security experts and manufacturers remain on high alert. The incident serves as a stark reminder of the security risks inherent in low-cost, unverified IoT hardware, where the promise of “free” content often hides a far more insidious cost to the consumer’s digital security and personal privacy. For users of these devices, the best course of action remains ensuring that firmware is kept up to date and, where possible, replacing devices from non-reputable manufacturers with those from vendors that adhere to strict security and privacy standards.