Dutch authorities have apprehended a 24-year-old convicted cybercriminal on suspicion of facilitating data theft and extortion for the notorious hacker collective known as ShinyHunters. The arrest of the suspect, identified by sources as Pepijn van der Stap, a resident of Almere and Lelystad, comes amid a period of intense volatility for the hacker group, which has dramatically escalated its global operations in the immediate aftermath of the police action.
The arrest has sent shockwaves through the cybersecurity landscape, as the remaining members of ShinyHunters have responded with a series of brazen, high-stakes attacks. These include the compromise of sensitive data from the Federal Bureau of Investigation (FBI) and the bold extortion of the Russian-linked ransomware group Cl0p.
A Double Life: From Researcher to "Umbreon"
Van der Stap is a figure of complex contradictions. In 2023, he was convicted in the Netherlands for his role in a sophisticated string of data thefts and extortion campaigns that netted between €1.5 million and €2.7 million. During his trial, he famously characterized his life as a "Dr. Jekyll and Mr. Hyde" existence. By day, he maintained a respectable professional presence as a software engineer at Hadrian, an Amsterdam-based cybersecurity startup, while also volunteering his time at the Dutch Institute for Vulnerability Disclosure (DIVD), a nonprofit organization dedicated to security research.
Under the cover of night, however, Van der Stap operated under the handle "Umbreon." Using this alias, he frequented English-language cybercrime forums such as the now-defunct RaidForums and Breached, where he sold stolen databases and extorted victims. His digital persona, named after a character from the Pokémon franchise, became a recognizable mark in underground circles, particularly after he offered data on 2.3 million Dutch citizens for sale in 2021.
Following his confession, Van der Stap was sentenced to four years in prison, with one year suspended. During the legal proceedings, he opted to remain in custody rather than return to his home, citing the need for treatment regarding psychological issues, including post-traumatic stress related to childhood trauma. He was ultimately released in December 2025.

In an interview with KrebsOnSecurity on September 9, 2026, Van der Stap sought to portray himself as a man attempting to make amends. At the time, he was employed as an offensive security lead at the Dutch firm Neo Security. He spoke of the ongoing civil litigation and restitution requirements stemming from his past crimes, claiming he was fully committed to contributing positively to society. However, shortly after that conversation, Van der Stap ceased all communication, effectively dropping off the grid for two weeks before his arrest on or around September 16.
The Odido Hack and Escalating Tensions
The arrest follows a months-long investigation by Dutch police into a high-profile intrusion at Odido, the Netherlands’ largest mobile telecommunications provider. In February 2026, a Dutch-speaking member of ShinyHunters successfully employed social engineering tactics to deceive an Odido employee into logging into a spoofed website. This breach allowed the attackers to exfiltrate the personal data of over 6.2 million Dutch citizens.
Dutch law enforcement had been actively soliciting public assistance to identify the voice of the hacker in a recorded phone call related to the Odido incident. In a brazen response to the investigation, ShinyHunters confirmed that the individual in the audio clip was indeed a member of their collective. The group issued a defiant statement to the NL Times, asserting that they were providing their comrade with full emotional, mental, and financial support, including legal counsel. They further insulted the competence of Dutch authorities, claiming that the police were "incompetent" and "irrelevant," and threatening further large-scale attacks on the nation.
Global Breach: The FBI and Oracle PeopleSoft
The group’s rhetoric was soon followed by action. Days after reports emerged of Van der Stap’s detention, ShinyHunters claimed responsibility for a significant breach of the FBI’s job application portal, apply.fbijobs.gov. According to reports from 404 Media and Reuters, the stolen data included Social Security numbers and personal details of more than 5,000 FBI employees. The cache contained highly sensitive information, including job titles, team assignments—such as those involving cyber threat intelligence and major cybercrime units—and even personal psychiatric and medical records.
The FBI has since confirmed the compromise of the portal. Analysts have linked the breach to the exploitation of a critical vulnerability (CVE-2026-35273) in Oracle’s PeopleSoft, a widely used human resources and payroll platform. While Oracle released a patch for the flaw, ShinyHunters reportedly bypassed mitigation efforts, including web application firewall rules suggested by Mandiant, by utilizing a URL-encoding trick. Security researchers at Mandiant and the Google Threat Intelligence Group (GTIG) confirmed in a September 25 report that ShinyHunters had conducted mass exploitation of this vulnerability across various sectors, including healthcare, technology, and government.

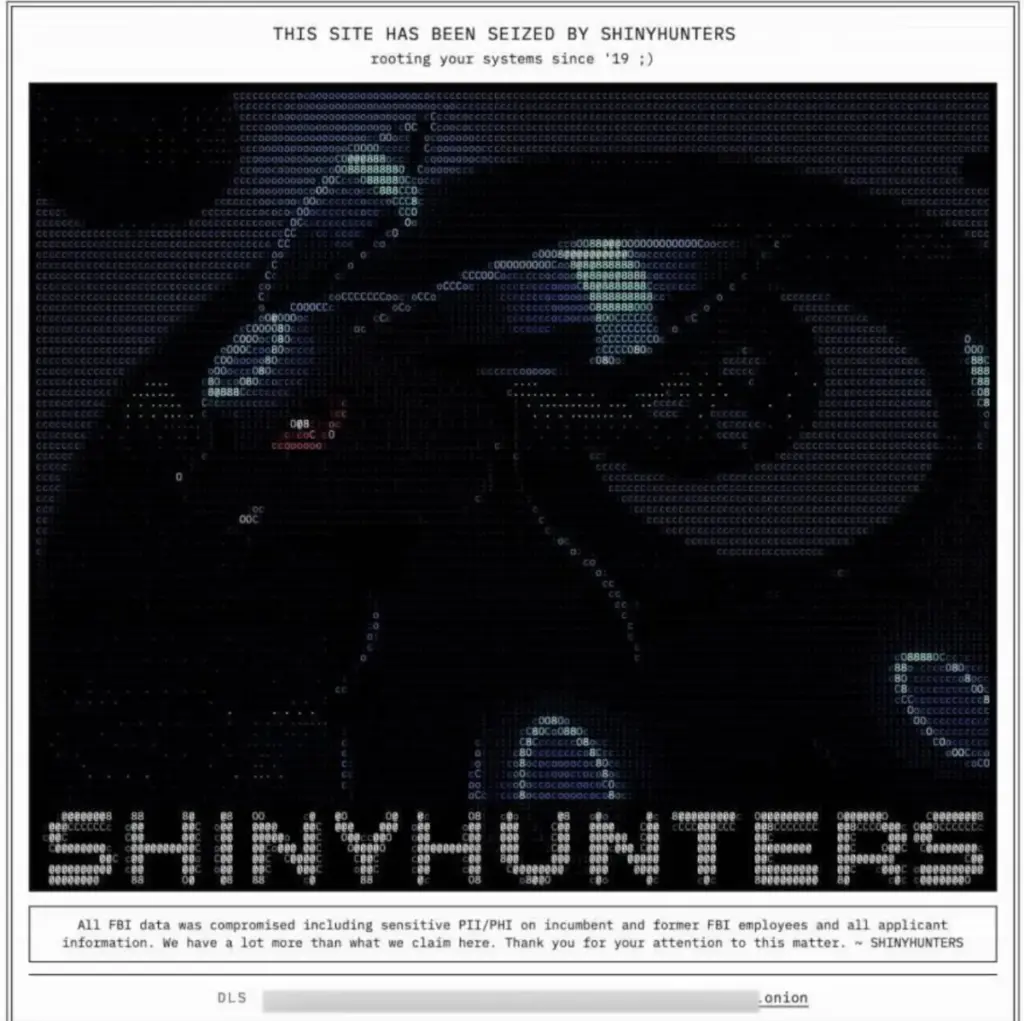
Throughout these attacks, the "Umbreon" alias—the same handle used by Van der Stap—reappeared in the group’s defacement messages. On the compromised FBI site, the hackers left an ASCII art depiction of the Pokémon character Umbreon, accompanied by the message: "This site has been seized by ShinyHunters. rooting your systems since ’19 ;)." This specific imagery appears to be an attempt by rival factions within the cybercrime underground to associate the Dutchman with the recent surge in high-profile attacks.
Internal Power Struggles and the Rise of "Rey"
Sources close to the investigation suggest that the recent pivot toward more reckless, high-visibility attacks marks a fundamental change in the leadership of ShinyHunters. The group is now reportedly under the influence of a teenage cybercriminal based in Amman, Jordan, known as "Rey." Rey is a key figure in the collective ScatteredLapsussHunters (SLSH), an umbrella group that synthesizes the capabilities of Scattered Spider, LAPSUS$, and ShinyHunters.
Investigations suggest there is significant animosity between Rey and Van der Stap regarding the control of the ShinyHunters brand and the proceeds of their data thefts. The inclusion of the Umbreon character in recent defacement images is viewed by security experts as a calculated move by Rey to implicate Van der Stap in the latest operations.
Rey has previously been identified by the cybersecurity firm KELA, and reports indicate that he operates with a level of aggression that has alienated some of his collaborators. His father, an employee of Royal Jordanian Airlines, has been contacted multiple times regarding his son’s activities but has provided no comment.
A Criminal Legacy and New Charges
Van der Stap’s motivations have long been a subject of scrutiny. Unlike many cybercriminals driven solely by financial gain, Van der Stap previously described his activities as a compulsive need to collect, organize, and archive data. "The hacking was very easy for me, and it wasn’t a compulsion," he told Bloomberg in 2024. "My habit was collecting. Collecting data, organizing data, downloading data, creating folders."

As the legal proceedings against him continue, the scope of the allegations has broadened significantly. On September 29, the Dutch news outlet RTL reported that investigators suspect Van der Stap of orchestrating at least two murders. Prosecutors allege that these crimes were intended to be carried out abroad, and they possess evidence suggesting the suspect issued the orders.
The FBI, represented by Assistant Director of the Cyber Division Brett Leatherman, has publicly thanked Dutch law enforcement for their cooperation. In a video message, Leatherman urged remaining members of the group to surrender, warning that the agency’s knowledge of their operations is growing. "Arrests have a way of changing who is willing to talk, and seized infrastructure has a way of showing us who’s left," Leatherman stated. "The longer you stay in this, the more we learn about you. You know how to find us, and we know how to find you."
The Dutch police confirmed that Van der Stap is scheduled to appear before the Rotterdam District Court to face the mounting charges against him, marking a definitive, if chaotic, turn in the investigation into one of the world’s most active data extortion rings.