In a striking reminder that the most advanced digital defenses can be circumvented by old-fashioned physical intrusion, a state-linked Chinese hacking group successfully compromised the laptops of senior executives attending an agricultural industry conference on Hainan Island earlier this spring. The operation, which bypassed traditional cybersecurity measures like multi-factor authentication (MFA) and endpoint detection and response (EDR) software, relied on a method security researchers have long dubbed the “evil maid” attack: gaining physical access to unattended hardware to implant malware directly into the system.
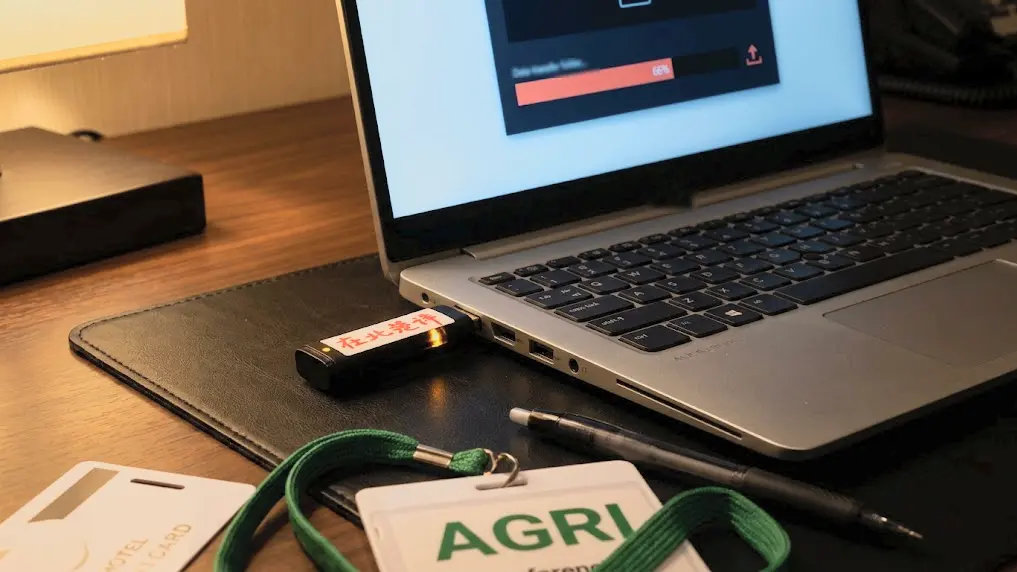
According to CrowdStrike’s 2026 Threat Hunting Report, the group, which the firm tracks as OVERCAST PANDA, executed this operation not through phishing emails or network breaches, but by infiltrating hotel rooms while the occupants were away at dinner. Adam Meyers, CrowdStrike’s senior vice president of counter adversary operations, detailed the timeline of the intrusions during the company’s Fal.Con 2026 conference. The intruders managed to enter one hotel room at approximately 8 p.m. local time and a second room by 9:57 p.m. Once inside, they booted the target laptops from a malicious USB stick, writing a backdoor known as FlowCloud directly to the machines’ storage before rebooting and leaving the rooms undisturbed.
The simplicity of the attack is matched only by its effectiveness. By bypassing the operating system entirely during the initial compromise, the hackers rendered network-based security controls irrelevant. There was no phishing attempt to trigger a user error, no credential-harvesting site to capture login data, and no network traffic for firewalls to flag. When the executives returned to their rooms and eventually powered on their laptops the following morning, the malicious trigger fired, allowing FlowCloud to load silently. Once active, the malware began its work: logging keystrokes, capturing screen activity, harvesting credentials, and exfiltrating sensitive files.
The Evolution of a Known Threat
While the “evil maid” concept—named after the theoretical risk of a hotel employee gaining access to a guest’s computer—has been a staple of security discourse since Joanna Rutkowska demonstrated it with a bootable USB stick in 2009, its use by state-sponsored actors remains relatively rare among the 290 adversaries tracked by CrowdStrike.
The OVERCAST PANDA campaign distinguishes itself through the seamless integration of high-level tradecraft. While other groups, such as the China-based MUSTANG PANDA, have historically relied on dropping USB sticks in hopes that a target will plug them in, OVERCAST PANDA’s approach is far more proactive. By utilizing hotel room access, they ensure the malware is placed directly on the specific hardware of their high-value targets.
FlowCloud itself is not a new tool, but its deployment here demonstrates the persistence of legacy threats. Proofpoint first documented the backdoor in 2020, noting its use in phishing campaigns targeting U.S. utility companies. NTT Security has also tracked USB-delivered infections using similar malware at overseas branches of Japanese organizations since early 2022. However, Meyers noted that the novel aspect of this specific campaign is the convergence of traditional intelligence-gathering tradecraft—breaking into secure hotel rooms—with sophisticated malware deployment.
The operation also raises significant concerns about the attribution of these attacks. Meyers identified the Ministry of State Security (MSS) in China as the likely force behind OVERCAST PANDA. The physical act of entering the rooms, he suggested, was likely performed by officers of the MSS or the Ministry of Public Security, or potentially by hotel staff who had been compelled or bribed by the state to facilitate the breach. Targeting an agricultural conference may seem niche, but it aligns perfectly with China’s stated long-term economic and food-security objectives, often outlined in its official five-year plans. A similar operation targeting a U.S.-based media professional, discovered mid-2026, further confirms the group’s reliance on this specific, high-touch methodology.
Why Modern Security Tools Often Miss Physical Tampering
The fundamental challenge posed by this campaign lies in the “blind spot” between a device being powered off and the operating system loading. Modern EDR agents, like CrowdStrike’s Falcon, require the operating system to be active to perform their duties. Similarly, MFA and AI-driven identity protections are designed to secure active user sessions or cloud workloads.
OVERCAST PANDA effectively operated below the stack. The compromise occurred when the device was essentially a piece of inert hardware, leaving no trace for an OS-level security agent to detect until the machine was already compromised. CrowdStrike’s sensor eventually caught the FlowCloud process once the OS loaded and the malware attempted to execute, but the damage was already done: the implant was on the disk, and the machine’s security had been fundamentally violated.
"Hotel entry is a very common thing," Meyers told VentureBeat. "Talk to any corporate physical security person. They’re generally aware of hotel entry, but I think what is unique is the combination of hotel entry with deployment of malware."
This gap highlights a broader issue in corporate security posture: the compartmentalization of defense. While firms invest heavily in cloud security, AI-powered threat detection, and advanced endpoint monitoring, the physical security of hardware remains a responsibility that often falls under a different organizational umbrella, or is ignored entirely.
The Shift Toward AI and Runtime Security
CrowdStrike’s disclosure of the OVERCAST PANDA campaign comes at a critical juncture for the cybersecurity industry. During Fal.Con 2026, the company announced a massive expansion of its AI security product slate, including the introduction of SafeMind—an agentic cybersecurity system built in partnership with Nvidia using Nemotron open models—and Falcon Guardian, a runtime security layer for AI agents.
These tools are designed to address a rapidly evolving threat landscape where AI-powered intrusions are scaling at an alarming rate. According to the company’s threat data, AI agent-triggered detections grew at 2.5 times the rate of human-triggered leads in the first half of 2026. Furthermore, cloud-conscious eCrime activity surged by 171%, and vishing (voice phishing) intrusions have doubled. Yet, all of these advanced threats share one common assumption: they target a running operating system, an active user, or a live cloud workload.
As Meyers observed, the industry is increasingly focused on these scalable, network-based threats because they affect the greatest number of machines. "You can’t intrude on hotel rooms at scale," Meyers said. "You can’t intrude on physical devices at scale. And even then, it’s just one device." However, for the executive whose laptop is compromised in a hotel room, the lack of scale does not make the intrusion any less devastating.
Closing the Physical Gap
The countermeasures required to prevent an “evil maid” attack are well-established, though often overlooked due to the inconvenience they impose on the end user. According to CrowdStrike, the solutions are rooted in firmware and policy rather than new software products.
Disabling the ability to boot from external media in the UEFI settings is perhaps the most effective deterrent. When paired with a strong BIOS administrator password, this prevents an unauthorized party from booting a machine from a USB drive. Furthermore, pre-boot authentication—which requires a user to enter a PIN or insert a hardware key before the encrypted drive can even be read by the OS—ensures that even if an attacker manages to boot the machine, they cannot access the file system to install a backdoor.
Meyers also advocates for a “travel-light” policy. Executives should be issued specific, hardened devices for international travel that contain no access to sensitive internal networks, no saved credentials, and no persistent VPN configurations. Once the trip concludes, these devices should be wiped or physically decommissioned.
"Don’t bring anything with you that you’re not comfortable with handing over to a foreign intelligence service," Meyers advised. He noted that even without an “evil maid” attack, government officials at border crossings can legally compel a traveler to unlock their device, rendering traditional encryption moot.
As the security industry pivots toward complex AI-driven defense mechanisms, the OVERCAST PANDA campaign serves as a sobering reminder that the oldest, most manual forms of espionage are still in active use. Organizations must recognize that while AI will defend the network, the security of the individual laptop remains a physical responsibility that cannot be offloaded to software alone. For the modern enterprise, closing the security gap requires bridging the divide between IT policy, firmware management, and a realistic understanding of the risks inherent in global travel.