







In a stark reminder of the persistent risks associated with international business travel, a Chinese state-linked hacking group has been identified orchestrating a sophisticated espionage campaign that bypasses digital security entirely. Rather than relying on traditional phishing emails, malware-laden links, or network-level intrusions, the threat actors—tracked by security firm CrowdStrike as OVERCAST PANDA—gained access to executive laptops by physically entering hotel rooms on Hainan Island this past spring.
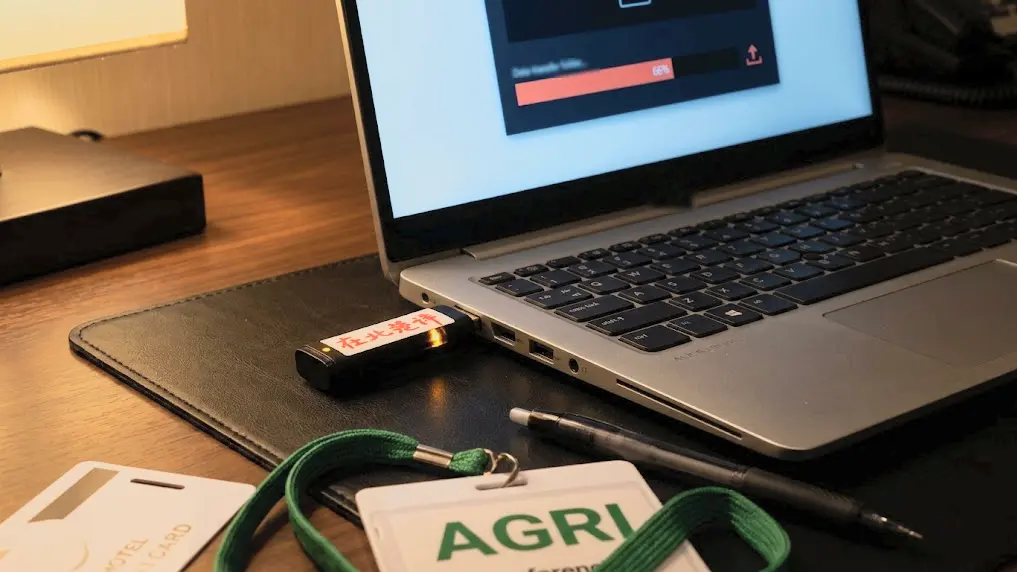
The operation, which targeted high-level executives attending an agricultural industry conference, saw intruders entering private suites while the occupants were away for dinner. Once inside, the operators used bootable USB sticks to compromise the machines directly, installing a persistent backdoor known as FlowCloud. This method allowed the attackers to manipulate the laptops at the hardware level, avoiding the detection mechanisms that typically guard against remote cyberattacks.
The Mechanics of the "Evil Maid" Attack
The details of the campaign were unveiled in CrowdStrike’s 2026 Threat Hunting Report and further elaborated upon by Adam Meyers, the company’s senior vice president of counter adversary operations, during the Fal.Con 2026 conference in Las Vegas. According to the investigation, the intrusions were highly surgical and timed with precision. In one instance, an intruder gained entry to a room at approximately 8 p.m. local time, followed by a second breach at 9:57 p.m. The attackers did not attempt to bypass login credentials or steal passwords through fake portals; instead, they booted the machines from external media, wrote the FlowCloud backdoor directly into the system’s storage, and exited, leaving the laptops seemingly untouched.
Security researchers have long referred to this technique as an "evil maid attack," a term coined in 2009 after Joanna Rutkowska demonstrated how physical access to an unattended machine could render even the most secure software defenses moot. While physical-access operations remain a rarity compared to the thousands of network-based threats CrowdStrike monitors, the OVERCAST PANDA campaign represents a novel escalation. By combining the tradecraft of intelligence-grade hotel room access with the deployment of advanced, persistent malware, the group effectively moved the battleground from the network to the physical environment.
When the targeted executives returned to their rooms and powered on their devices the following morning, the malicious trigger fired, and FlowCloud loaded into memory. From that point forward, the compromised laptops began executing a range of espionage activities, including keylogging, screen captures, file exfiltration, and credential harvesting.
A Gap in Modern Defensive Layers
The efficacy of the attack stems from a fundamental reality of modern endpoint security: most protections are designed to operate only after the operating system has fully loaded. Endpoint Detection and Response (EDR) agents, multi-factor authentication (MFA) protocols, and AI-driven security tools all rely on an active, running OS to function. By inserting the backdoor at the pre-boot stage, OVERCAST PANDA successfully operated beneath the EDR agent and the authentication stack.
"We have the visibility once the machine boots up," Meyers explained to VentureBeat. However, the critical vulnerability lies in the window of time between the initial USB write and the next time the executive logs back into the system. During these hours, the laptop remains a compromised asset, its storage modified by the attackers, yet entirely invisible to security software that is not yet active. While CrowdStrike’s Falcon sensors eventually identified and disrupted the threat once FlowCloud began its processes, the initial infection was already firmly established on the disk.
Meyers attributed the operation to the Chinese Ministry of State Security. He noted that the individuals conducting these physical breaches were likely intelligence officers, agents of the Ministry of Public Security, or even hotel staff who had been compelled or incentivized to facilitate the intrusion. The choice of an agricultural conference as the target aligns with the broader intelligence-gathering priorities observed in China’s recent five-year plans, suggesting a strategic effort to gain competitive advantages in food security and related economic sectors.
Quantifying the Shifting Threat Landscape
The disclosures at Fal.Con 2026 highlighted that while physical attacks like those in Hainan are chilling, they represent only a fraction of the rapidly evolving threat landscape. During the event, CrowdStrike unveiled a suite of new AI-driven security products, including Falcon Guardian, SafeMind, the Agentic Identity Provider, and AI Gateway. These tools are designed to address a surge in automated, AI-powered threats that are increasingly challenging enterprise defenses.
Data from the 2026 Threat Hunting Report underscores the intensity of this shift. CrowdStrike reported that AI agent-triggered detection leads have grown at 2.5 times the rate of human-triggered incidents. Furthermore, cloud-conscious eCrime activity surged by 171% over the reporting period. Vishing (voice phishing) intrusions also doubled in the first half of 2026, with groups like SNARKY SPIDER demonstrating the ability to move from initial account compromise to full data exfiltration in under five minutes.
Despite these alarming statistics, Meyers emphasized that network-based attacks remain the primary concern for the average enterprise due to their ability to scale. "You can’t intrude on hotel rooms at scale," Meyers noted, contrasting the labor-intensive nature of the Hainan operation with the lightning-fast, AI-driven campaigns of groups like REVENANT SPIDER, which recently compromised 17 victims in less than an hour using custom web shells.
Bridging the Firmware Security Gap
For organizations, the challenge is that the most effective defenses against physical-access attacks are often neglected because they are deemed "inconvenient." The tools to mitigate such risks have existed for years; CrowdStrike, for instance, has integrated firmware attack detection and BIOS settings auditing into its Falcon sensor since 2019. Yet, the implementation of these controls often falls through the cracks of corporate bureaucracy.
To defend against future "evil maid" operations, security leaders must prioritize firmware-level hygiene. This includes disabling the ability to boot from external USB drives within the UEFI/BIOS, setting robust BIOS administrator passwords, and enforcing full-disk encryption with pre-boot authentication. Relying solely on standard BitLocker configurations—which can be susceptible to hardware-based attacks—is no longer sufficient for high-value targets.
Furthermore, the industry is increasingly advocating for the use of "clean" travel-only devices for international trips. These machines should be stripped of access to production environments, VPN configurations, and sensitive credentials. The philosophy is simple: if a device is taken into a high-risk environment and left unattended, it must be assumed that the physical integrity of the hardware has been compromised.
As CrowdStrike and other security leaders push forward with AI-integrated defensive layers, the Hainan incident serves as a sobering reminder that sophisticated adversaries will continue to exploit the simplest, most fundamental gaps in security. As long as organizational silos separate physical security policies from digital infrastructure management, the "evil maid" will remain a potent tool for state-sponsored intelligence services. For the modern executive, the lesson is clear: in an era of hyper-connected cyber warfare, the most effective security protocol may be the most basic—never bring a critical device into an environment where you cannot guarantee its physical security.