In a startling revelation that highlights the fragile perimeter of even the most secure government networks, security researchers have identified that several staffers at the White House are utilizing computers or mobile devices equipped with residential proxy services. These services, which effectively turn a user’s internet connection into a public relay point, have made the Executive Office of the President’s internet addresses available for rent by anonymous third parties.
Perhaps most concerning is the discovery that one of the primary services operating on these devices is a Russian-linked company. The founder of this service, Infatica, previously operated a web hosting firm that served as a critical infrastructure hub for the 2016 cyberattacks against election systems in Arizona and Illinois.
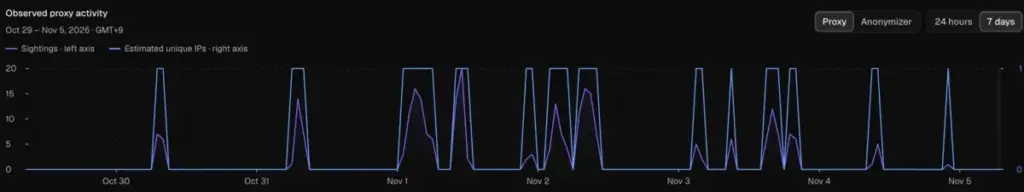
The security firm Layer3 Intel, which first identified the anomaly, reported that it detected multiple residential proxy nodes beaconing out from the specific internet address network reserved for the Executive Office of the President, known as AS2650. According to the firm’s telemetry, this proxy activity was not an isolated incident but a persistent phenomenon observed between October 5 and November 3. A detailed forensic review of the proxies available through the AS2650 network revealed that they successfully exited from the White House network 236 times during that roughly month-long window.
The implications of this exposure are significant. Residential proxy services operate by allowing customers to "rent" the IP addresses of everyday users, often without the users’ full knowledge or explicit consent regarding the security ramifications. By routing traffic through these nodes, a user can mask their true location or origin, making their web activity appear as though it is coming from a legitimate, trusted residential or corporate network. From the perspective of a website or a server, the traffic originates from the White House, not the proxy service’s end customer.
Following the initial disclosure by Layer3 Intel, the proxy tracking firm Synthient confirmed these findings via social media. Synthient’s analysis indicated that the activity observed originating from the White House’s network was tied to multiple installations of a software service called Infatica. Infatica is a proxy program frequently bundled into "free" mobile and desktop applications. Users often install these applications—ranging from games to utility tools—without realizing that the software contains a hidden component that turns their device into a gateway for strangers.
The connection to Vladimir Fomenko, the founder of Infatica, adds a geopolitical layer to the technical concern. Fomenko was previously the proprietor of King Servers, a hosting company that was identified as the source for six of the eight internet addresses utilized by Russian state security services to infiltrate and compromise election databases in Arizona and Illinois during the 2016 election cycle. While the current usage of Infatica by White House staffers appears to be a result of third-party software bundles rather than a targeted breach, the presence of infrastructure linked to a known actor in the Russian cyber-espionage ecosystem on a sensitive federal network has raised alarm bells among cybersecurity professionals.
The ecosystem of residential proxy providers is vast and largely opaque, with many services operating out of jurisdictions with minimal regulatory oversight, including China and Russia. While these companies often claim to provide legitimate services for tasks like market research or ad verification, they inherently provide a mechanism for anyone to bypass security controls by paying a nominal fee.
Layer3 Intel noted that the proxy exit nodes detected within the White House network were active on 26 of the 30 days during their observation period. Furthermore, the firm noted a specific pattern to the activity, with the majority of the connections occurring in the evening hours, specifically between 5 p.m. and midnight. This pattern strongly suggests that the proxy nodes are likely residing on employee-owned devices or work-issued machines that are being used for personal browsing or have been compromised by secondary applications while connected to the internal network.
Perhaps most unsettling is the discovery that Infatica is not the only culprit. Layer3 Intel reported that it identified 28 separate residential proxy services that were able to successfully route traffic through the White House network. "This is public access," the Layer3 Intel team stated in their report. "Anybody can obtain it by signing up to a public residential proxy service, paying a few dollars and sending requests through it. We did not selectively target this network or try to make our probes exit from it. We caught this by chance, simply by requesting global rotating access through these services."
The White House has not yet issued a formal statement in response to inquiries regarding the findings.
The danger posed by these services extends far beyond simple anonymization. Residential proxy networks have become a primary conduit for malicious activity, including large-scale account takeovers, advertising fraud, and the aggressive scraping of content for AI training models. However, the security risks to the local environment are arguably more immediate. In late 2025, researchers discovered that cybercriminals were actively exploiting vulnerabilities within these proxy services to probe local networks for weak points, effectively using the proxy nodes as a beachhead to deploy malware inside otherwise secure environments.
In January 2026, the severity of this threat was underscored when Synthient founder Ben Brundage demonstrated how cybercriminals were abusing vulnerabilities in these services to seize control of devices located within the local networks of unsuspecting users. This discovery forced a wide range of proxy providers to scramble for security patches.
"Some of these resellers sell bandwidth for as low as 60 cents a Gigabyte; that means for less than a dollar you can gain access into some of the most confidential and trusted networks," Brundage explained. He further noted that the reseller ecosystem is rife with anonymity, allowing criminals to purchase access to high-value networks while completely bypassing standard "Know Your Customer" (KYC) identity verification protocols.
The prevalence of these proxies in high-security environments is often a byproduct of the "monetization" of free software. App developers, seeking to generate revenue from free tools, often embed software development kits (SDKs) provided by residential proxy networks. These SDKs turn the user’s device into a node, and the developer receives a small commission for every installation that successfully routes traffic. Employees who download these applications on devices that are subsequently connected to sensitive networks inadvertently expose those networks to the entire global proxy pool.
The scale of the problem is not limited to the White House. Data gathered by the proxy tracking service Spur during a webinar in early 2026 revealed that residential proxies were present in nearly 300 government-owned and operated networks, as well as 318 utility companies, 166 healthcare providers, and 141 financial institutions. Security firm Infoblox similarly reported earlier this year that approximately 65% of its customer base had queried one or more domains associated with residential proxy networks, suggesting that the "leakage" of these secure networks into the proxy ecosystem is a widespread and systemic vulnerability that organizations are struggling to contain. As digital perimeters become increasingly porous, the challenge for government and private entities alike will be to implement more rigorous endpoint controls to prevent employee devices from becoming involuntary participants in a global network of commercial and potentially malicious proxies.