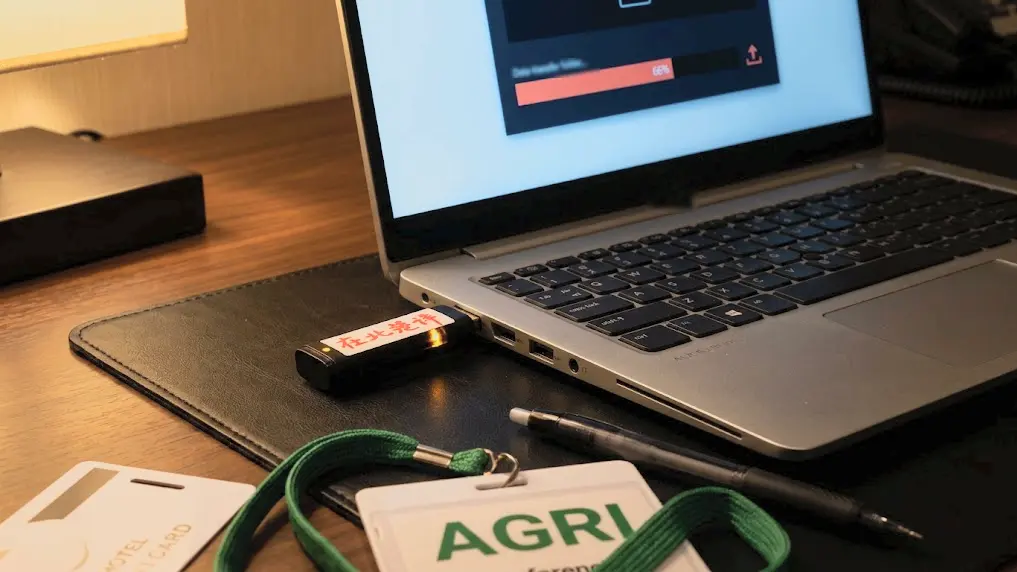
In a chilling demonstration of how traditional "low-tech" espionage can outmaneuver high-end digital defenses, a Chinese state-linked hacking group has successfully compromised executive laptops at an agricultural industry conference on Hainan Island. Rather than relying on sophisticated phishing campaigns, network vulnerabilities, or zero-day exploits, the intruders bypassed modern cybersecurity stacks by physically infiltrating hotel rooms and booting target machines from unauthorized USB drives while the executives were away at dinner.
The operation, attributed to the group known as OVERCAST PANDA, was detailed in CrowdStrike’s 2026 Threat Hunting Report and further illuminated during the company’s annual Fal.Con 2026 conference. The breach highlights a significant gap in the modern security perimeter: while enterprise-grade tools are increasingly adept at defending against network-based threats, they remain largely blind to physical tampering that occurs beneath the operating system and before the security software even begins to load.
A New Twist on the "Evil Maid" Attack
Security researchers have long recognized the concept of an "evil maid attack," a term popularized by Joanna Rutkowska in 2009 to describe the physical compromise of an unattended device via a bootable USB stick. While such physical-access operations are relatively rare among the nearly 300 named adversaries currently tracked by CrowdStrike, the OVERCAST PANDA campaign represents a sophisticated, targeted evolution of the practice.
According to Adam Meyers, CrowdStrike’s senior vice president of counter adversary operations, the campaign took place between March and May 2026. The operational timeline was precise and brazen: in one instance, an intruder entered a hotel room at approximately 8 p.m. local time, followed by a second intrusion at another room shortly before 10 p.m. During these brief windows, the hackers deployed a backdoor known as "FlowCloud" directly to the storage of each laptop. By rebooting the machines and exiting the rooms without leaving a digital trail on the network, the actors ensured that the devices appeared untouched.
The use of FlowCloud is not new, but its application in this context is highly deliberate. Previously documented by Proofpoint in 2020 and tracked by NTT Security’s SOC as a tool for USB-delivered infections, FlowCloud is a versatile piece of malware. When the executives returned to their rooms and powered on their devices the following morning, the trigger fired, loading the backdoor into the operating system. Once active, the malware enabled keylogging, screen capture, file collection, and the harvesting of corporate credentials—all occurring under the nose of the user.
Why Modern Defense Layers Fled the Field
The success of the Hainan operation underscores the inherent limitations of modern endpoint detection and response (EDR) systems. EDR agents, by design, require the operating system to be fully loaded and running to provide protection. Similarly, multi-factor authentication (MFA) requires a user login attempt, and phishing training assumes a digital vector of entry.
OVERCAST PANDA’s methodology effectively bypassed these layers by operating at the firmware level. Because the compromise occurred below the running OS, the EDR agent was essentially dormant during the initial infection. By the time the Falcon sensor picked up the malicious process after the morning boot, the implant and its trigger were already embedded on the disk.
"Hotel entry is a very common thing," Meyers noted during an interview at Fal.Con. "Talk to any corporate physical security person. They’re generally aware of hotel entry, but I think what is unique is the combination of hotel entry with the deployment of malware."
Meyers attributed the operation to China’s Ministry of State Security (MSS). The physical entry itself likely involved either intelligence officers or hotel staff who had been coerced or bribed into facilitating the intrusion. This focus on an agricultural conference is not arbitrary; it aligns with China’s broader strategic collection priorities, which are deeply integrated into the nation’s five-year economic and technological development plans.
Balancing AI-Driven Security with Hardened Firmware
CrowdStrike’s disclosure of the OVERCAST PANDA incident occurred just weeks before the company unveiled a massive slate of AI-powered security products at Fal.Con 2026, including the "SafeMind" system—a collaborative development with Nvidia utilizing Nemotron open models—and the "Falcon Guardian" runtime security layer. While these tools address a surge in cloud-conscious eCrime and AI-agent threats, they also serve as a reminder that the digital security landscape is moving toward increasingly automated, network-speed combat.
However, the OVERCAST PANDA campaign serves as a sobering reminder that the most sophisticated AI-driven defense cannot solve a problem created by a physical USB stick and a hotel door key. Meyers emphasized that while the industry is understandably focused on scaling defenses against network-based AI threats—such as those posed by groups like REVENANT SPIDER, which can compromise dozens of victims in under an hour—the "slow", unscalable nature of physical espionage remains a persistent, high-impact threat for high-value targets.
"You can’t intrude on hotel rooms at scale," Meyers explained. "You can’t intrude on physical devices at scale. And even then, it’s just one device." Nevertheless, for an executive representing a major firm, "one device" is often enough to grant an adversary access to an entire corporate network or proprietary trade secrets.
Closing the Gap: Practical Hardening for Global Travel
For security leaders, the lesson of the Hainan breach is that the solution to this specific threat is not found in a new product, but in the rigorous application of existing, "inconvenient" security controls. The vulnerability exists because many enterprise devices are not configured to block unauthorized boot sequences, leaving them susceptible to simple, cheap physical attacks.
The recommended countermeasures are well-established but often ignored in the name of user convenience. The most critical step is to disable external booting within the UEFI settings and protect that configuration with a robust BIOS administrator password. Furthermore, the implementation of full-disk encryption alone is insufficient if it relies solely on a Trusted Platform Module (TPM); researchers have repeatedly demonstrated that volume keys can be intercepted via bus-sniffing. True protection requires pre-boot authentication, forcing the user to provide a PIN or a physical key before the operating system can even decrypt the storage.
Additionally, organizations must maintain strict firmware monitoring and ensure that revocation lists—such as those for the UEFI shims that have previously undermined Secure Boot—are kept up to date. Yet, as Meyers pointed out, the most effective strategy for international travel remains the most draconian: the "burner" policy.
"Don’t bring anything with you that you’re not comfortable with handing over to a foreign intelligence service," Meyers advised. He noted that during his own tenure at CrowdStrike, he utilized dedicated, wiped-clean laptops and temporary email accounts when traveling overseas, operating under the assumption that any device entering a foreign jurisdiction is subject to physical seizure and inspection.
Ultimately, the OVERCAST PANDA incident highlights a fundamental fracture in organizational security. While one department may be tasked with deploying the latest AI-driven cloud-threat defense, another is responsible for hardware procurement and travel policy. When these silos remain disconnected, the most advanced security suite in the world is rendered irrelevant by a simple physical exploit that has been known to the security community for nearly two decades. As long as executives carry production-access devices into high-risk environments without hardened firmware configurations, they remain vulnerable to the oldest trick in the book: an adversary waiting in the room while they are away.