In a significant escalation of the federal government’s campaign against the prolific hacking collective known as ShinyHunters, FBI agents arrested a Canadian cybersecurity executive in Pennsylvania on Thursday. The arrest comes as part of an expanding, high-stakes investigation into the group, which recently gained notoriety for breaching FBI systems and exfiltrating sensitive personal data belonging to thousands of federal agents.
While the FBI has remained tight-lipped regarding the specific identity of the individual, multiple sources familiar with the matter have confirmed the arrest to KrebsOnSecurity. The development follows a report from The New York Times, which first signaled that a Canadian national had been taken into custody in Pennsylvania on suspicion of providing material assistance to the ShinyHunters operation. FBI Director Kash Patel acknowledged the arrest in a brief statement on social media platform X, though he declined to name the suspect or provide granular details regarding the charges.
A Professional Caught in the Crosshairs
According to sources close to the investigation, the suspect was in Pennsylvania to attend the Cyber Risk Summit, a high-profile industry gathering held at the Loews Philadelphia Hotel between October 5 and October 7. The individual is reportedly an executive associated with a Canadian security firm that specializes in the complex, high-pressure field of ransomware negotiations—a sector where experts often act as intermediaries between criminal extortionists and victimized organizations.
Online records from the Cyber Risk Summit indicate that a Canadian security company, Cypfer, was the summit’s primary sponsor. Further scrutiny of the event’s speaker roster and professional networking platforms, such as LinkedIn, identified Edward Dubrovsky as a prominent figure in this space. Dubrovsky, previously associated with Cypfer and currently affiliated with another security firm, CyberSteward, had publicly signaled his intention to attend the Philadelphia conference alongside his team.
Following the initial identification of the suspect, a spokesperson for Cypfer sought to clarify Dubrovsky’s history with their organization. The spokesperson stated that while Dubrovsky’s LinkedIn profile previously claimed he was a founder or co-founder of the firm, he had actually served as a managing director before resigning in November 2025.

Extortion and the "Strategic Response"
Federal court records reveal that an individual named Edward Dobrovsky—with a slight spelling variation from the LinkedIn profile—was arrested in Pennsylvania on October 8. He faces serious charges, including conspiracy to threaten to impair the confidentiality of information with the intent to extort money, and interference with commerce by threats. While the core complaint remains under seal, filings indexed at CourtListener.com offer a glimpse into the legal allegations, which center on the intersection of professional cyber-defense and the illicit world of extortion.
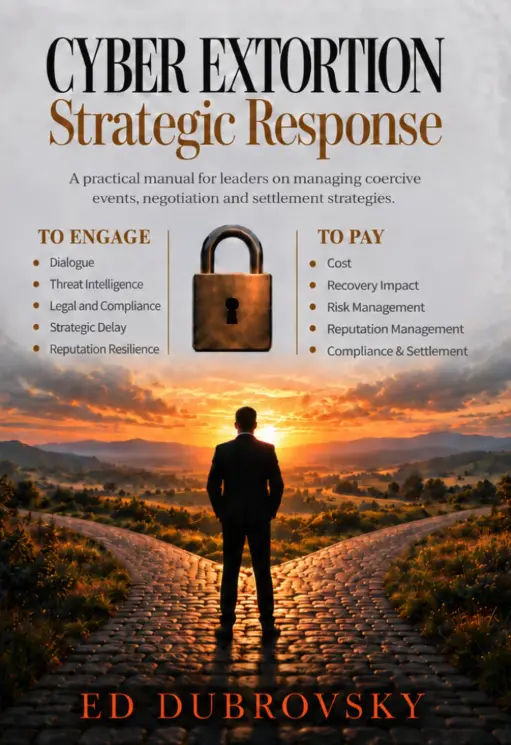
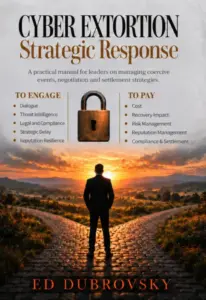
The arrest has drawn attention to Dubrovsky’s professional background, most notably his authorship of Cyber Extortion Strategic Response. The 252-page book positions itself as a guide to navigating the aftermath of a ransomware attack, promising to lead readers "beyond the ransom note." In the book’s promotional material, the author emphasizes the delicate nature of engaging with cybercriminals.
"At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay," an excerpt from the book’s Amazon listing reads. "Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."
The irony of an expert on cyber-extortion facing federal charges for allegedly participating in such activities has not been lost on industry observers. Currently, U.S. Bureau of Prisons records show that a 54-year-old Edward Dubrovsky is being held at a federal facility in Philadelphia. However, a notice filed on October 9 indicates that the case is being transferred to the Eastern District of Texas. Sources suggest this move is strategic, as the Texas field office has become the epicenter of the FBI’s centralized investigation into the ShinyHunters collective. As of the time of this report, Dubrovsky does not appear to have retained legal counsel, and the court has yet to appoint a public defender.
The Rise and Reach of ShinyHunters
ShinyHunters has established itself as one of the most aggressive and persistent threats in the modern digital landscape. The group typically targets software-as-a-service (SaaS) companies, leveraging sophisticated phishing campaigns and the use of stolen credentials to breach corporate environments. Once inside, the hackers siphon off massive caches of data, threatening to leak the information publicly unless a ransom is paid. According to FBI assessments, the group has successfully extorted more than $70 million from various victims over the course of this year alone.

The investigation appears to be reaching a turning point. Sources indicate that federal agents have been exhaustively analyzing electronic devices seized during a recent operation in the Netherlands, where Dutch authorities arrested the convicted cybercriminal Pepijn van der Stap. The intelligence gathered from these devices is believed to have been instrumental in the recent flurry of activity. Insiders suggest that further charges against individuals at companies specializing in ransomware negotiation may be on the horizon as the FBI works to dismantle the networks that support these groups.
Internal Turmoil and Agency Breaches
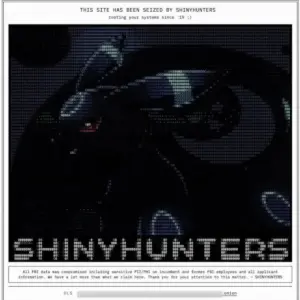
The pressure on ShinyHunters intensified following the arrest of Van der Stap, which triggered a power struggle within the group. A member operating under the handle "Rey" assumed control of the collective and immediately began taunting the FBI. This digital bravado took a darker turn when the group targeted the FBI’s own online recruitment portal. The breach resulted in the theft of sensitive data, including details regarding the specific units and specializations of federal agents, as well as highly confidential medical and psychiatric records.
The arrogance of the group, however, ultimately played into the hands of investigators. Last week, Reuters reported that "Rey"—who has been identified as a teenager named Saif Al-din Khader—was apprehended and is reportedly cooperating with federal authorities. Investigations revealed that Khader was allegedly orchestrating extortion attempts against a navigation and digital aviation unit recently divested by Boeing.
The arrest of a high-level executive from a cybersecurity firm, when viewed alongside the capture of central figures like Khader and Van der Stap, suggests a broadening scope in how federal law enforcement is addressing the infrastructure of cybercrime. By targeting not only the hackers themselves but also those who facilitate the financial and strategic mechanisms of extortion, the FBI is signaling a more aggressive stance in its battle against digital threat actors.
As the legal proceedings against the individuals involved in the ShinyHunters saga move forward, the cybersecurity industry is bracing for further disclosures. With the case now concentrated in the Eastern District of Texas and court documents remaining largely under seal, the full extent of the alleged conspiracy remains to be seen. For now, the arrest of a prominent ransomware negotiator serves as a stark reminder of the thin line between those who defend against cyber threats and those who are accused of exploiting them. The FBI has declined to provide further comment as the investigation remains active and fluid.