A teenager from Amman, Jordan, suspected of acting as a central figure in the notorious data theft and extortion syndicate known as "ShinyHunters," has been taken into custody. Sources confirm that the suspect, who operates under the hacker handle "Rey," is currently cooperating with the Federal Bureau of Investigation (FBI) to assist in identifying other members of the sprawling, decentralized hacking collective.
The detention of the suspect, identified in previous reports as Saif Al-din Khader, occurred at a critical juncture for the group. At the time of his apprehension, ShinyHunters was actively engaged in an extortion campaign targeting a business unit recently divested by the global aerospace giant Boeing. The irony of the target—a company providing services for the aviation sector—is particularly stark, as the suspect’s father is reportedly employed by Royal Jordanian Airlines, a carrier whose fleet relies heavily on Boeing aircraft.
The Rise and Fall of ‘Rey’
The confirmation of Khader’s detention follows an October 3 report by Reuters, which cited three unnamed sources regarding the arrest of a key ShinyHunters member in Amman. This individual, whom KrebsOnSecurity profiled in November 2025 as "Rey," had openly admitted to participating in various ransomware operations. His digital trail, however, became increasingly chaotic in the weeks leading up to his arrest.
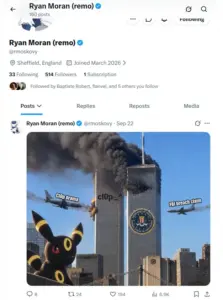
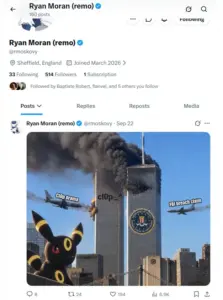
On September 28, reports emerged that Dutch authorities had apprehended 24-year-old Pepijn van der Stap, a convicted cybercriminal suspected of providing technical support to ShinyHunters. According to evidence gathered during the investigation, Rey assumed control of the ShinyHunters brand immediately following Van der Stap’s arrest on September 15. In a display of bravado that ultimately drew unwanted attention, Rey began publicly boasting about successfully breaching the FBI and extorting the infamous "Cl0p" ransomware group.

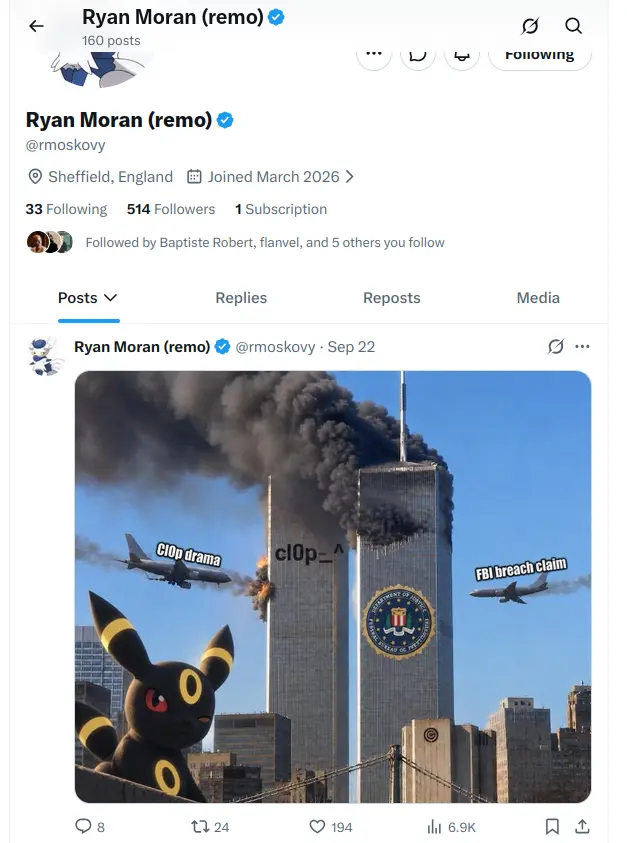
In an attempt to misdirect investigators and settle scores, Rey utilized his Twitter/X account to mock both the FBI and the Cl0p syndicate. By incorporating images of the avatar previously used by Van der Stap—who went by the alias "Umbreon"—Rey attempted to frame the Dutch suspect for his own activities. This tactic, while sophisticated in its attempt at misdirection, likely accelerated the scrutiny that led to his capture.
Exploiting the Oracle PeopleSoft Vulnerability
The surge in ShinyHunters’ activity throughout 2026 was fueled by the exploitation of a critical vulnerability (CVE-2026-35273) in Oracle’s PeopleSoft platform. This software-as-a-service (SaaS) solution is a cornerstone for many major organizations, managing complex internal operations such as human resources, payroll, and benefits.
ShinyHunters first began utilizing this vulnerability as a zero-day exploit in June. Despite Oracle issuing a rapid security patch and Mandiant providing specific web application firewall (WAF) rules to mitigate the threat, the group proved resilient. In a recent shift, the hackers bypassed Mandiant’s security measures by employing a well-documented URL-encoding trick. A September 25 report from Mandiant and the Google Threat Intelligence Group (GTIG) confirmed that ShinyHunters successfully mass-exploited this vulnerability, siphoning sensitive data from dozens of systems spanning sectors from healthcare and agriculture to government and higher education.
The fallout from these attacks was severe. On October 5, Reuters reported that the FBI had terminated a contractor at Accenture. The decision followed a security failure that left the FBI’s recruitment portal vulnerable, resulting in a breach that exposed the sensitive personal data of more than 5,000 FBI personnel, including their specialized units, medical records, and psychiatric history.

The Boeing Connection and ‘Rey’s’ Father
The investigation into the extortion of the former Boeing unit, Jeppesen ForeFlight, provided the FBI with the leverage needed to prioritize the pursuit of "Rey." Sources familiar with the investigation indicated that the theft of data from this specific subsidiary introduced significant operational safety and security risks, heightening the urgency of the case.
Boeing confirmed the extortion attempts in a statement, noting that the incident involved data from Jeppesen ForeFlight, which the company sold to the private equity firm Thoma Bravo for $10.55 billion in November 2025. While Boeing is reviewing the situation, Jeppesen ForeFlight has maintained that their internal operations and products remain unaffected.
The personal connection between the suspect and the aviation industry has been a focal point of the investigation. In early 2025, Rey claimed on Telegram that his father was an airline pilot. While independent confirmation of his father’s specific role is limited, records obtained from a previously compromised family computer showed that the elder Khader used the same credentials to access multiple employee portals for Royal Jordanian Airlines. Despite multiple attempts by security journalists to reach out for comment, neither the father nor the son has responded to inquiries regarding these findings. Following these queries, Rey began a systematic purge of his social media presence, including the accounts used to taunt law enforcement.
Escalating Allegations Against Van der Stap
While Rey’s cooperation has shifted the focus of the FBI, the legal situation surrounding the Dutch suspect, Pepijn van der Stap, has taken a darker turn. Dutch media outlets, including RTL, reported on September 29 that investigators are probing allegations that Van der Stap may have orchestrated at least two murder-for-hire plots.

Van der Stap, who had recently completed a four-year prison sentence for cybercrime, had been attempting to rebrand himself as a "reformed" hacker. At the time of his arrest, he was employed as an "offensive security lead" at Neo Security, a firm based in Amsterdam. Benjamin Korper, the owner of Neo Security, stated that he has hired an external firm to audit Van der Stap’s work, though no evidence has yet surfaced to suggest he hacked his own employer or their clients. The September 15 raid on his home, which reportedly involved the use of flash-bang grenades, suggests that Dutch authorities viewed the threat posed by Van der Stap as significant and imminent.
The ‘Dread Pirate Roberts’ Model of Cybercrime
The evolution of ShinyHunters serves as a cautionary tale regarding the modern "franchise" model of cybercrime. Experts draw parallels to the "Dread Pirate Roberts" persona from The Princess Bride: the brand survives even as the individuals behind it are arrested and replaced. The original members of the group, many of whom were French citizens, have largely been incapacitated by law enforcement, yet the name persists.
Current investigations suggest that the FBI is now focusing on a network of freelancers who provide stolen credentials to these platforms in exchange for a percentage of the ransom proceeds. Within the Telegram channels where these hackers congregate, the reaction to Rey’s arrest has been one of ridicule. Many in the community viewed Rey as a "larper"—a novice who bought the group’s old PGP keys to capitalize on a name he did not earn.
A Telegram channel known as "The Battle," which has been actively documenting and mocking Rey’s activities, described his downfall as the result of a "serious mistake" in attempting to revive a defunct brand. According to the administrators of this channel, Rey’s attempts to use the ShinyHunters name to negotiate deals for a 25% to 30% cut of ransoms likely generated over $200 million in damages, drawing the concentrated ire of both international law enforcement and rival criminal groups.

In a final act of defiance, the group claimed in an interview with The Register that their decision to hack the FBI was a strategic "public relations" move. They argued that the agency’s May 2026 warning against paying ransoms was unprofessional and that the hack was necessary to "protect their business." By attempting to refute the FBI’s narrative, however, they only succeeded in cementing their status as a high-priority target, ultimately leading to the dismantling of their operations and the cooperation of their most vocal representative.