In the fast-paced world of cloud infrastructure, the primary challenge for developers has often been the friction between writing code and successfully deploying it. Last week, Amazon Web Services (AWS) signaled a strategic shift toward reducing this friction. Rather than introducing entirely new paradigms of compute that force developers to rethink their architecture, AWS focused on shortening the distance between existing codebases and production environments. The introduction of AWS Lambda Web Functions and the broader push to simplify provisioning for services like Amazon S3 reflect a unified philosophy: meet developers where they are, using the tools they already trust.
The Evolution of Serverless: AWS Lambda Web Functions
The most significant headline to emerge this week is the launch of AWS Lambda Web Functions. For years, developers utilizing AWS Lambda have had to adapt their web applications to fit the service’s specific event-handler model. This often required rewriting code to translate HTTP requests into a format the Lambda environment could digest. With the new Web Functions form factor, that architectural hurdle is effectively removed.
AWS Lambda Web Functions allows developers to run standard, port-listening HTTP servers—built using popular frameworks such as Express, Hono, Fastify, or Next.js—directly on Lambda without the need for cumbersome adapters. The process is remarkably streamlined: a developer can execute the aws lambda-web deploy command, and within a minute, they are provided with a live, functional HTTPS URL. By eliminating the requirement for infrastructure setup or framework-specific lock-in, AWS is significantly lowering the barrier to entry for serverless deployments.
This release brings Lambda to a total of three distinct form factors, all underpinned by the high-performance Firecracker microVM isolation technology. These include Event Functions, which remain the standard for asynchronous processing; the new Web Functions, tailored for user-facing layers; and MicroVMs, which offer a stateful sandbox for running untrusted or complex code. The ability to compose these three models within a single application provides developers with a versatile toolkit that can handle everything from background data processing to high-traffic frontend delivery.
Crucially, this is not merely a repackaging of existing technology. AWS has optimized the execution environment to handle up to 128 concurrent requests, allowing for better resource utilization. In traditional serverless models, traffic bursts often lead to a one-to-one mapping between requests and environments, which can be inefficient. By allowing a single warm environment to handle multiple requests, and by billing based on actual CPU time rather than total wall-clock time, AWS is fundamentally changing the cost-performance arithmetic for developers. This is particularly advantageous for server-side rendering, API backends, and AI inference endpoints where a significant portion of execution time is spent idling while waiting for I/O or token streaming.
For those looking to scale, the integration is robust. Developers can easily replicate their application across multiple regions using the --regions flag, enabling latency-based routing behind a single global URL. Furthermore, the ability to split traffic across different revisions using weighted routing provides a native path for canary rollouts, reducing the risk associated with deploying new code. Currently available in five regions and supporting Node.js 24 on Arm64, this new capability represents a major step forward for web application performance on AWS. Additionally, the integration with Amazon CloudFront, which can now use a Web Function endpoint as an origin, ensures that global content delivery remains secure and performant.
The Critical Need for AI Governance: Trust in Depth
While the ease of deployment continues to accelerate, the complexity of the systems being deployed is also rising, particularly with the proliferation of autonomous AI agents. The second major focus of the week was not a new feature launch, but a crucial discussion on the governance of these agents. As businesses rush to integrate AI into their operational workflows, the challenge of maintaining control without stifling the agent’s autonomy has become a primary concern for architects.
The prevailing wisdom has often been to keep a human in the loop for every decision an agent makes. However, as the scale of these operations grows, this approach tends to break down. Human oversight, when applied to every single action, eventually leads to fatigue and diminished vigilance, resulting in missed errors and decreased efficiency. AWS’s perspective, detailed in their latest guidance on "Trust in Depth," argues that the answer lies in a structured, multi-layered approach to governance.
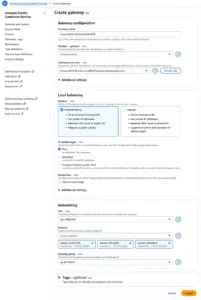
AWS outlines this strategy through four core dimensions: scope, know, bound, and observe. The core thesis is that an agent’s operational boundaries must exist independently of the agent’s own reasoning process. If an agent is responsible for defining its own constraints, it remains inherently vulnerable to manipulation or internal logic errors. By moving these policies into Amazon Bedrock AgentCore and enforcing them at the gateway level, organizations can ensure that the agent operates within a hardened perimeter.
This approach draws on over a decade of experience AWS has gained from running automated reasoning systems in production. With AWS Identity and Access Management (IAM) managing more than 2.1 billion requests per second, the company has proven that sophisticated, rule-based automated governance can scale to meet massive global demand. The application of this same rigorous logic to AI agents is a significant evolution. By treating agent rules with the same level of architectural gravity as identity policies, organizations can empower their agents to act autonomously while maintaining a high degree of confidence in the security and compliance of those actions.
Looking Ahead
As AWS continues to bridge the gap between development convenience and production-grade security, the ecosystem is clearly moving toward a model of "invisible" infrastructure. Whether it is the ease of deploying a web server with a single command or the implementation of robust, policy-based governance for AI agents, the common denominator is the removal of manual, repetitive tasks that do not add direct value to the end user.
For developers and architects, the path forward involves embracing these higher-level abstractions. By leveraging tools like Lambda Web Functions for compute and Bedrock AgentCore for AI policy enforcement, teams can focus their energy on building unique business value rather than managing the plumbing of the cloud. As we look toward the coming weeks, it will be interesting to see how these patterns of "abstraction and automation" continue to permeate other areas of the AWS portfolio.
For those interested in diving deeper into these topics, the AWS Compute Blog offers a comprehensive walkthrough of the new Lambda Web Functions, providing detailed insights into performance tuning and migration strategies. Furthermore, the AWS Builder Center remains a vital resource for connecting with the broader developer community, allowing for the sharing of solutions and best practices as these new tools are adopted in real-world scenarios.
As always, the AWS "What’s New" page remains the definitive source for the latest updates across the platform. With the rapid pace of change, staying informed on these foundational shifts is essential for any builder looking to maintain a modern, secure, and efficient infrastructure. We will continue to track these developments and provide the latest updates in our next weekly roundup.