Authorities in the Netherlands have apprehended a 24-year-old man, a convicted cybercriminal with a history of high-profile data theft, on suspicion of providing critical support to the prolific and aggressive hacking collective known as "ShinyHunters." The arrest, which occurred in mid-September 2026, has triggered a volatile reaction from the remaining members of the group, who responded with a series of brazen, high-stakes attacks, including a significant breach of the FBI’s job application portal and the targeted extortion of the Russian-linked ransomware syndicate Cl0p.
The suspect, identified by sources familiar with the investigation as Pepijn van der Stap, is a resident of Almere and Lelystad. His detention marks a major development in the ongoing efforts by European law enforcement to dismantle the infrastructure supporting ShinyHunters. Van der Stap is no stranger to the Dutch legal system; he was previously convicted in 2023 for his involvement in an extensive campaign of data theft and extortion, crimes that prosecutors estimated netted him between €1.5 million and €2.7 million.
A Dual Existence: From Researcher to Cybercriminal
During his 2023 trial, van der Stap provided a candid—and often unsettling—look into the "Dr. Jekyll and Mr. Hyde" reality of his life. He confessed to operating under the pseudonym "Umbreon," a handle inspired by the popular Pokémon character, to infiltrate systems, extort victims, and dump sensitive information on illicit English-language forums such as the now-shuttered RaidForums and Breached.
Yet, this life of digital crime stood in stark contrast to his public persona. By day, van der Stap was a software engineer for Hadrian, an Amsterdam-based cybersecurity startup. He further burnished his reputation by volunteering for the Dutch Institute for Vulnerability Disclosure (DIVD), a nonprofit organization dedicated to ethical security research.

Van der Stap ultimately confessed to his illicit activities and was sentenced to four years in prison, with one year suspended. During the legal proceedings, he opted to remain in custody rather than return home, citing a lack of adequate support for his psychological struggles, which he attributed to childhood trauma and resulting PTSD. He regained his freedom in December 2025.
In a September 9, 2026, interview with KrebsOnSecurity, van der Stap painted a picture of a man attempting to pivot toward a legitimate career, emphasizing his desire to contribute positively to society. At the time, he was employed as an offensive security lead at the Dutch firm Neo Security. He spoke of the ongoing burden of civil lawsuits and the necessity of making restitution to his victims. However, the tone of his life shifted shortly thereafter; communication with him ceased abruptly, and individuals close to him reported an inability to reach him for weeks, coinciding with the timeline of his arrest on or around September 16.
The Odido Breach and Police Scrutiny
The Dutch authorities’ interest in van der Stap is believed to be linked to a broader, intense investigation into ShinyHunters. The police have been actively seeking public assistance to identify a voice from a February 2026 recording of a social engineering attack against Odido, the Netherlands’ largest mobile telecommunications provider. During that intrusion, a native Dutch speaker—purportedly a ShinyHunters member—tricked an employee into accessing a spoofed website. That single point of failure allowed the group to exfiltrate the personal data of more than 6.2 million Dutch citizens.
ShinyHunters has brazenly confirmed in communications with Dutch media that the suspect in the Odido audio clip is indeed a member of their collective. In a defiant statement provided to the NL Times, the group claimed they were providing their associate with full emotional, mental, and financial support, including legal counsel. They dismissed the Dutch police as "incompetent" and "irrelevant," warning that the authorities would need "all the luck in the world" to stop them from launching further large-scale operations within the country.

Escalation: The FBI and Beyond
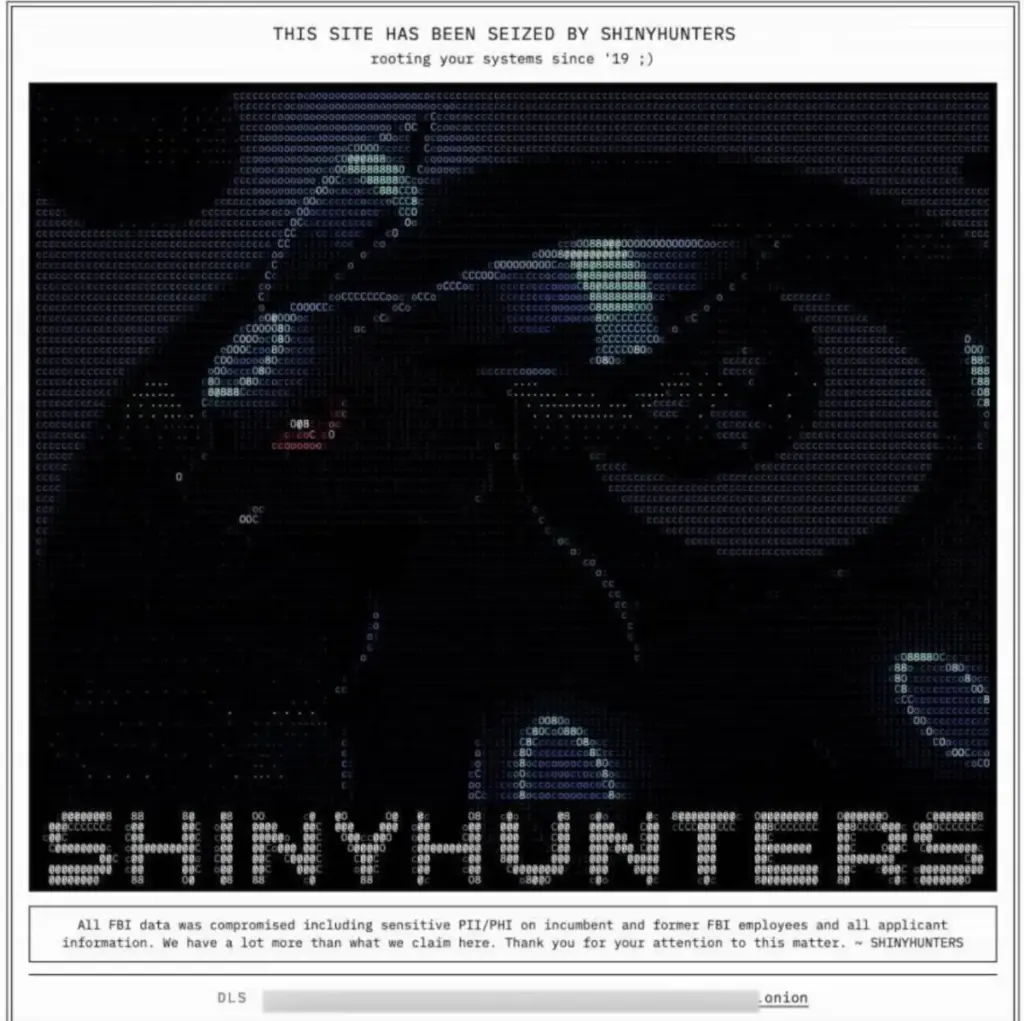
The fallout from van der Stap’s detention became globally apparent when ShinyHunters claimed responsibility for a sophisticated breach of the FBI’s job application portal, apply.fbijobs.gov. The attack exposed the Social Security numbers and personal details of more than 5,000 officials. According to reports from 404 Media and Reuters, the stolen files included specific job titles, such as special agents and investigators tasked with monitoring foreign state-backed cyber threats. Some of the shared documentation even contained highly sensitive psychiatric and medical records of FBI personnel.
The FBI has since confirmed the compromise of the portal. Investigations revealed that the group gained access by exploiting a vulnerability (CVE-2026-35273) in Oracle’s PeopleSoft, a widely used human resources and payroll management platform. Although Oracle released a patch for the vulnerability, which ShinyHunters had been weaponizing as a zero-day since June, the hackers managed to bypass security mitigations. Security researchers at Mandiant and the Google Threat Intelligence Group (GTIG) confirmed that the group utilized a URL-encoding trick to circumvent web application firewall rules, allowing for the mass exploitation of systems across healthcare, government, technology, and agriculture.
The fingerprint of the "Umbreon" persona appeared prominently in the group’s propaganda. The defacement image left on the FBI’s portal included an ASCII art depiction of the Umbreon Pokémon character, mirroring the imagery used by ShinyHunters in their 2020 hack of Hackforums.
Internal Strife and the "Rey" Factor
Analysts tracking the group suggest that the recent, high-risk attacks represent a strategic shift in the group’s operations. Sources indicate that this change is driven by a new leadership dynamic following the takeover of the ShinyHunters brand by a teenage cybercriminal based in Amman, Jordan, known as "Rey." Rey is a key operative in the "ScatteredLapsussHunters" (SLSH) alliance, a conglomerate formed by the remnants of Scattered Spider, LAPSUS$, and ShinyHunters.

Tensions reportedly run high between Rey and the Dutch hacker, with evidence suggesting that the inclusion of the "Umbreon" image in the FBI hack may have been a calculated move by Rey to frame the Dutch national for the attack. Rey’s digital footprint has been monitored closely by cybersecurity firms like KELA since 2025. Despite inquiries sent to his family, and his father’s awareness of his son’s alleged activities, the young hacker’s influence over the collective appears to be growing, as evidenced by his provocative social media posts taunting both the FBI and the Cl0p ransomware group.
The friction between these groups is rooted in failed partnerships. Earlier this year, ShinyHunters and SLSH had attempted to collaborate with TeamPCP, a group specialized in compromising code supply chains. That partnership crumbled after the groups accused one another of sabotaging their monetization efforts. Mandiant, having infiltrated TeamPCP’s operations, secretly fed stolen credentials to cloud providers like Microsoft and Amazon, rendering the data worthless and sparking a cycle of mutual recrimination.
A Legacy of Data Collection
While the current leadership of ShinyHunters appears motivated by massive, rapid-fire extortion—with estimates suggesting they are on track to generate nearly $100 million in 2026—van der Stap’s original motivation remained distinct. In previous interviews, he described his criminal activity not as a quest for wealth, but as a compulsion for "collecting" and "organizing" stolen data.
As the legal proceedings against van der Stap move forward, the Dutch police have confirmed that the 24-year-old will appear before the chambers of the Rotterdam District Court on September 29. Meanwhile, the security community remains on high alert, watching to see whether the arrest serves as a deterrent to the emboldened collective or acts as a catalyst for further retaliatory strikes against global targets.