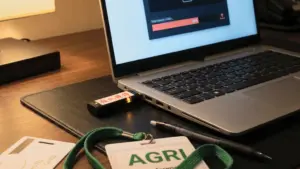
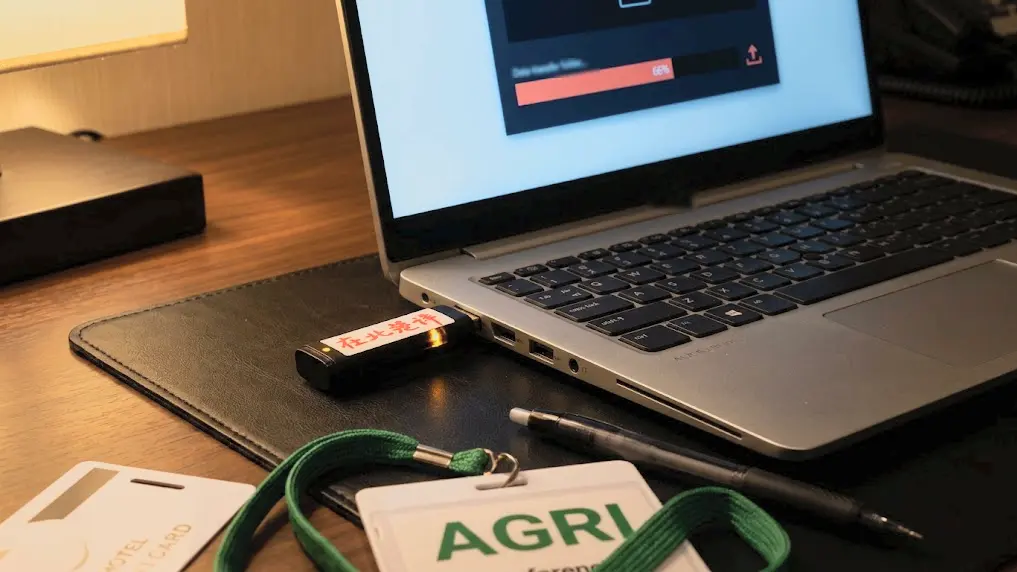
In a stark reminder of the persistent physical vulnerabilities facing corporate travelers, a Chinese state-linked hacking group has been identified executing a sophisticated, "low-tech" campaign against agricultural industry executives. Rather than relying on the common digital vectors of phishing or network exploits, the group—tracked by cybersecurity firm CrowdStrike as OVERCAST PANDA—gained unauthorized access to hotel rooms on Hainan Island this past spring. Once inside, the intruders physically booted target laptops from malicious USB sticks while the executives were away at dinner, effectively bypassing traditional endpoint security measures.
The details of this operation were brought to light by CrowdStrike in its 2026 Threat Hunting Report and further elaborated upon during the company’s Fal.Con 2026 conference in Las Vegas. Adam Meyers, CrowdStrike’s senior vice president of counter adversary operations, revealed a chilling timeline of the intrusions: in one instance, an operative entered a hotel room at approximately 8 p.m. local time, followed by a second breach at another room at 9:57 p.m. The intruders deployed a backdoor known as "FlowCloud" directly to the storage of the targeted machines before rebooting them and departing, leaving no digital trail of network intrusion or suspicious email activity.
The campaign, which unfolded between March and May 2026, serves as a modern-day manifestation of the "evil maid" attack—a concept long discussed in security circles since researcher Joanna Rutkowska first demonstrated the technique in 2009. While such physical-access operations are rare among the 290 distinct adversaries monitored by CrowdStrike, the OVERCAST PANDA operation is notable for its tactical refinement. Unlike the methods associated with other groups, such as MUSTANG PANDA, which often rely on a user to unwittingly plug in a dropped USB drive, OVERCAST PANDA took control of the machine’s boot sequence, ensuring the malware was present before the operating system even loaded.
The Mechanics of an "Evil Maid" Deployment
When the targeted executives returned to their rooms and powered on their devices the following morning, the malicious trigger fired, and the FlowCloud backdoor loaded into the operating system. Once active, the malware provided the attackers with a comprehensive suite of espionage capabilities, including keylogging, screen capture, file collection, and credential harvesting.
The effectiveness of this attack lies in the "blind spot" it exploits. CrowdStrike’s Falcon sensor, like most Endpoint Detection and Response (EDR) solutions, relies on the operating system being active and the security agent running to monitor for threats. Because the compromise occurred at the firmware level, it remained undetected while the laptop sat closed and powered off.
"We have the visibility once the machine boots up," Meyers explained to VentureBeat. The gap in security exists during the hours between the initial USB write and the next time the executive logs in. It is during this window that the implant, dormant but present, waits to be executed. This level of sophistication highlights a critical failure point in modern corporate security: the assumption that a device is secure simply because it is protected by software-based EDR or Multi-Factor Authentication (MFA).
Meyers noted that he believes China’s Ministry of State Security is the entity behind OVERCAST PANDA. The individuals responsible for the physical room entries are likely officers, intelligence agents, or potentially hotel staff who have been bribed or coerced into facilitating the intrusions. Targeting an agricultural conference is consistent with broader economic and industrial intelligence collection priorities frequently observed in China’s five-year plans.
Why Conventional Security Tools Struggle
The OVERCAST PANDA campaign underscores a significant challenge for modern security architectures. Existing tools are designed to combat threats that propagate through the network or the user interface. EDR needs the OS to be running; MFA requires a login attempt; and phishing training relies on the existence of an email. OVERCAST PANDA’s approach bypassed all these layers by operating at a point of entry that exists beneath the software stack. By the time the Falcon sensor picked up the FlowCloud process after the boot sequence, the malware was already deeply embedded in the system.
This physical-access strategy is particularly concerning because it is not easily scaled. While groups like REVENANT SPIDER—another adversary highlighted by CrowdStrike—can use artificial intelligence to compromise 17 victims with custom web shells in less than an hour, physical hotel room breaches are labor-intensive and high-risk. However, as Meyers pointed out, the fact that they are unscalable does not make them less dangerous; it simply means they are highly targeted. When a state intelligence service identifies specific executives at a specific conference as high-value targets, they are willing to deploy the necessary resources for a manual, physical operation that is virtually guaranteed to succeed against standard hardened laptops.
The Shift Toward Firmware and Policy Controls
Addressing this threat requires a departure from purely software-based solutions. While CrowdStrike has pioneered firmware attack detection and BIOS settings auditing within its Falcon platform—including integrations that allow organizations to surface BIOS verification telemetry—Meyers emphasized that the primary defense remains a matter of administrative policy and configuration rather than a product update.
The most effective safeguards are the "old and cheap" ones: disabling external boot options in the UEFI, setting a BIOS administrator password to prevent unauthorized changes, and enforcing pre-boot authentication. Pre-boot authentication, in particular, forces a human to supply a PIN or key before the encrypted storage volume becomes readable, rendering the machine significantly more resilient to unauthorized boot attempts from external media.
Furthermore, Meyers urged a pragmatic approach to international travel. "Don’t bring anything with you that you’re not comfortable with handing over to a foreign intelligence service," he cautioned. The security expert noted that he personally utilized temporary laptops and isolated email accounts during his own overseas travel, wiping the devices entirely upon his return. This strategy acknowledges the reality that customs officials and local actors in various jurisdictions may have the legal authority or physical capacity to compel access to any device brought across a border.
Organizational Fracture and the Future of Defense
The difficulty in mitigating these attacks often stems from organizational silos. In many large enterprises, the team responsible for endpoint security (the EDR team) is separate from the team managing BIOS configurations on travel laptops, which in turn is separate from the department handling identity governance. When these groups do not coordinate, gaps emerge—such as an executive carrying a machine with production access to an international conference without proper firmware locks.
As CrowdStrike continues to integrate new AI-driven tools like SafeMind and Falcon Guardian into its ecosystem, the focus remains on securing the runtime environment of AI agents and cloud workloads. These innovations are critical for defending against the surge in AI-powered, network-based eCrime, which remains a more frequent and scalable threat to the average enterprise.
However, the OVERCAST PANDA incident serves as a stark reminder that the digital and physical worlds remain inextricably linked. While cybersecurity leaders are busy deploying the next generation of AI-security products to combat automated threats, state actors are still finding success with the timeless, manual tradecraft of entering a hotel room and booting a laptop. For the executive traveler, the ultimate security barrier is not a software update, but the disciplined application of firmware policies and the strategic decision to leave sensitive data behind. As the security industry evolves to meet the challenges of the future, it must ensure that the foundational security of the hardware is not left in the past.