In the fast-paced ecosystem of cloud computing, the true measure of innovation is often found not in the sheer volume of new services, but in how effectively a platform can reduce the friction between a developer’s local environment and a live, production-ready state. Last week, Amazon Web Services (AWS) focused heavily on this philosophy, introducing tools designed to streamline deployment workflows and improve the economics of serverless computing. While these operational updates captured the attention of developers looking for faster release cycles, the industry’s broader conversation shifted toward the governance of artificial intelligence. By mid-week, the discourse moved from the mechanics of deployment to the complex challenge of maintaining oversight as AI agents gain increasing levels of autonomy.
A New Era for Lambda: Introducing Web Functions
The headline announcement of the week is undoubtedly the introduction of AWS Lambda Web Functions. For years, the serverless paradigm has required developers to adapt their code to specific event-driven architectures. While powerful, this often meant rewriting standard web applications into event handlers, creating a layer of abstraction that could complicate the migration of existing codebases. Lambda Web Functions effectively removes this hurdle, offering a new form factor that allows developers to run a standard HTTP web application directly on Lambda without the need for cumbersome adapters.
This shift is significant for teams building with frameworks such as Express, Hono, Fastify, or Next.js. The process is remarkably streamlined: developers can take a server that already listens on a port, execute a simple aws lambda-web deploy command, and receive a live HTTPS URL in under a minute. By eliminating the requirement for pre-configured infrastructure or complex framework-specific adapters, AWS is lowering the barrier to entry for serverless deployments. Lambda now supports three distinct form factors—all running on the secure, high-performance Firecracker isolation technology—that can compose within a single application: Event Functions for asynchronous processing, Web Functions for user-facing layers, and MicroVMs for stateful sandboxes designed to execute untrusted code.
Beyond the ease of deployment, there are technical refinements that make this more than a simple repackaging of existing capabilities. A standout feature is the concurrency model; each execution environment is now capable of handling up to 128 concurrent requests. This allows a burst of incoming traffic to share warm environments rather than forcing a one-to-one mapping between a request and an environment. Furthermore, the billing structure has been optimized to track the CPU time that code actually consumes, rather than billing based on wall-clock time. For developers working on API backends, server-side rendering, or inference endpoints that stream tokens—where a significant portion of latency is simply waiting for external processes—this change in the underlying economic model is substantial.
The deployment experience has also been modernized for global scale. By adding a simple --regions flag to the existing deploy command, developers can replicate their code across multiple geographic regions, automatically configuring latency-based routing behind a single, unified global URL. To facilitate safer releases, AWS has also included support for traffic splitting, allowing for canary rollouts based on weighted traffic distribution. Currently, the service is available in five regions, running on Node.js 24 with Arm64 architecture and native VPC connectivity. CloudFront integration is also live, enabling developers to use a Web Function endpoint as an origin, complete with origin access control for enhanced security.
Navigating the Future of Autonomous Agents
While the technical advancements in Lambda aim to make development faster and more efficient, the latter half of the week saw a pivot toward the critical subject of AI safety and governance. As organizations continue to integrate AI agents into their workflows, the question of how to manage autonomy without sacrificing control has become a central concern. A recent analysis, Trust in Depth: Giving Agents More Autonomy Without Losing Control, highlights a common trap: the "human-in-the-loop" model, which works well during small-scale testing but often fails as the system grows.
The challenge, as identified by the report, is that human operators, when tasked with checking every single action taken by an agent, eventually experience fatigue and stop effectively catching critical errors. To solve this, AWS proposes a more robust framework centered on four distinct pillars: scope, know, bound, and observe. This approach moves the security boundary outside the agent’s own reasoning. Because an agent cannot be expected to disable a security control that it is responsible for operating, the governance must be enforced at the gateway level.

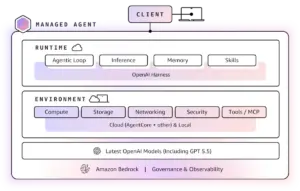
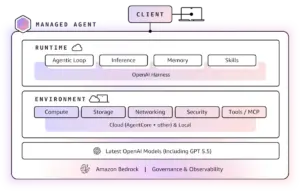
The proposed solution involves utilizing Amazon Bedrock AgentCore policies to govern agent behavior. By offloading the enforcement of rules to the infrastructure layer, organizations can ensure that their AI agents operate within defined parameters, regardless of the complexity of the tasks they perform. This approach leverages the same automated reasoning technology that AWS has refined over the past decade—the same technology that currently supports the massive scale of AWS Identity and Access Management, which processes over 2.1 billion requests per second. The argument here is compelling: instead of relying on the agent’s internal logic to police itself, the responsibility should reside in the robust, time-tested policy engines that define the rules of the cloud environment.
Bridging the Gap Between Code and Capability
The overarching theme of the past week was the continued convergence of developer productivity and system reliability. By making it easier to deploy code via Lambda Web Functions, AWS is addressing the "velocity" side of the equation—shortening the distance between a local development environment and a production endpoint. By introducing more sophisticated policy enforcement for AI agents, they are addressing the "stability" side, ensuring that as systems become faster and more autonomous, they remain secure and within the bounds of organizational policy.
These developments underscore a shift in how developers interact with cloud providers. It is no longer just about provisioning virtual machines or managing containers; it is about utilizing high-level abstractions that handle the complexities of concurrency, regional replication, and security policy enforcement automatically. For the average developer, this means spending less time managing the infrastructure and more time refining the business logic that provides value to their users.
As the industry continues to push the boundaries of what is possible with cloud-native architectures, the focus will likely remain on these dual goals of simplifying operations and hardening security. The new capabilities in Lambda and the evolving strategies for agent governance suggest that AWS is positioning its platform not just as a collection of services, but as an integrated environment that anticipates the operational needs of modern software engineering.
For those looking to stay informed on these rapid developments, the What’s New with AWS page remains the primary source for comprehensive updates on all service launches and feature enhancements. Additionally, the AWS Builder Center continues to serve as a hub for developers to connect, share their solutions, and access the documentation and resources necessary to implement these new tools effectively. As the cloud continues to evolve, keeping pace with these changes is essential for any team looking to maintain a competitive edge in their deployment and security practices.
The recent updates are a reminder that even mature platforms like AWS are constantly reinventing the core primitives of computing. Whether it is through the new form factors in Lambda or the sophisticated governance models for AI agents, the goal remains the same: to provide builders with the tools they need to operate at scale, while ensuring that the infrastructure remains both agile and secure. As always, the community can look forward to further refinements and new features as these services continue to mature in the coming months.