For decades, passwords have served as the cornerstone of digital security, despite being a persistent source of friction for both users and service providers. Remembering complex strings of characters, managing password fatigue, and constantly mitigating the risks of phishing attacks and credential stuffing have long burdened developers and consumers alike. Passwords require users to memorize secrets and demand that service providers maintain complex hashing, salting, rate-limiting, and recovery flows. Fortunately, the technology industry is increasingly embracing passkeys as a modern alternative, allowing individuals to confirm their identity through established device authenticators such as fingerprints, facial recognition, or screen lock PINs.
Recent technical documentation and implementation guides emphasize how passkeys eliminate shared secrets entirely by leveraging public-key cryptography. Instead of transmitting a vulnerable password across the internet, a user’s device signs a cryptographic challenge using a private key securely stored locally. The server merely stores a public key, meaning that even a catastrophic database breach exposes no data that can be used to compromise user accounts. Developers looking to adopt this paradigm can build robust passwordless architectures using modern web frameworks, pairing a NestJS backend utilizing PostgreSQL with a Next.js frontend driven by TypeScript and the SimpleWebAuthn library.
The fundamental limitations of traditional password-based authentication have driven the urgent need for this cryptographic evolution. Phishing attacks remain one of the most pervasive threats, as malicious actors easily replicate legitimate login portals to intercept human-entered secrets. Even technically savvy individuals can fall victim to sophisticated spear-phishing campaigns delivered via urgent emails or text messages. Furthermore, credential fatigue forces widespread password reuse. Because users maintain dozens or hundreds of online accounts, a single data leak at an obscure forum frequently leads to automated credential-stuffing attacks that compromise high-value targets like email accounts and financial institutions.
Beyond user-facing vulnerabilities, passwords impose significant architectural burdens on development teams. Securing database tables requires meticulous implementation of salted hashing algorithms, rate limiting, and proactive monitoring for leaks. Passwords also fail to provide adequate privacy, as users pass identical secrets to countless third-party platforms, trusting those entities with sensitive data that can later be cross-referenced across breaches. The constant cycle of forced password resets, security questions, and verification codes ultimately degrades user engagement, leading to high drop-off rates during registration and increased customer support overhead.
Passkeys resolve these foundational security challenges by fundamentally shifting where trust resides. Rather than relying on human vigilance to spot fraudulent URLs and create strong credentials, passkeys rely on the browser and operating system to enforce domain boundaries. Browsers and operating systems automatically restrict passkeys to the exact domain that created them, rendering phishing pages completely ineffective regardless of how visually convincing they may appear. Every passkey generates a unique key pair per site, eliminating reuse entirely. Furthermore, biometric data such as fingerprints and facial scans never leave the user’s local device.
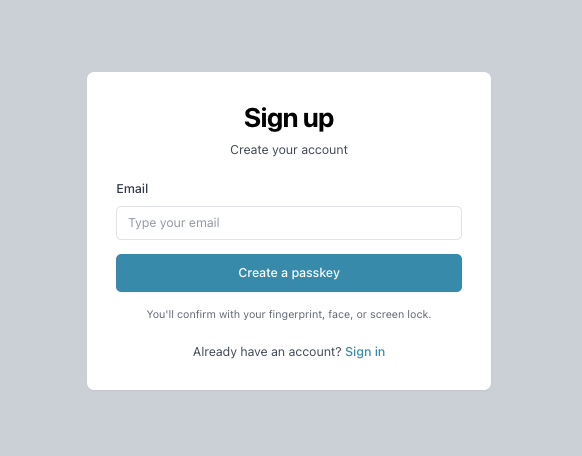
Implementing passkey architecture involves understanding the underlying mechanics of the Web Authentication API, commonly known as WebAuthn. Standardized by the W3C and supported across all major browsers, WebAuthn powers both registration and authentication ceremonies through a reliable three-step pattern. During registration, the user’s device generates a new public-private key pair, retaining the private key securely while sending the public key to the server for future validation. During authentication, the device signs a fresh server-generated challenge using its private key, and the server verifies the resulting signature against the stored public key.
Security architects implementing these systems must carefully navigate several critical implementation details to avoid subtle vulnerabilities. For instance, the relying party identifier, or RP ID, designates the specific domain to which passkeys belong, anchoring the cryptographic verification to prevent cross-site misuse. Additionally, developers must correctly evaluate the user verification flag within signed responses, ensuring that local biometric or screen-lock checks genuinely occurred rather than relying solely on simple user presence detections. Proper handling of database fields, such as ensuring unique constraints on user handles and clearing expired authentication challenges safely, remains vital to maintaining system integrity.
As the software development community continues to transition away from legacy credentials, adopting WebAuthn standards provides a clear pathway toward more secure, user-friendly digital ecosystems. Complete implementations demonstrate that modern frameworks like NestJS and Next.js can seamlessly integrate cryptographic authentication without sacrificing developer velocity or user experience. While passwords will likely persist in legacy systems for some time, the widespread hardware support for passkeys ensures that developers now possess the necessary tools to build inherently phishing-resistant applications for the modern web.