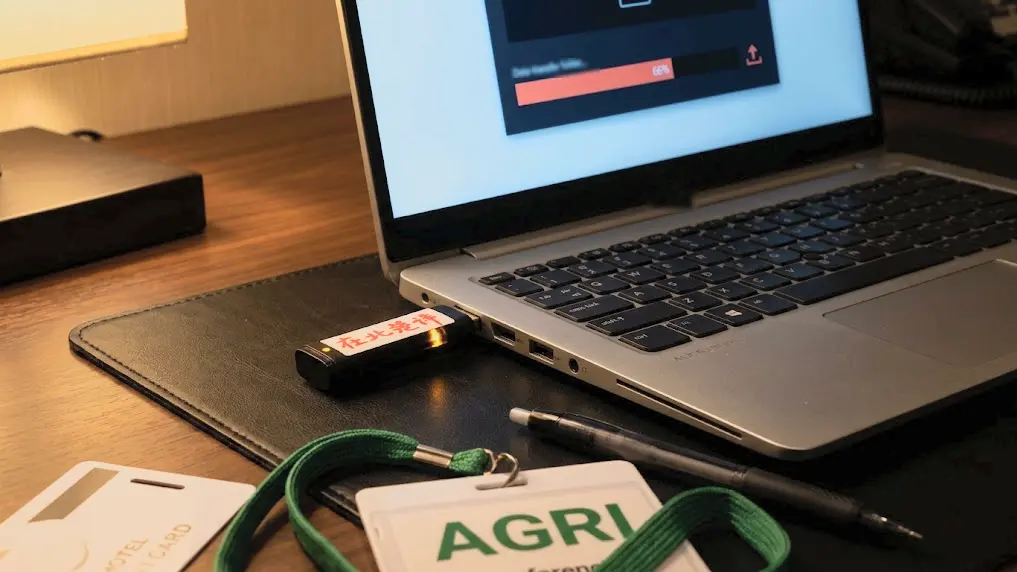
A state-linked Chinese hacking group, identified by security firm CrowdStrike as OVERCAST PANDA, has been linked to a sophisticated physical-access campaign that bypassed traditional network security by compromising executive laptops directly inside hotel rooms. Rather than relying on the common digital vectors of phishing or network breaches, the threat actors targeted executives attending an agricultural industry conference on Hainan Island this past spring, gaining physical access to their devices while the victims were away at dinner.
The operation, detailed in CrowdStrike’s 2026 Threat Hunting Report, highlights a growing concern among cybersecurity experts: the vulnerability of high-value targets to physical tampering in regions where state intelligence services can exert influence over hotel security or staff. According to Adam Meyers, CrowdStrike’s senior vice president of counter-adversary operations, the timeline of the intrusions was precise. In one instance, an intruder entered a hotel room at approximately 8 p.m. local time, followed by a second breach at another room at 9:57 p.m.
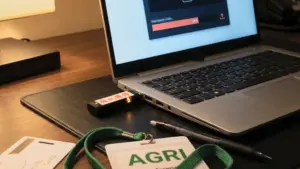
Once inside, the operatives did not attempt to bypass login screens or crack passwords. Instead, they booted the machines from a USB stick, injecting a backdoor known as FlowCloud directly into the laptops’ storage before rebooting the systems and exiting the rooms. This method left no traces of network intrusion, no phishing emails, and no stolen credentials that would typically alert traditional security monitoring systems. The campaign, which took place between March and May 2026, represents a rare but highly effective form of espionage that circumvents the very layers of security—such as Endpoint Detection and Response (EDR) and Multi-Factor Authentication (MFA)—that modern enterprises rely upon.
The Return of the ‘Evil Maid’ Attack
The technique employed by OVERCAST PANDA is known in cybersecurity circles as an "evil maid attack," a term popularized in 2009 by security researcher Joanna Rutkowska. The concept involves an attacker gaining physical access to an unattended device, typically in a hotel room, to compromise it while the owner is away. While physical-access operations remain rare among the 290 adversaries tracked by CrowdStrike, the tactical innovation here lies in the combination of state-backed intelligence gathering with specialized malware deployment.
Unlike the common tactics used by groups like MUSTANG PANDA, which often rely on victims accidentally plugging in a malicious USB stick, this operation was proactive. The intruders bypassed the need for user interaction by booting the machines into an alternative environment, ensuring that the malware would execute automatically the next time the executive logged in. Once the laptop was powered on the following morning, the trigger fired, initiating FlowCloud—a backdoor that has been in circulation for years. First documented by Proofpoint in 2020 during attacks on U.S. utilities and later tracked by NTT Security in Japanese organizations, FlowCloud is capable of extensive surveillance, including keylogging, screen capture, file collection, and credential harvesting.
Meyers noted that while CrowdStrike’s Falcon sensor is highly effective, its visibility is dependent on the operating system being fully loaded. The window of vulnerability, therefore, exists between the moment the USB is inserted and the moment the user resumes their session. During these hours, the device sits in a compromised state, entirely undetected by software-based security agents.
Why Existing Security Tools Missed the Breach
The success of the OVERCAST PANDA campaign underscores a significant gap in modern enterprise security strategies. EDR platforms are designed to monitor activities occurring within the operating system; MFA is designed to thwart unauthorized logins; and phishing training aims to change user behavior. Because this breach occurred below the level of the OS and the authentication stack, these defenses were effectively bypassed.
Meyers suggested that the sophistication of the operation likely points to China’s Ministry of State Security (MSS). He hypothesized that the individuals carrying out the room entries were likely intelligence officers or hotel staff who had been compromised, bribed, or compelled to cooperate. This tradecraft was not limited to the agricultural conference; a separate incident in mid-2026 involving a U.S.-based media professional suggested a broader pattern of physical targeting. The selection of an agricultural conference as a venue is particularly telling, as it aligns with the collection priorities outlined in China’s national five-year plans.
Shifts in Cybersecurity and the Role of AI
The disclosure of these findings coincided with CrowdStrike’s annual Fal.Con 2026 conference in Las Vegas, where the company unveiled a new suite of AI-driven security products, including Falcon Guardian, SafeMind, the Agentic Identity Provider, and AI Gateway. Nvidia CEO Jensen Huang joined CrowdStrike CEO George Kurtz on stage to demonstrate SafeMind, an agentic system built on Nvidia’s Nemotron open models, designed to synthesize threat data into actionable security responses.
Despite the focus on AI, CrowdStrike’s report highlights that the threat landscape is evolving in two distinct directions. While network-based threats—such as those posed by AI-enabled eCrime groups—are surging, the physical-access threat remains a potent weapon for state actors. According to the report, AI agent-triggered detections grew at 2.5 times the rate of human-triggered leads, and cloud-conscious eCrime activity saw a 171% increase. Furthermore, vishing attacks doubled in the first half of 2026, with groups like SNARKY SPIDER successfully moving from initial compromise to full data exfiltration in less than five minutes.
These trends highlight a clear dichotomy in modern cyber warfare: network-based attacks are designed for scale, while physical-access attacks are designed for precision. Meyers acknowledged that while network-based intrusions are more concerning for the average enterprise due to their ability to impact thousands of machines simultaneously, the hotel-room operations represent a targeted, high-impact strategy that conventional network defenses are simply not built to stop.
Firmware and Policy: The Last Line of Defense
For security leaders, the solution to this physical threat is well-established but frequently ignored due to the "inconvenience" it poses to end-users. CrowdStrike has offered firmware attack detection and BIOS settings auditing via its Falcon sensor for years, but the implementation of these tools often falls through the cracks of organizational silos.
Preventing such attacks requires a return to fundamental security hygiene. Disabling external boot capabilities in the UEFI/BIOS settings and setting a strong BIOS administrator password are among the most effective deterrents. Furthermore, the use of full-disk encryption coupled with pre-boot authentication—which requires a PIN or a hardware key before the system can even load the OS—prevents attackers from accessing the storage volume even if they gain physical control of the device.
Meyers emphasized that the most critical defense is a change in organizational mindset regarding international travel. "Don’t bring anything with you that you’re not comfortable with handing over to a foreign intelligence service," he advised. He recommended that companies adopt a policy of issuing "travel-only" laptops and mobile devices for international conferences—devices that contain no saved credentials, no access to production systems, and no persistent VPN configurations.
The OVERCAST PANDA operation serves as a stark reminder that as digital defenses become more advanced, state actors will continue to seek out the "weakest link," which often remains the physical device itself. While companies rush to secure AI agents and cloud workloads, the vulnerability of a laptop sitting in a hotel room remains a persistent risk for those who fail to implement basic firmware-level controls. For many organizations, the question is not whether they have the technology to stop such an attack, but whether they have the discipline to enforce the necessary policies before their executives board their next international flight.