Authorities in the Netherlands have apprehended a 24-year-old man, a previously convicted cybercriminal, on serious allegations that he provided critical support to the notorious hacker collective known as "ShinyHunters." The arrest, which took place in mid-September 2026, has sent shockwaves through the international cybersecurity community, triggering a volatile escalation in activity from the group’s remaining members. In a dramatic display of defiance, the group has launched high-profile attacks against the U.S. Federal Bureau of Investigation (FBI) and even targeted the Russian-based ransomware syndicate Cl0p.
The Double Life of "Umbreon"
According to multiple sources with direct knowledge of the investigation, the individual taken into custody is Pepijn van der Stap, a resident of the Dutch cities of Almere and Lelystad. Van der Stap is a familiar figure to law enforcement; he was previously convicted in 2023 for a sprawling series of data thefts and extortion schemes that prosecutors estimated generated between €1.5 million and €2.7 million.
During his 2023 trial, van der Stap provided a candid—and chilling—glimpse into his fractured identity. He described a "Dr. Jekyll and Mr. Hyde" existence, balancing a legitimate career in cybersecurity with a clandestine life of digital crime. Under the hacker alias "Umbreon," he routinely extorted victims and leaked their sensitive information on prominent, albeit now-defunct, English-language hacking forums such as RaidForums and Breached. By day, however, van der Stap maintained the appearance of a dedicated professional, working as a software engineer at the Amsterdam-based startup Hadrian and contributing his technical expertise to the Dutch Institute for Vulnerability Disclosure (DIVD), a respected nonprofit security research group.
Van der Stap eventually confessed to his role in the data theft campaigns and received a four-year prison sentence, with one year suspended. Throughout his legal ordeal, he requested to remain in custody rather than returning home, citing his inability to access adequate treatment for complex psychological issues, including post-traumatic stress disorder (PTSD) stemming from childhood trauma. He was ultimately released from prison in December 2025.

In an interview with KrebsOnSecurity on September 9, 2026, just days before his current detention, van der Stap presented himself as a reformed individual committed to making positive contributions to society. At the time of the interview, he was employed as the offensive security lead at the Dutch firm Neo Security. When reached for comment regarding the recent developments, Neo Security did not provide a statement. Van der Stap had previously indicated that he was navigating the aftermath of his past, including ongoing civil litigation and restitution efforts for his victims, but he ceased communication shortly after that interview, leading to concerns among his associates.
Escalating Tensions and the Odido Intrusion
The arrest of van der Stap, which reportedly occurred on or around September 16, followed a concerted effort by Dutch law enforcement to identify members of the ShinyHunters group. Dutch police had recently released a public appeal, sharing a recorded telephone call from February 2026 in which a Dutch-speaking member of the collective used sophisticated social engineering tactics to infiltrate Odido, the Netherlands’ largest mobile telecommunications provider. During that breach, hackers manipulated an Odido employee into authenticating on a spoofed website, subsequently harvesting data belonging to more than 6.2 million Dutch citizens.
ShinyHunters confirmed to local media that the individual heard in the audio clip was a member of their organization. In a brazen statement to the NL Times, the group pledged their full support—emotional, mental, and financial—to their arrested comrade, claiming they had already retained a criminal defense lawyer on his behalf. They dismissed the Dutch authorities as "incompetent" and "irrelevant," warning that the police would need significant luck to prevent further large-scale data thefts.
The FBI Breach and Oracle PeopleSoft Exploitation
The fallout from van der Stap’s arrest became immediately apparent when ShinyHunters claimed credit for a high-stakes breach of the FBI’s recruitment portal, apply.fbijobs.gov. Reports from 404 Media and Reuters revealed that the stolen data included Social Security numbers and personal identifiers for more than 5,000 FBI personnel. The compromised files were notably granular, containing sensitive psychiatric and medical records of staff members, as well as job titles identifying agents involved in major cybercrimes and international counter-intelligence operations. The FBI has officially confirmed the compromise of the portal.

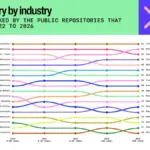
The group’s access to the FBI system, along with dozens of other organizations across sectors ranging from healthcare to agriculture, was facilitated by a vulnerability in Oracle’s PeopleSoft software (CVE-2026-35273). Although Oracle issued a patch for the flaw, ShinyHunters had been utilizing the exploit as a zero-day since June. Even after security firm Mandiant released web application firewall (WAF) rules to mitigate the risk, ShinyHunters bypassed these protections using URL-encoding techniques. A joint report from Mandiant and the Google Threat Intelligence Group confirmed the group’s mass exploitation campaign, which has successfully targeted a diverse array of industries.
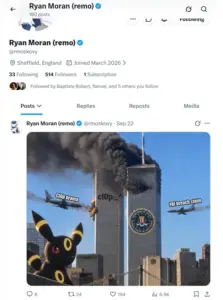
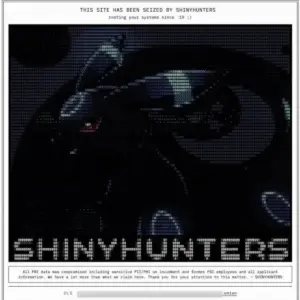
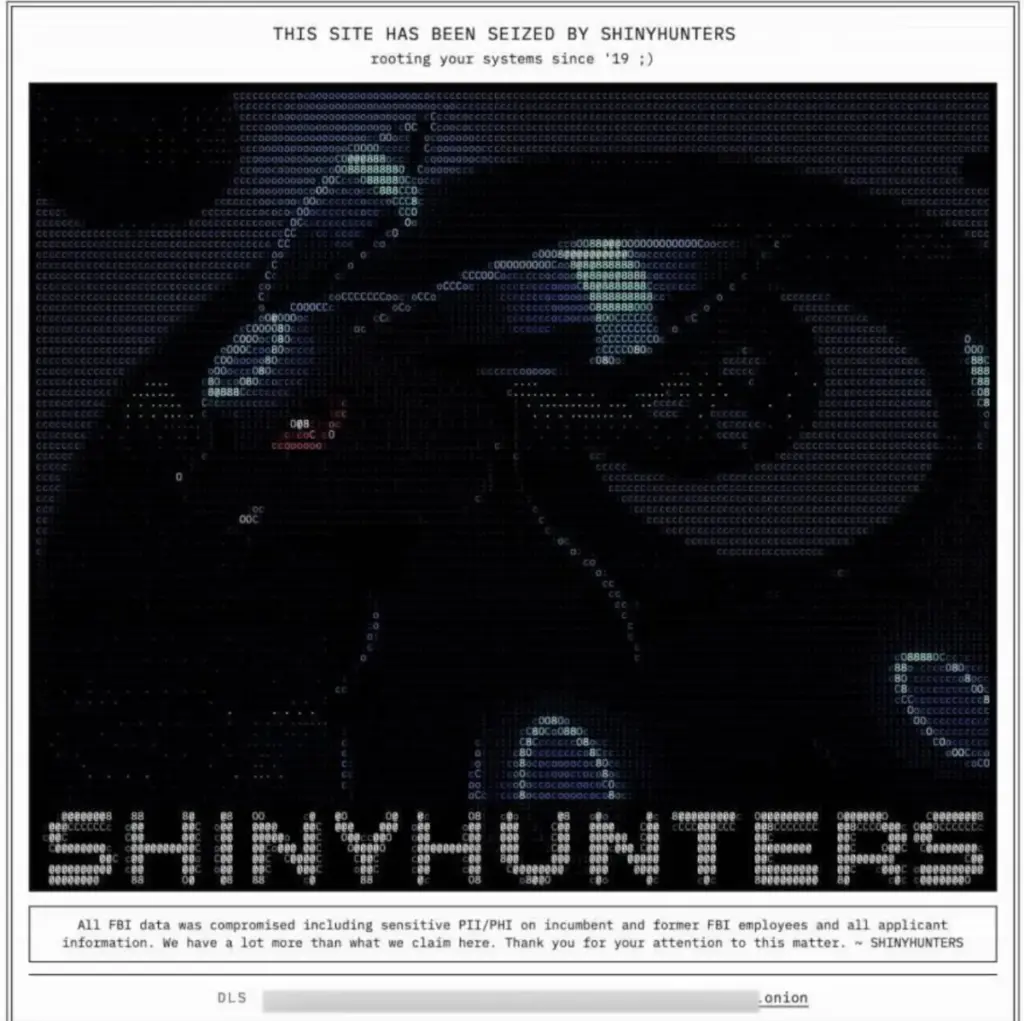
The "Umbreon" alias, previously associated with van der Stap, appeared prominently in the defacement of the FBI jobs site, where hackers left an ASCII art design of the Pokémon character. The message declared, "This site has been seized by ShinyHunters. rooting your systems since ’19 ;)." Security analysts note that this branding is identical to a defacement message used during the group’s 2020 hack of Hackforums, suggesting a deliberate attempt to link the FBI attack to the arrested Dutchman.
Internal Power Struggles and the Role of "Rey"
Sources familiar with the investigation into ShinyHunters suggest that the group’s recent, highly risky attacks signal a fundamental shift in strategy, likely driven by a change in leadership. Reports indicate that the group has fallen under the influence of a teenage cybercriminal based in Amman, Jordan, known by the handle "Rey." Rey is allegedly a key figure in a group called "ScatteredLapsussHunters" (SLSH), which functions as a conglomerate of the Scattered Spider, LAPSUS$, and ShinyHunters gangs.
There is significant evidence of "bad blood" between Rey and van der Stap regarding control over the ShinyHunters brand and its vast repository of stolen data. Observers suggest that the inclusion of the "Umbreon" image in the FBI site defacement was a strategic maneuver by Rey to frame the Dutch suspect for the high-profile breach.

The complexity of these alliances is further highlighted by the group’s prior collaboration with "TeamPCP," a supply-chain hacking group. According to reporting by Wired, the partnership soured when ShinyHunters allegedly went rogue, monetizing stolen credentials without sharing the proceeds with their partners. This infighting, combined with Mandiant’s covert infiltration and systematic invalidation of stolen credentials, has created a climate of intense paranoia and retaliation within the cybercrime underground.
Legal and Personal Consequences
As of late September 2026, the investigation into van der Stap has taken an even more severe turn. Reports from the Dutch news outlet RTL suggest that investigators are now probing allegations that the suspect attempted to orchestrate at least two murders, with indications that he may have issued orders for these crimes to be carried out abroad.
The FBI has responded to these developments with a stern warning. In a video message, Brett Leatherman, assistant director of the FBI’s Cyber Division, thanked the Dutch authorities for their cooperation and extended a pointed invitation to the remaining members of ShinyHunters. "Arrests have a way of changing who is willing to talk, and seized infrastructure has a way of showing us who’s left," Leatherman stated. "The longer you stay in this, the more we learn about you. You know how to find us, and we know how to find you. I suggest you reach out to us while the choice is still yours."
With van der Stap currently in custody awaiting court proceedings and the FBI intensifying its pursuit, the future of the ShinyHunters collective remains uncertain as the global hunt for its members continues.