When Nvidia’s long-standing Chief Security Officer, David Reber, quietly stepped down in August, the departure registered as a mere footnote in the tech industry’s relentless news cycle. Having served as the company’s CSO for four years and as a fixture at the semiconductor giant for seven, his exit appeared standard. Yet, in hindsight, the timing and the circumstances surrounding the leadership transition at one of the world’s most critical technology firms have taken on a far more ominous complexion.
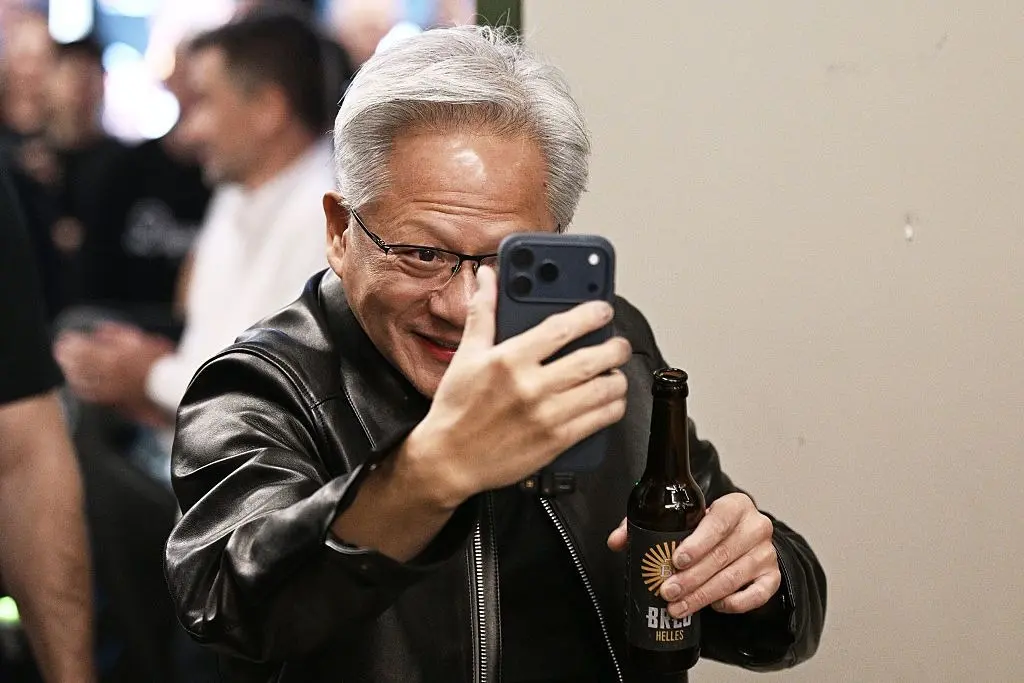
Just two and a half months after Reber’s departure, the corporate landscape at Nvidia was upended by the resignation of CEO Jensen Huang. His exit followed a mounting storm of controversy regarding his extramarital affairs—a scandal that began with reports of a relationship with an executive at Megaspeed, a Singapore-based data center company currently under scrutiny by U.S. investigators for its alleged role in funneling restricted Nvidia chips to China. The revelations did not stop there; subsequent reporting indicated additional affairs with at least two Nvidia employees, painting a picture of personal conduct that has invited intense scrutiny of the company’s internal governance and security posture.
At the time of his August resignation, Reber cited health reasons for his departure, disclosing a diagnosis of young-onset Parkinson’s disease that had been managed for over two years. "This wasn’t a pivot I had planned," Reber wrote in a LinkedIn post at the time. "But I know what needs to come first: family and health."
Reber’s successor, Saša Zdjelar, arrived with a pedigree of deep corporate experience, having spent 17 years at ExxonMobil, followed by a tenure at Salesforce and a stint at cybersecurity firm ReversingLabs. Despite the gravity of the unfolding situation, Zdjelar has remained silent, offering no response to inquiries regarding the transition or the extent of the security team’s awareness of the risks surrounding the CEO. Similarly, Nvidia has declined to comment on the matter, leaving a significant gap in the public understanding of how the company’s internal controls failed to flag or mitigate the potential exposure caused by Huang’s private life.
While there is no public evidence directly linking the security leadership turnover to the Megaspeed investigation or the CEO’s conduct, the coincidence has fueled speculation about the efficacy of Nvidia’s internal oversight. Relationships between a CEO and staff or external business partners typically fall under the purview of human resources, legal counsel, and the board of directors rather than the security department. However, security professionals argue that any such relationship—regardless of whether it occurs within the office or externally—creates a profound vulnerability. In the world of high-stakes corporate espionage, an affair provides a foreign intelligence service with immediate, high-leverage material that can be used to compromise an executive, forcing them into a position where they may be coerced into sharing sensitive information.
The situation with Megaspeed is particularly concerning because it transcends internal office dynamics. If an executive is entangled with a foreign entity that is already under federal investigation for potential sanctions violations, the risk of state-sponsored intelligence gathering becomes acute.
Identifying these risks, however, is a monumental challenge. According to Nicholas Eftimiades, a retired senior intelligence officer who has trained more than 1,000 corporate security professionals, the methodology employed by modern intelligence services relies less on high-tech digital hacking and more on the patient, subtle collection of information through everyday human interaction. This "human intelligence" approach makes it incredibly difficult for traditional corporate security teams—who are often geared toward preventing perimeter breaches or malware—to detect when an executive is being "cultivated" as an asset.
Evidence suggests that segments of the organization were aware of the volatility. Reports have confirmed that Nvidia’s legal department had been engaged with the government’s inquiry into Megaspeed for over a year. Furthermore, the nature of Huang’s relationships with staff—including a vice president who reported directly to him—was apparently an open secret among some colleagues. Yet, the critical question remains: did this information ever reach the security team? And if it did, were they empowered to act?
Eftimiades, author of the 2020 book Chinese Espionage Operations and Tactics, notes that security teams are frequently underfunded and marginalized within corporate hierarchies. Because security departments are viewed as cost centers rather than revenue generators, they often lack the leverage to challenge a powerful CEO. "It’s astonishingly common for CEOs to answer a security team’s warnings with ‘not a nickel more than compliance,’" Eftimiades observed.
This narrow view of security is a systemic issue across the industry. In a recent opinion piece for The Hill, Don Aviv, CEO of Interfor International, and co-author Jeremy Hurewitz argued that companies continue to focus too heavily on physical and cyber threats while neglecting the "insider threat" spectrum. They emphasized that security teams must broaden their scope to include the monitoring of suspicious business relationships, conflicts of interest, and the subtle cultivation of employees by foreign intelligence actors.
While it would be surprising if a company of Nvidia’s global influence did not have a more expansive security mandate, the possibility remains that the team was either kept in the dark or ignored. Intelligence operations, Eftimiades explains, function much like a biological virus. Once an asset is identified, the service begins to probe the organization’s soft points—the disagreements between a CEO and their board, for example, or the specific individuals pushing for or blocking policy changes. By identifying these "sticking points," intelligence services can tailor their pressure campaigns to extract the specific insights they need, such as shifts in export controls or sensitive technical roadmaps.
The playbook is well-documented, particularly regarding China’s intelligence gathering efforts. Eftimiades notes that any executive conducting significant business in the region is likely to have been approached at some point. Unlike the transactional, rapid-fire nature of Cold War espionage, modern intelligence cultivation is a long game, often spanning years rather than weeks. Intelligence services may use a variety of tools to augment this, including IMSI catchers—portable devices that mimic cell towers to intercept mobile communications. While there is no definitive proof that such technology was used against Huang, the threat is a constant reality in the current geopolitical climate.
As federal inquiries and the board-mandated independent investigation move forward, more details regarding the timeline of events at Nvidia are likely to emerge. The incident serves as a stark reminder of the limitations of traditional corporate defense mechanisms. For Eftimiades, the entire episode should be a "wake-up call" for the U.S. corporate sector, which he believes remains largely oblivious to the sophisticated tactics employed by foreign adversaries.
"We have lost trillions in intellectual property," Eftimiades said. "Whatever we think we’re doing isn’t working." As Nvidia grapples with the aftermath of its leadership crisis, the industry is left to wonder if the company’s internal safeguards were simply bypassed, or if the broader culture of corporate security failed to account for the most unpredictable variable of all: the human element. The investigation into the Megaspeed connection and the internal fallout of the CEO’s departure will likely define the company’s trajectory for years to come, serving as a cautionary tale for any firm that believes its walls are high enough to keep the outside world at bay.